Dell Connectivity Client Security
Summary
The Dell Connectivity Client enables connectivity and streaming telemetry from customer infrastructure to Dell Technologies. The primary uses of telemetry collection are to deliver a proactive service and support experience to Dell customers.
The content of the technical guide describes the security controls and policies that the Dell Connectivity Client (DCC) establishes to deliver secure and modern connectivity and telemetry streaming. The guide is intended to proactively address the security concerns many customers raise when adopting a new connectivity standard.
This technical document reviews:
- Dell Connectivity Client data collection
- Architecture overview and security controls
- Security and integrity standards of Dell Technologies
- Responsibilities associated with securing information through the Shared (Dell and End customer) Responsibility Matrix.
Security Assurance from Dell Technologies
Dell Technologies has taken steps to ensure program and application development teams follow a consistent methodology using an internal Secure Development Lifecycle (SDL) process. The SDL process from Dell Technologies integrates standards from a variety of data sources and is aligned with the Secure Software Development Framework (SSDF) and ISO/IEC 27034 information technology, security techniques, and the application security principles outlined in the NIST.
The SDL is a common reference for Dell product organizations to benchmark their secure development activities against market expectations and industry best practices. It defines controls that the Dell product teams must adopt while developing new features and functionality. The SDL includes both analysis activities and prescriptive proactive controls around key risk areas. The analysis includes activities such as threat modeling, static code analysis, scanning, and security testing. This analysis is intended to discover and address security defects throughout the development lifecycle. The prescriptive controls are intended to ensure development teams code defensively to prevent specific prevalent security issues, including those found in the OWASP Top 10 or SANS Top 25. Many of these activities are automated as part of the DevOps strategy to drive enforcement of SDL at scale.
Architecture Overview
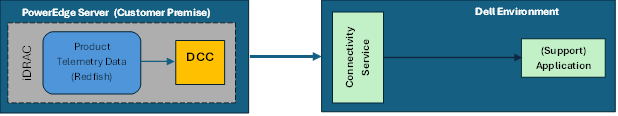
- iDRAC sending request to connect to Dell network via Dell Connectivity Client
Modularity: DCC needs a modular and composable architecture to support the footprint and configuration (including embedded, single node and cluster configurations).
Dell Advisors and Partners
Data In Transit
DCC enables transmission of telemetry data including system data such as logs, alerts, health, performance and configuration information. No customer data is sent, only data generated by the customer’s systems. Customers can control which systems send information over these channels.
All data arriving through those channels is protected in transit by industry-standard best practices. Both channels use digital certificates and customer-controlled access policies to establish point-to-point encryption and ensure all data is securely transported to the Dell IT-managed infrastructure. Connection and access are performed over secured transport and presentation protocols – TCP, TLS 1.3, and HTTPS.
Data Collection
The Dell Connectivity Client (DCC) provides secure, bi-directional connectivity between Dell's network and PowerEdge servers running on customer premises.
- There are different types of information that are being collected and transmitted to Dell. No Personally Identifiable Information (PII) is being collected or transmitted to Dell.
- Full Config Snapshot – This is sent every day and includes a full Redfish Walk, transforming the Redfish data into OpenTelemetry (OTel) format.
- Config Change – This involves Redfish lifecycle events. For a given event, the DCC pulls back the Redfish and sends the changed object.
- Metric Payload – On startup, the DCC has a default configuration for the metric report definition. Once configured, Redfish streams the metrics to DCC, which is then transformed into an OpenTelemetry format and sent.
- Alert Stream –This is essentially a full Redfish event stream. Redfish emits this data, DCC converts it into OpenTelemetry format and sends it.
- SupportAssist Collection (SAC) Log – Known as the “Technical Support Report (TSR)”, DCC will collect logs daily and send them to Dell. In addition, Dell Support call request a TSR on-demand in response to a case being opened.
Roles and Responsibilities: Dell Support, Customers, & Partners
Security for DCC operates under a shared security model. Dell’s shared responsibility matrix clearly delineates the respective roles between customer and Dell on a function-by-function basis, as well as shared levels of responsibility.
- DCC Security – Dell owns the security of the Dell hosted infrastructure.
- Threat & Vulnerability assessment – Dell owns the threat and vulnerability assessment of Dell owned systems.
- Secure Development Lifecycle – Dell owns the secure development lifecycle of Dell owned systems.
- Firewall – Dell owns Dell premise firewall protection
- Device onboarding – Dell owns connectivity of Dell owned systems but works with customer on the onboarding of customer systems.
- Device maintenance – Dell owns maintenance of Dell owned systems or customer supported systems.
Table 1. DCC shared responsibility matrix
|
Category |
Customer |
Dell |
|
DCC Security |
|
✔️ |
|
Data Security/Protection |
✔️ |
✔️ |
|
Threat and Vulnerability Assessment of the DCC |
|
✔️ |
|
Secure Development Lifecycle |
|
✔️ |
|
Firewall |
✔️ |
✔️ |
|
Collector |
✔️ |
✔️ |
|
Device Onboarding |
✔️ |
✔️
|
|
Device Maintenance |
✔️ |
✔️
|
Security and Compliance
The Dell Connectivity Client protects Dell and Customer data utilizing policies and strategies from established frameworks. Where applicable, application and product development at Dell utilizes mappings to established frameworks and regulations to help ensure that appropriate security principles and requirements are reflected in the development lifecycle. The security measures that protect DCC map to industry-accepted security standards, regulations, and control frameworks.
- ISO 27001 Information Security Management Systems
- NIST Security and Privacy Controls for Federal Information Systems and Organization
- CSA Cloud Control Matrix
- SafeCODE
- For more information see the Security and Trust Center
Conclusion
Dell Technologies strives to create a security-aware culture across its entire community. Our internal SDL is a common reference for Dell Technologies’ product organizations to benchmark product and application secure development activities against market expectations and industry practices. It defines security controls that product teams should adopt while developing new features and functionality for our programs. Customers can be assured that Dell is committed to providing a reliable, private, and secure experience for DCC customers.
Glossary
Table 2. Glossary
|
Acronym |
Definition |
|
SDL |
Secure Development Lifecycle |
|
DCC |
Dell Connectivity Client |
|
NIST |
National Institute of Standards & Technology |
|
CSA |
Cloud Security Alliance |
|
ISO |
International Organization of Standardization |
|
OWASP |
Open Web Application Security Project |
|
SANS |
SynsAdmin, Audit, Network, and Security |
Notice
This technical guide is for informational purposes only and represents current Dell practices, which are subject to change without notice. It does not create any commitments or assurances from Dell and its affiliates, suppliers or licensors. Dell’s responsibilities and liabilities to its customers are controlled by Dell agreements which are neither a part of, nor modified by this whitepaper. Customers are solely responsible for making their own independent assessment of the information provided in this whitepaper.