NetWorker: How to Use NWUI
Summary: This KB article provides an overview of the NetWorker Web User Interface (NWUI). This is an HTML web-based NetWorker management interface that provides similar functionality as the legacy Java-based NetWorker Management Console. ...
This article applies to
This article does not apply to
This article is not tied to any specific product.
Not all product versions are identified in this article.
Instructions
Table of Contents
- Video
- What is the NetWorker Management Web User Interface (NWUI)
- How to Install
- How to Access
- How to Monitor
- How to Add the vCenter Server
- How to Install the vCenter Plug-in
- How to Add and Configure the vProxy
- Adding a NetWorker Client
- Adding a NetWorker Group
- Adding an Azure Subscription
- Adding an Azure Protection Client
- Adding a Pool
- Creating a Data Domain Device
- Creating a Protection Policy, Workflow, Action
- NVP-vProxy Recovery Operations
Refer to this video:
This video is also available on YouTube.
What is the NetWorker Management Web User Interface (NWUI)
This web interface uses HTML5, Apache Tomcat, REST API, and the Spring Framework to provide a superior user-experience through intuitive workflows and increased responsiveness. The NWUI can be installed on Linux or Microsoft Windows operating systems, either directly on the NetWorker server or on a host which is not the NetWorker server. Depending on the NetWorker version installed some features or functionalities may not exist. For additional information, see the NetWorker version-specific Administration Guides, available through: https://www.dell.com/support/home/product-support/product/networker/docs (you must sign-in with your Dell support account)
Expand each of the following sections for more details:
For full details about how to install the NWUI, see the following article: NetWorker: How to Install NWUI
NWUI supports the following browsers: Microsoft Internet Explorer 11; Google Chrome; Microsoft Edge; Mozilla Firefox.
- The UI can be installed either on the NetWorker Server or on the NetWorker Management Console server.
- It can be installed on Linux or Windows Operating Systems. See the NetWorker Compatibility Guides for a full list of supported platforms (Dell Support login may be required).
- The NetWorker Installation Guide provides full details on how to install the NetWorker Management UI on your chosen platform.
- Windows: Extract the executable and run the exe to launch the installation wizard. You may get a Security Alert, from which you must select:
'View Certificate'; 'Install Certificate'; 'Place all certificates on the following store'; 'Browse'; 'Trusted Root Certificate Authorities; 'Ok'; 'Yes'. - Linux: Extract using the '
tar' command and install using the 'rpm' command. There is a prompt to run a configuration script/opt/nwui/scripts/nwui_configure.shwhich runs through configuring the software.
- Windows: Extract the executable and run the exe to launch the installation wizard. You may get a Security Alert, from which you must select:
- As part of the installation, the authentication host is specified which points to a NetWorker server running the authentication service. The NetWorker Management Web UI uses NetWorker credentials for authentication. These are the same credentials as are used for the NetWorker Management Console (NMC).
Windows: Windows Services Manager Linux sysvinit: /etc/init.d/nwui start/stop/status Linux systemd: systemctl start/stop/status nwui - NWUI's default configuration uses self-signed certificates; however, these can be replaced with CA-signed certificates.
Accessing the NetWorker Management Web UI
- Access the NetWorker Management Web UI by going to the following address in a web browser:
https://<IP_address_or_hostname>:9090/nwui - Log in with a NetWorker user account and password.
Figure 1. NWUI login
NWUI is configured to use a specific NetWorker authentication (AUTHC) server during NWUI initial configuration: NetWorker: How To Identify Which Server is the Authentication Server Used By NMC and NWUI
The NWUI is accessible using AD/LDAP users once AD/LDAP external authentication is integrated with NetWorker.
How to Monitor
After logging in to NWUI you are presented with the main Dashboard. By default, the graphs shown give an overview of the Policy, Workflow, and Actions performed in the last 24 hours; however, the interval can be adjusted by clicking the 3 dots to the right of Last 24 hours. The dashboard also gives an overview of any Active Sessions (backups, clones, restores), and Alerts.
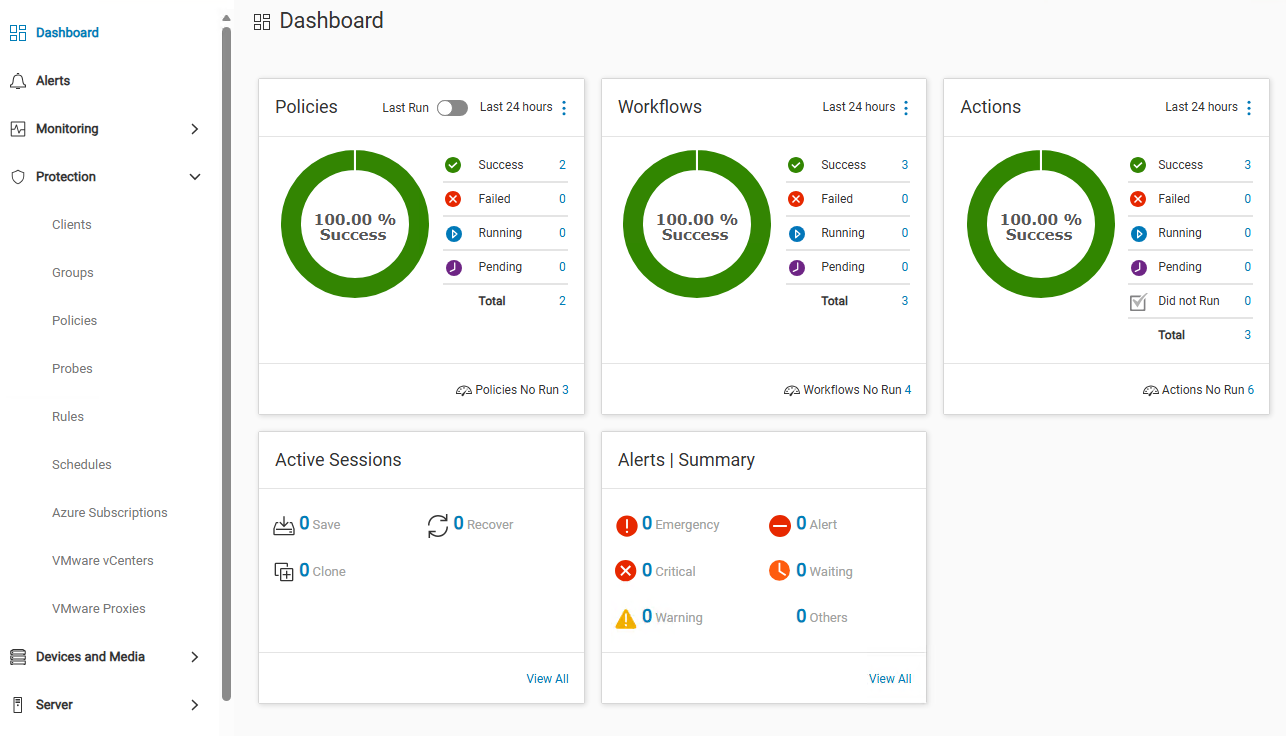
Figure 2. NWUI dashboard
You can click on the linked (blue) objects in the dashboard and they will take you to their respective Monitoring tabs (explained below).
To monitor any Alerts click on View all from the Dashboard -> Alerts | Summary window, or click on Alerts in the left menu:
Figure 3. NWUI Alerts
Expand the Monitoring tab in the left menu:
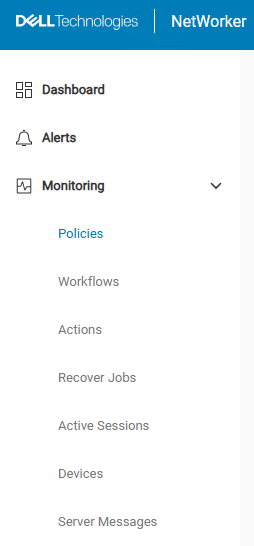
Figure 4. NWUI Monitoring
Each tab provides the following:
- Policies: an overview of completed or failed NetWorker protection operations at the Policy-level. In the NetWorker protection operation stack, Policies are the top container. A policy can contain multiple workflows. From the Policies tab, you can navigate further down through the Workflows and Actions.
- Workflows: an overview of NetWorker protection operations at the Workflow-level. In the NetWorker protection operation stack, Workflows are configured under a single policy. Multiple workflows may exist under a policy; the workflows determine the schedule (start times) of the workflow. Each unique workflow is associated with a specific NetWorker Group. Only one group can be assigned in a workflow; similarly, groups can only be assigned to one workflow. Groups are containers that contain resources to be protected (clients, VMs, so forth). A workflow may contain multiple Action (backup, clone, so forth). From the Workflows tab you can review the workflow logs or navigate further down into a Workflow's Actions.
- Actions: an overview of NetWorker protection operations at the Action-level. In the NetWorker protection operation stack, Actions are the bottom stack. Policy -> Workflow -> Action. Multiple actions may be configured in a single workflow; for example, a workflow may be configured to perform a backup, then following the backup, clone (copy) the data to another device. The actions determine the backup level, parallelism, limits, and so forth. From the Actions tab, you can view each action's logs.
The Protection Policy, Workflow, and Action logs are found on the NetWorker server under the /nsr/logs/policy folder path. These logs follow the NetWorkerjobsdbretention (default 72 hours). After thejobsdbretention has passed, the logs are removed. - Recover Jobs: an overview of completed or failed NetWorker recover jobs. You can review logs from the recovery jobs completed.
- Active Sessions: an overview of any actively running NetWorker backup, clone, or recover session.
- Devices: An overview of devices configured on the NetWorker server showing: their status, media type, volume name, media pool, library (tape devices), and most recent message.
- Server Messages: Messages regarding the NetWorker server. These same messages can be found in the
/nsr/logs/daemon.rawon the NetWorker server.
- Expand the Protection drop-down in the NWUI menu.
- Go to VMware vCenters.
- Click +Add.
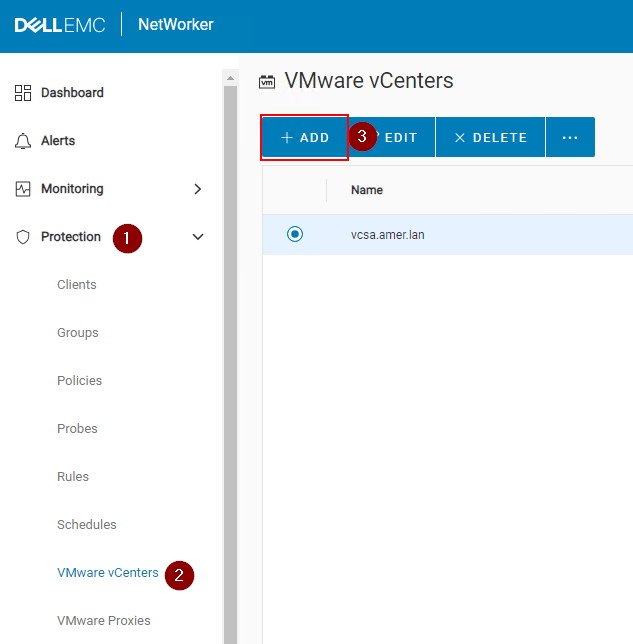
Figure 5. NWUI VMware vCenter Protection view
- In the Hostname field, specify the FQDN or IP address of the vCenter server. In the Username field, specify a vCenter user account that has permission to perform backups. In the Password field, specify the password for the vCenter user account. If the vCenter server is deployed in the Cloud, select the Deployed in Cloud checkbox. Click Save.
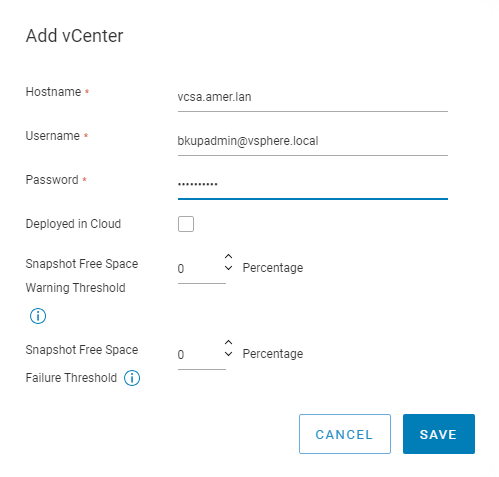
Figure 6. Adding a vCenter to NetWorker from NWUI
The NetWorker VMware Integration Guide details the permissions required by the vCenter user account, available through: https://www.dell.com/support/home/product-support/product/networker/docs (You must sign-in with your Dell support account).
- An entry for the added vCenter server appears automatically in the Protection window's VMware vCenters pane. If an entry for the added vCenter does not appear, click the Refresh icon.
- When you select one of the available vCenter resources, the vCenter inventory displays in the right pane of the window in a tree structure that allows you to view all virtual machines and entities, and select individual items to view the entity's properties.
- If you must edit the vCenter server properties, you can do so under Protection > VMware vCenters.
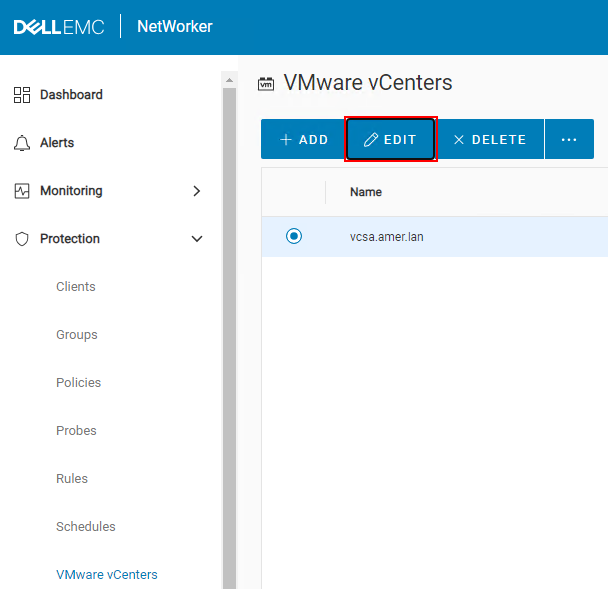
Figure 7. Editing a VMware vCenter from NWUI
The vCenter plug-in is optional, it is not mandatory for performing VMware backup and restore operations. It provides a backup/recover interface directly within the vSphere user interface.
The vCenter vSphere NetWorker plug-in is only supported when the vCenter was added to NetWorker using its FQDN or IP address. It does not support vCenters which were added using their shortname alias. NetWorker: vCenter plug-in and VCUI login fail with "vCenter not registered with NetWorker server".
- Expand the Protection drop-down in the NWUI menu.
- Go to VMware vCenters.
- Select the VMware vCenter you want to install the plug-in on.
- Click the ... option and select Install vCenter Plugin.
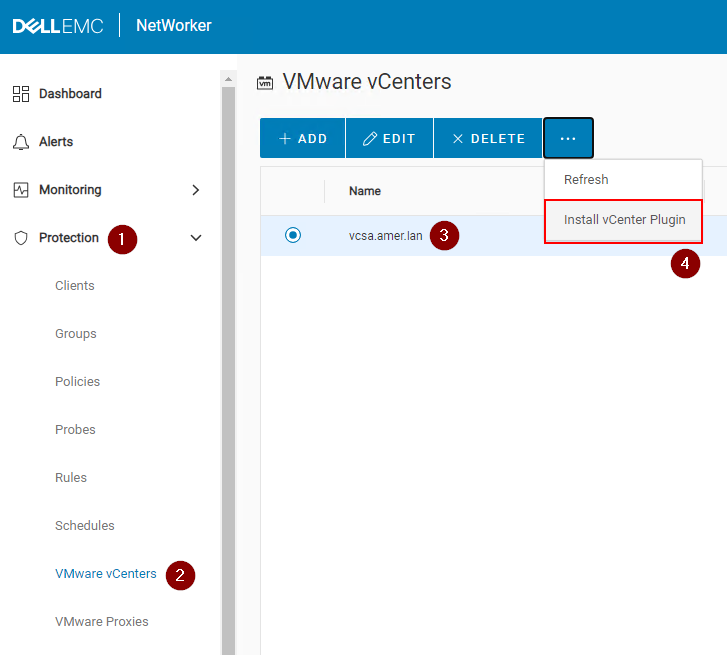
Figure 8. Installing the VMware vSphere NetWorker plugin from NWUI
- The default vCenter port used is
443. Specify the vCenter user account which has permissions to install the plug-in. Specify the vCenter user accounts password.
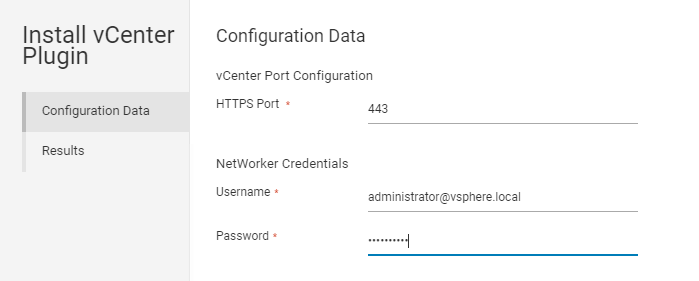
Figure 9. vSphere plugin installation options
- Click Install and monitor the results.
- Log in to the vSphere web client. The NetWorker plug-in is available from the home page.
For any issues observed during vSphere plugin installation, see: NetWorker: vCenter Plugin and User Interface (VCUI) Troubleshooting
- After deploying the OVA for the vProxy host, perform the following steps to add the vProxy by using the NetWorker Management Web UI.
See: NetWorker: How To Deploy NVP vProxy in VMware Environments - You must first have followed the above procedure to add the vCenter.
- In the left menu, expand the Protection drop-down.
- Go to VMware Proxies.
- Click +Add.
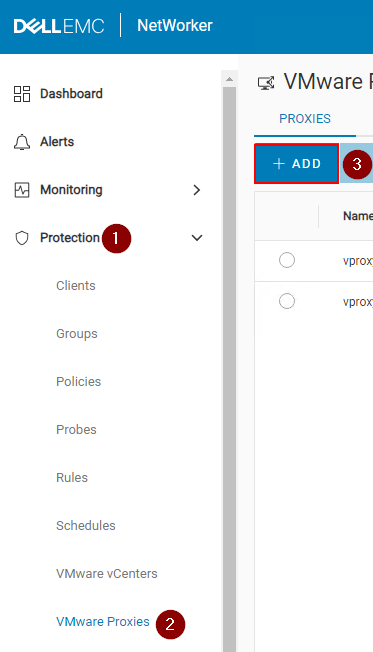
Figure 10. Adding a NetWorker VMware Protection (NVP) vProxy appliance from NWUI
- In the Selection page, ensure that the correct vCenter is selected. Click Select Proxies to select one or more vProxies.
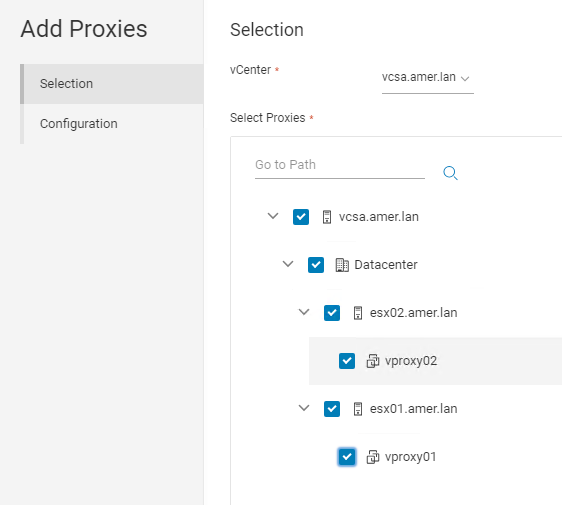
Figure 11. Adding a NetWorker VMware Protection (NVP) vProxy appliance from NWUI
- In the Configuration page, enter the vProxy admin user's password. Click Finish when ready to initiate registration.
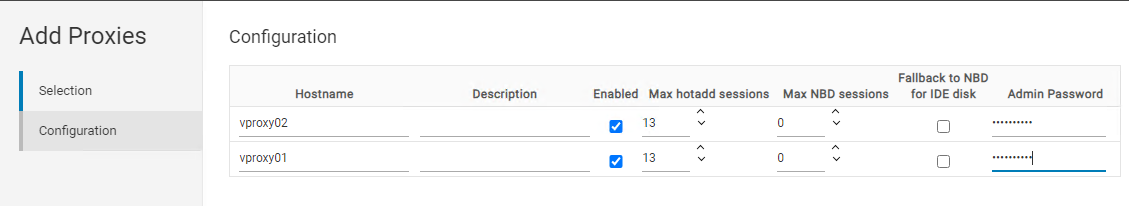
Figure 12. Adding a NetWorker VMware Protection (NVP) vProxy appliance from NWUI
For more information about Hot Add and NBD configuration options and best practices, see the NetWorker VMware Integration Guide, available through: https://www.dell.com/support/home/product-support/product/networker/docs. (You must sign-in with your Dell support account).
You can edit the properties of the vProxy, using the Edit icon in the Protection->VMware Proxies page.
The following procedure assumes that the target host already has the NetWorker client software installed and is ready to be added as a client resource within the NetWorker server configuration. If you have not installed the NetWorker client software, see the NetWorker Installation Guide, available through Support for NetWorker | Manuals & Documents. The NetWorker Compatibility Matrix details supported operating systems and configurations for NetWorker software.
This guide shows how to register a standard file system type client. For clients that require database or application specific backups, see the module specific documentation:
- Support for NetWorker | Manuals & Documents.
- Support for NetWorker Module for Databases and Applications | Manuals & Documents
- Support for NetWorker Module for MEDITECH | Manuals & Documents
- Support for NetWorker Module for Microsoft | Manuals & Documents
- Support for NetWorker for OpenVMS | Manuals & Documents
- Support for NetWorker Module for SAP | Manuals & Documents
NOTE: You must sign-in with your Dell support account to access the above links.
- Log in to NWUI.
- Go to Protection -> Clients.
- Click +Add.
- In the Basic Configuration tab, enter the following:
- In the Name field, enter the Fully Qualified Domain Name (FQDN) or short-name alias of the remote system.
- (Optional) in the Description field, add some information describing the client.
- (Optional) from the Restricted Datazone drop down, select a RDZ (if configured). Restricted Datazones (RDZ) allows NetWorker administrators to organize a NetWorker environment into a multi-tenancy configuration, providing the ability to add an extra layer of privilege control. For more information, see the NetWorker Administration and NetWorker Security Configuration guides.
- (Optional) Assign user-created Tags. Tags are environment-specific and used to group resources together, for example Sale, Support, so forth.
- (Optional) Select a Group you would like to add the client to. This does not need to be done during client creation; for example, if a group must also be created you can create the group later and add the clients to it.
- The Type drop-down has the Traditional option selected by default. Leave this as-is.
- (Optional) Select the Block Based Backup check box. During block based backups, the backup application scans a volume or a disk in a file system, and backs up all the blocks that are in use in the file system. See the Block Based Backup and Recovery chapter of the NetWorker Administration Guide for more details.
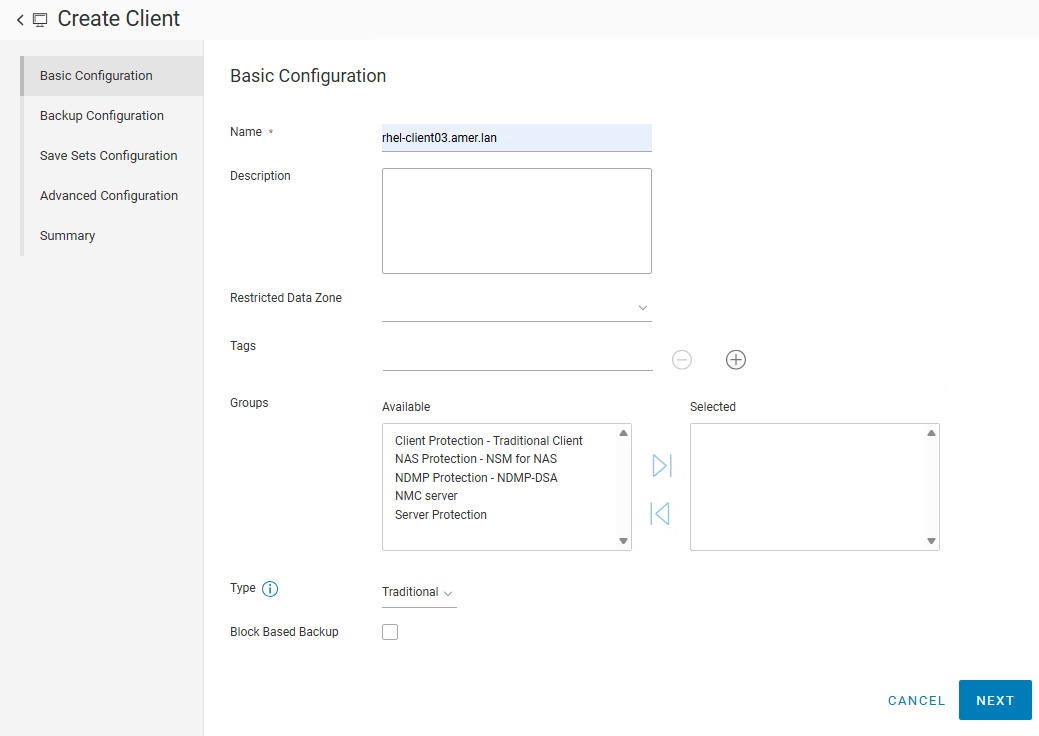
Figure 13. Basic Configuration Tab.
-
- Click Next.
- In the Backup Configuration tab confirm the client details and click Next.
NOTE: If the NetWorker server and client cannot communicate correctly, either name resolution or port issue, an error appears on this tab. See NetWorker: How to test communication through a firewall
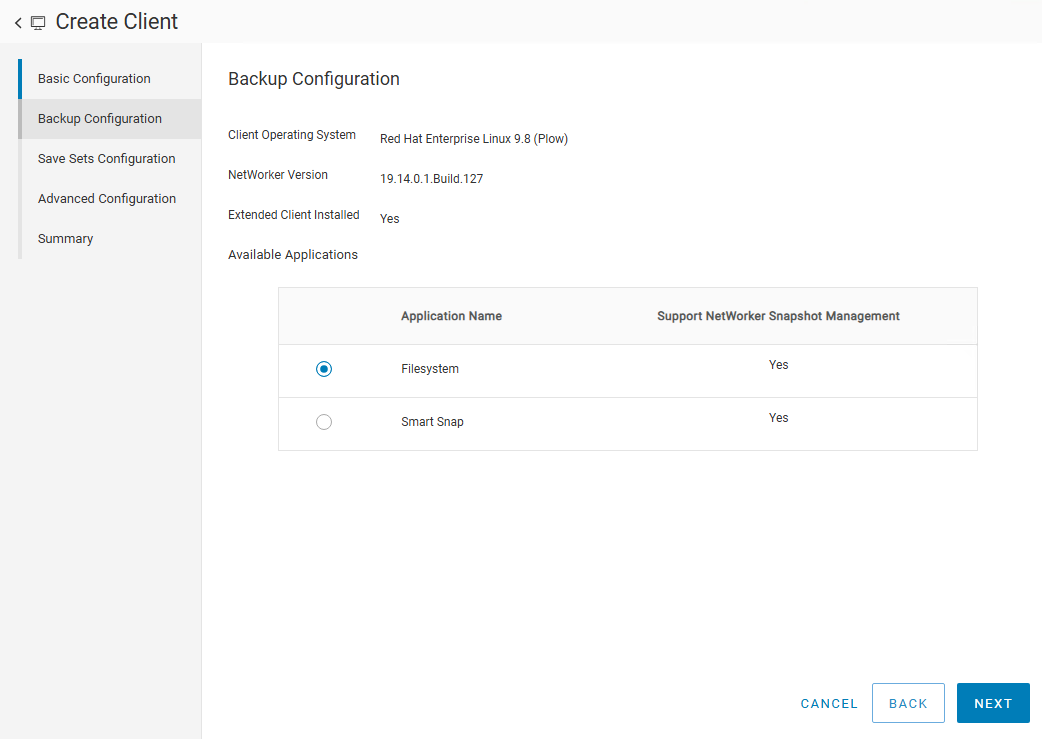
Figure 14. Backup Configuration tab.
- In the Save Sets Configuration tab, leave the All Save Sets option selected, or unselect the option and manually pick volumes, folders, or files to be backed up by the client. Then click Next.
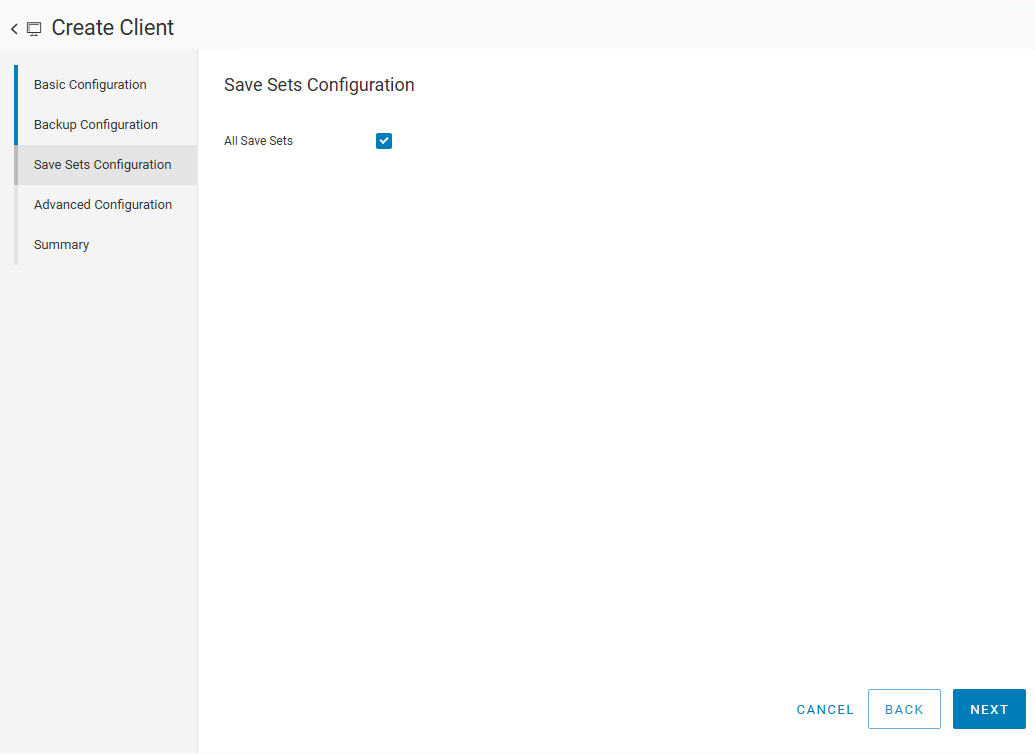
Figure 15. Save Sets Configuration tab.
- In the Advanced Configuration tab, click Next. Changing these options are not required for a standard file system backup. See the NetWorker Administration Guide for more information on these settings.
- On the Summary tab, confirm the settings and click Finish.
The client is now listed in the Protection -> Clients tab. It will show as Unprotected until it is added to a Group:
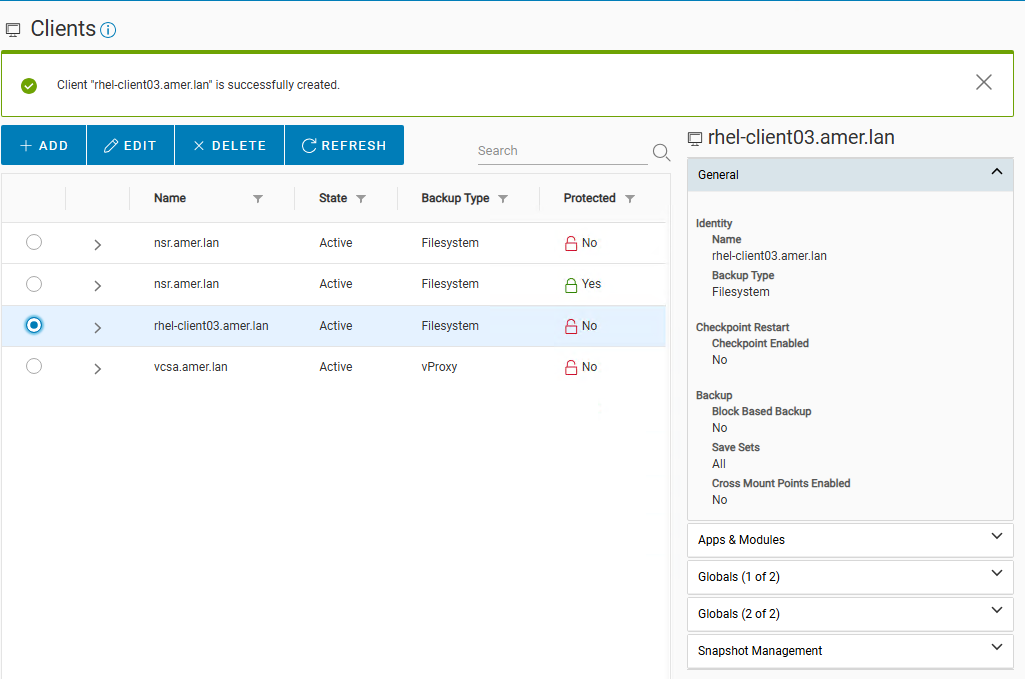
Figure 16: NetWorker Clients.
NOTE: After client creation, the client can be edited using the Edit option. Any of the settings defined (except for client name and backup type) can be modified after client creation.
Adding a NetWorker Group
NetWorker groups are logical containers for NetWorker clients or VMware Virtual Machines (VM). A group is assigned to a Protection Policy's Workflow to perform specific Actions at a specified start time.
- Log In to NWUI.
- Go to Protection Groups.
- Click +Add.
NOTE: An alternate method is to create the group while Creating a Protection Policy Workflow Action. The same steps shown below apply, but they appear during the workflow creation process. - In the Basic Configuration tab, provide the following:
- Enter a Name.
- (Optional) add a Description to describe the group's purpose.
- (Optional) from the Restricted Datazone drop down, select a RDZ (if configured). Restricted Datazones (RDZ) allows NetWorker administrators to organize a NetWorker environment into a multi-tenancy configuration, providing the ability to add an extra layer of privilege control. For more information, see the NetWorker Administration and NetWorker Security Configuration guides. Support for NetWorker | Manuals & Documents
- Select a Type (The option selected changes the remaining steps of the Group creation process):
- VMware: This option is used to select a NSR Hypervisor resource. VMware Virtual Machines are selected for protection in the group resource. This can be achieved through manual selection or dynamic rules: NetWorker: vProxy: How to enable a VMware group with Dynamic Association and Rules
- Save Set: This option is used when the intended purpose of the group is to be configured in a Clone (copy) based workflow.
- NAS Device: This option is used when performing backups of Network Attached Storage (NAS) devices using the Network Data Management Protocol (NDMP). See the Network Data Management Protocol User Guide for more information. Support for NetWorker | Manuals & Documents
- Client: This option is used when performing protection operations on traditional NetWorker clients.
- (Optional) Select a Protection Policy
- (Optional) Select a Workflow.
NOTE: A Group can only be assigned to a single Workflow; similarly, a Workflow can only have one group assigned. A Policy can contain multiple workflows. Groups can be assigned to a workflow during the Policy->Workflow creation process. See: Creating a Protection Policy, Workflow, Action - Click Next.
- As an example, after selecting Client, the Client Resources tab shows NetWorker clients that were previously registered with the NetWorker server. See Adding a NetWorker Client. Select clients that are to be protected by the group:
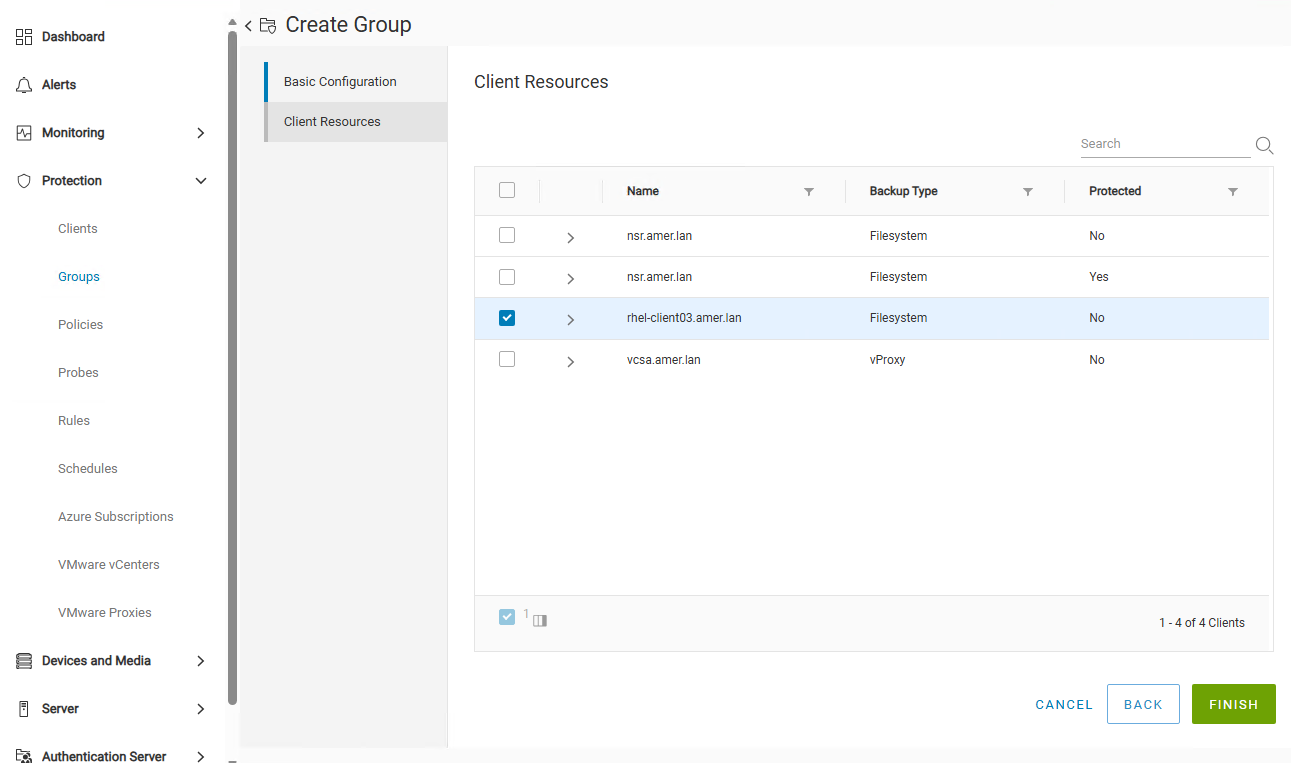
Figure 17: Client Resource selection during Group Creation.
- Once all of the required clients are selected, click Finish.
NOTE: Groups can be modified after creation from Protection -> Groups using the Edit option.
Adding an Azure Subscription
Specific information regarding NetWorker Azure protection can be found in the Dell NetWorker and Azure VM Snapshot Integration Guide available through Support for NetWorker | Manuals & Documents (You must sign-in with your Dell support account). See the version-specific guides which may contain settings and options that are specific to your NetWorker version.
The NetWorker server must be at-minimum NetWorker 19.11 in order to configure Azure subscriptions.
- Log in to NWUI and go to Protection -> Azure Subscriptions.
- Click +Add.
- Add the following details:
-
- Name: User defined value. This can be named as per your naming convention/preferences to identify the Azure subscription.
- Description: Optional. provide brief description about the Azure resource.
- Command:
nsrazure_discovery[-D debug level] - Endpoint:
management.azure.comis present by default.
-
Click Next. The following details must be provided by the Azure Administrator, or Azure Portal if you have direct access.
-
- Subscription ID: Obtained from Azure Home -> Subscriptions.
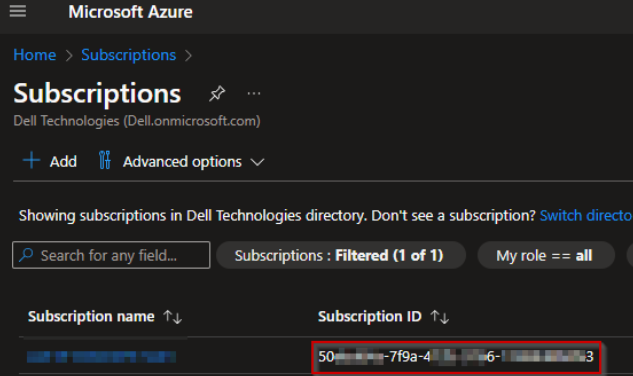
Figure 18. Azure Subscription Id
-
- Application (Client) ID: Obtained from Azure App Registrations:
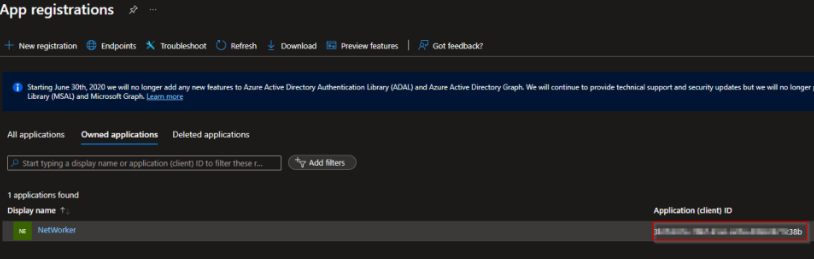
Figure 19. Azure Client ID
-
- Client Secret Key: From Azure go to Home -> App Registrations -> App Registration Name. Then click on Certificates & Secrets. Click on +New Client Secret, specify a name and validity period, once created collect the value:
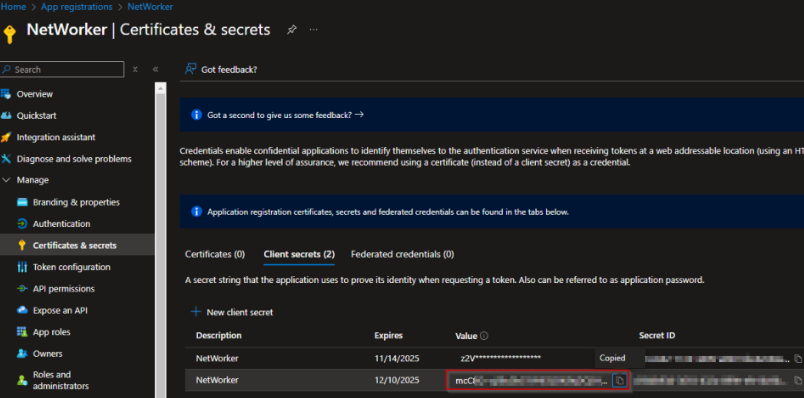
Figure 20. Client Secrets
-
- Tenant ID: From Azure go to Home -> App Registrations -> App Registration Name.
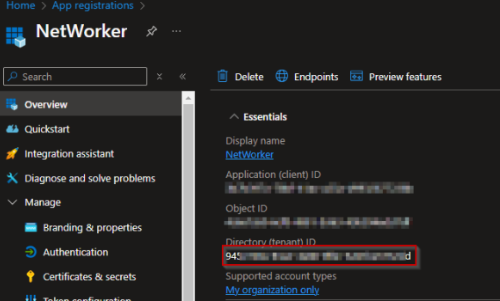
Figure 21. Tenant ID
- Click Finish.
Once the Azure subscription is created, a Discovery process can be run from the NWUI and Azure Resource Groups and VMs should be listed:
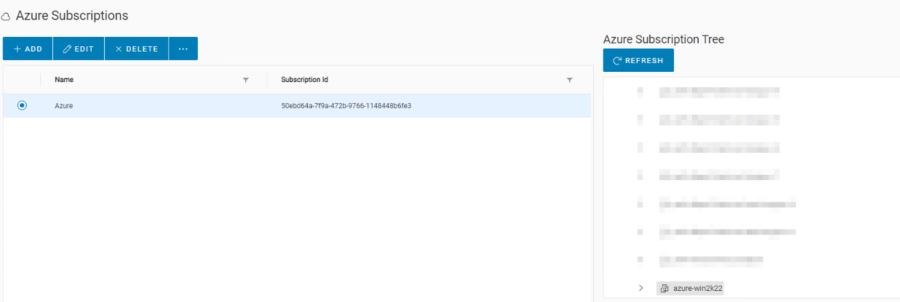
Figure 22. Azure subscription
Logs for the discovery process are on the NetWorker server under:
-
- Linux:
/nsr/logs/azure_subscription/SUBSCRIPTION-NAME_TIMESTAMP.log - Windows (Default):
C:\Program Files\EMC NetWorker\nsr\logs\azure_subscription\SUBSCRIPTION-NAME_TIMESTAMP.log
- Linux:
For additional information, see: NetWorker: Azure Snapshot Protection Troubleshooting Guide
Adding an Azure protection client
To back up Azure VMs, there must be at least one Azure VM in the Azure subscription that has the NetWorker 19.11 (or later) extended client software installed. The NetWorker Installation Guide provides instructions for installing NetWorker on specific Operating Systems. Support for NetWorker | Manuals & Documents (You must sign-in with your Dell support account)
An Azure backup backs up an entire VM, which includes all the attached disks. You cannot select individual disks of a VM for a backup. The NetWorker client acts as a proxy and is used to attach the Azure VM disks and backup the Azure VM data to Data Domain.
-
Log into the NetWorker Web User Interface (NWUI)
- Go to Protection -> Clients.
- Click +Add.
-
- Name: Enter the name of the Azure VM with the extended client software installed. This name should be DNS resolvable or requires
/etc/hostsentry on the Networker server. - Type: Cloud
- All other fields are optional on the Basic Configuration tab.
- Name: Enter the name of the Azure VM with the extended client software installed. This name should be DNS resolvable or requires
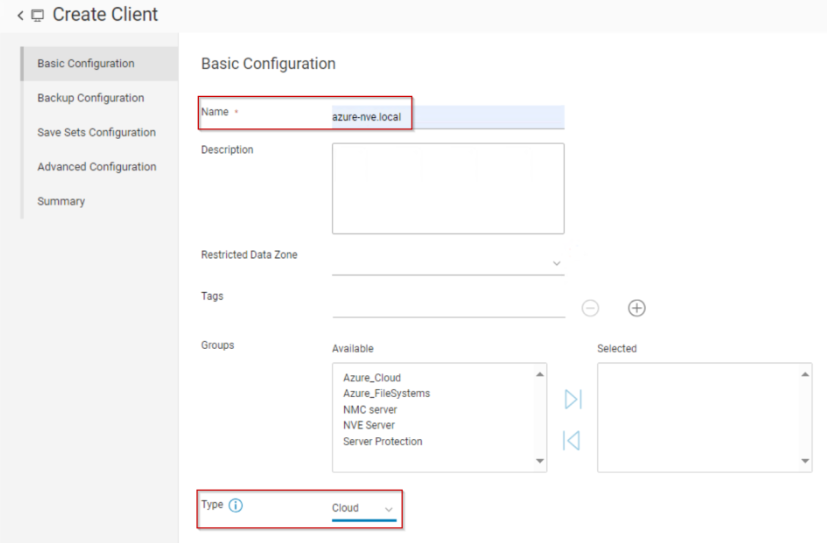
Figure 23. Creating an Azure client resource
- Click NEXT.
- If the NetWorker server successfully communicates with the Azure VM. The VMs details will be available and the Next option will not be grayed out:
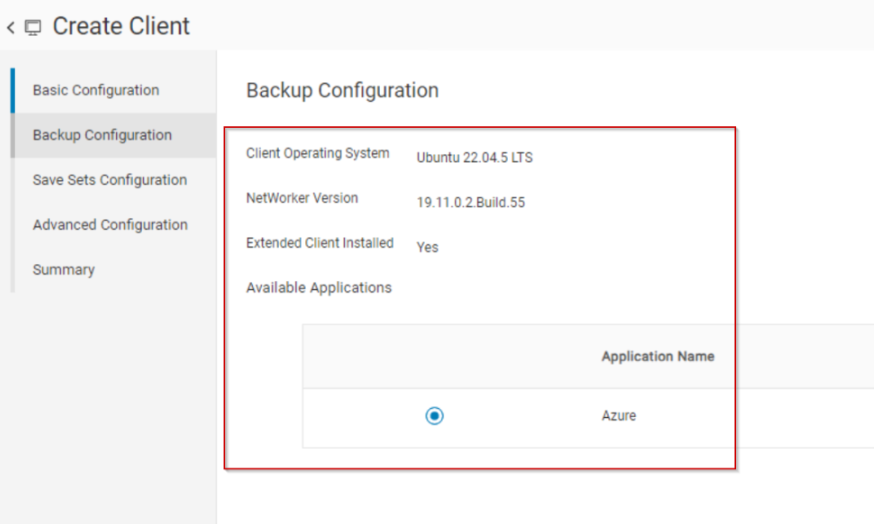
Figure 24. Create client with Azure type
- Click NEXT.
- On the Save Sets Configuration page:
-
- Select the Azure Subscription from the drop down.
- Click FETCH.
- Select an Azure Resource Group, or individual Azure VMs.
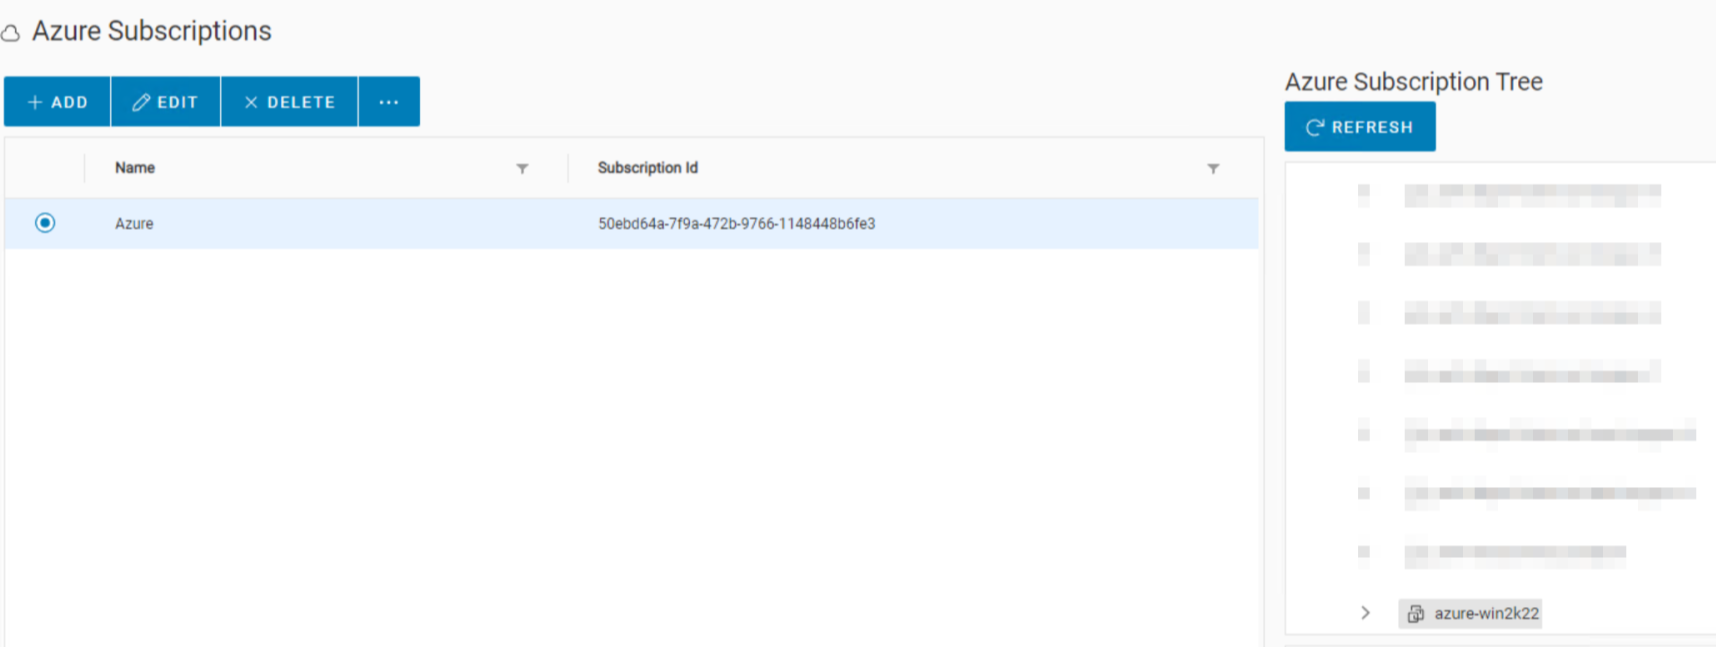
Figure 25. Azure subscription resources
- Click NEXT.
- On the Advanced Configuration window, click NEXT.
- Review the configuration Summary, and click FINISH.
If the Azure client created successfully, you will see it in the Clients tab of NWUI and NMC.
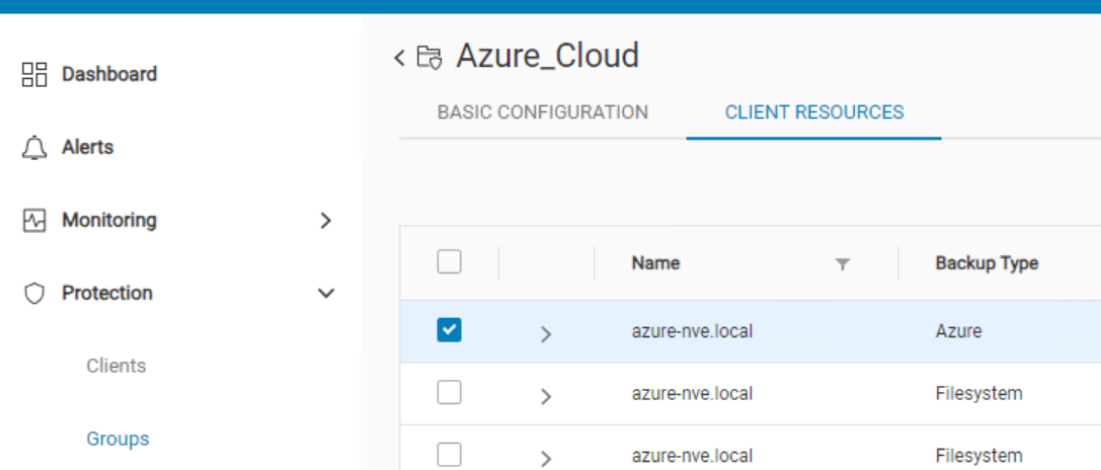
Figure 26. Azure client resource
The backup type is set as Azure
The client is created with the Azure type save set list:
Resource_Group1:VM1
Resource_Group1:VM2
The backup command is auto populated with nsrazure_save.
The application information is auto populated with the Azure subscription name of the NSR Azure Subscription resource.
- Expand the Devices and Media drop-down in the left menu.
- Go to Media Pools.
- Click +Add.
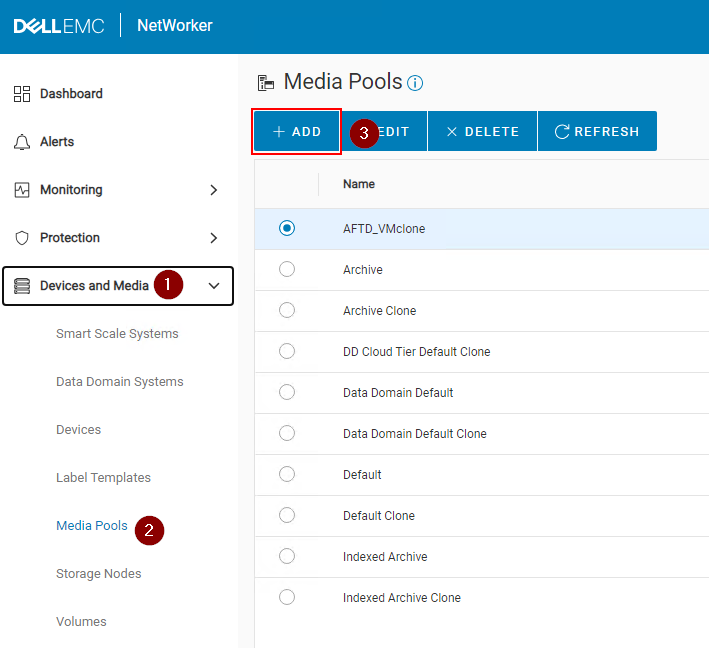
Figure 27. Creating a new pool from NWUI
- Populate the required fields:
- Specify a Name for the pool.
- Specify a Type (Backup or Backup Clone).
- Select a Label Template or click Add Label Template. See below Adding a Label Template section.
- Select a Media Type Required for the device type that the Pool will use.
- Optional: Select configured devices to use this pool. This can be left blank if you intend on creating new devices for the pool to use.
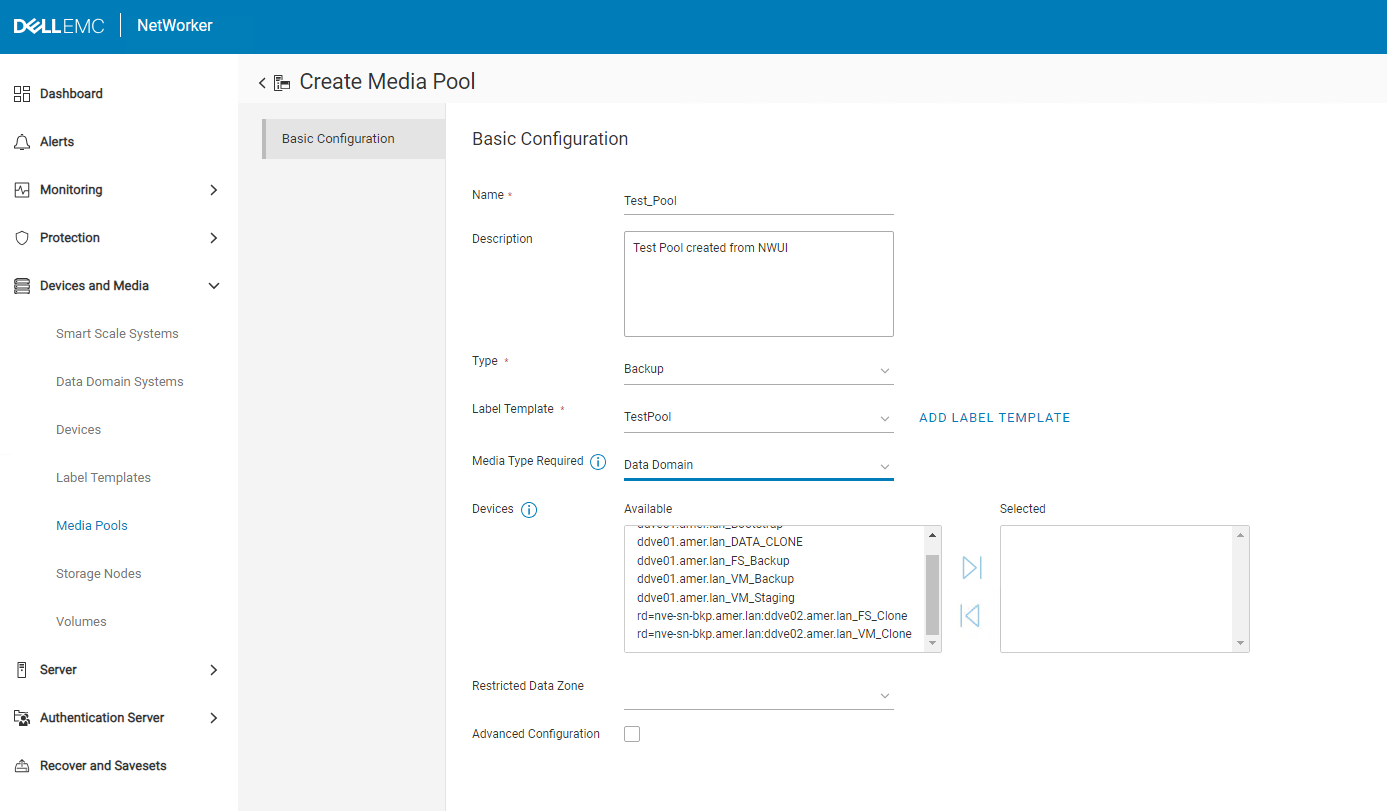
Figure 28. NWUI options for creating a Pool
-
- Click Finish.
- Adding a Label Template:
- Can be accessed from NWUI under Devices and Media->Label Templates.
- Can be accessed during Pool creation by selecting Add Label Template.
- Provide a Name for the label template. This is what appears when a device is labeled to a Pool using the label template.
- Specify a field component, such as Character String.
- Add a field component, such as Range of Numbers: 001 to 999 would be a common one used with NetWorker. The options shown match the default convention used by NetWorker (
NameOfPool.###) appears when a device is labeled against the pool. - Specify a Separator.
- Specify the Next Label for the Label Template to use. For the options used in this example this would be
TestPool.001.
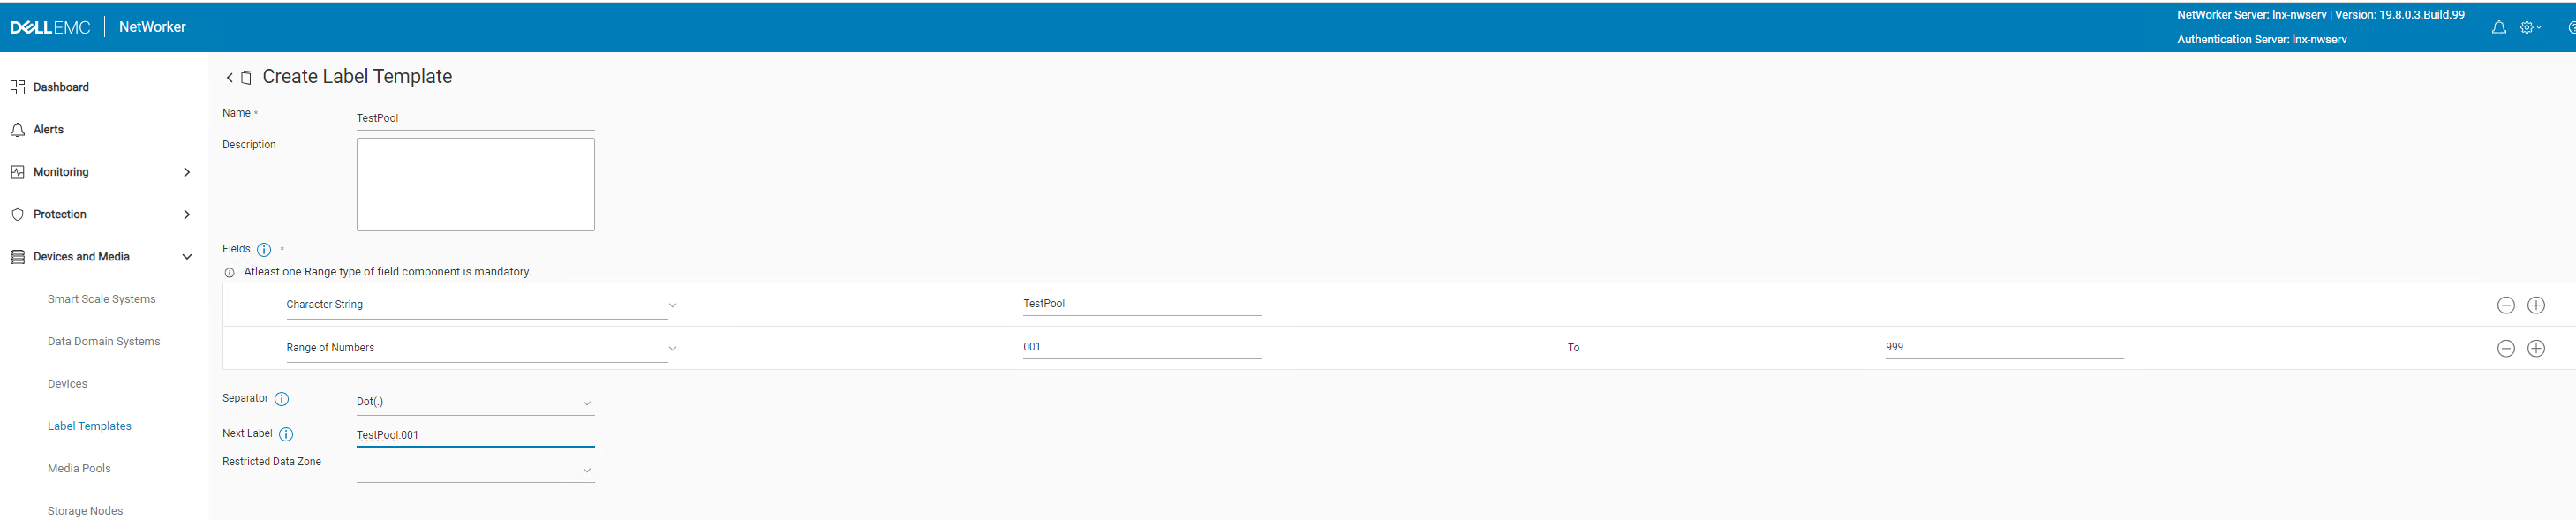
Figure 29. Template label configuration options in NWUI
- Click Create.
- Expand the Devices and Media drop down in the left menu.
- Go to Devices.
- Click +Add.
- Select Data Domain.
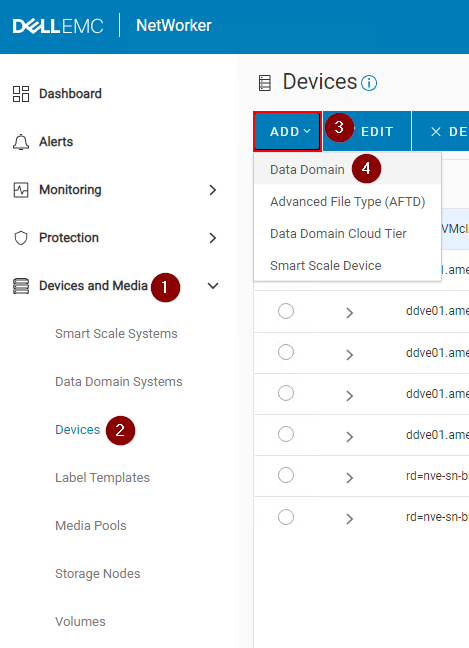
Figure 30. Steps for creating a new Data Domain device in NWUI
- Select a Data Domain which already exists on the NetWorker server. If no Data Domain exists, click Add Data Domain.
- Ensure that the correct ddboost user is shown when selecting a preexisting Data Domain.
- Click Connect.
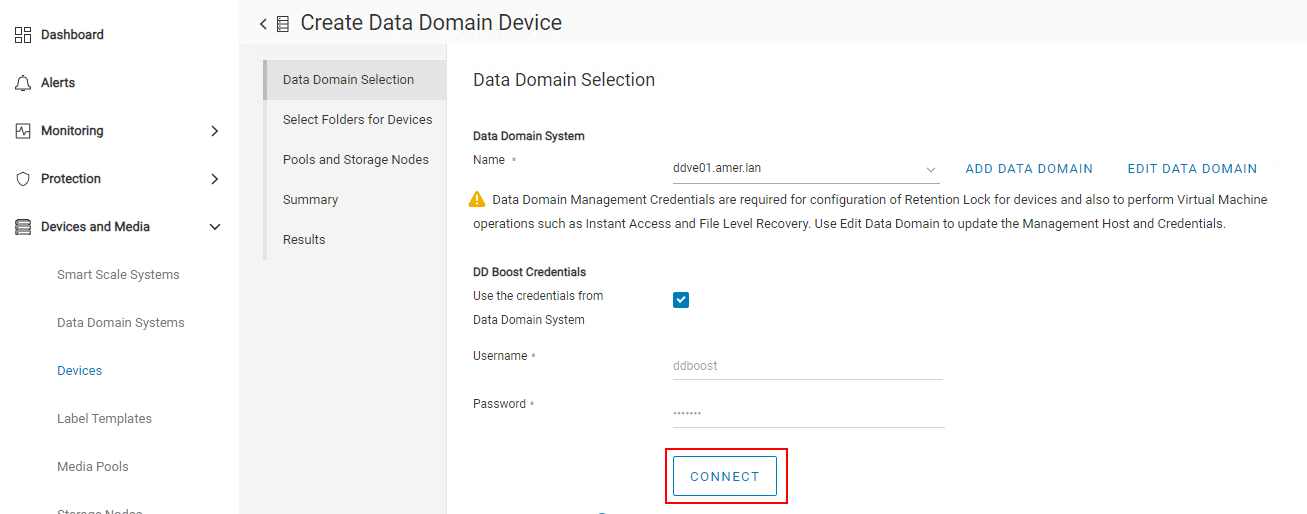
Figure 31. Data Domain device connection test
NOTE: If the connection attempt fails, use the Edit Data Domain option to update the ddboost user credentials. You can validate and update ddboost user credentials from the Data Domain web management interface.
- Click Next.
- Click New Folder.
- Enter a name for the device.
- Check the device. The Device Name and Storage Path should appear in the lower pane.
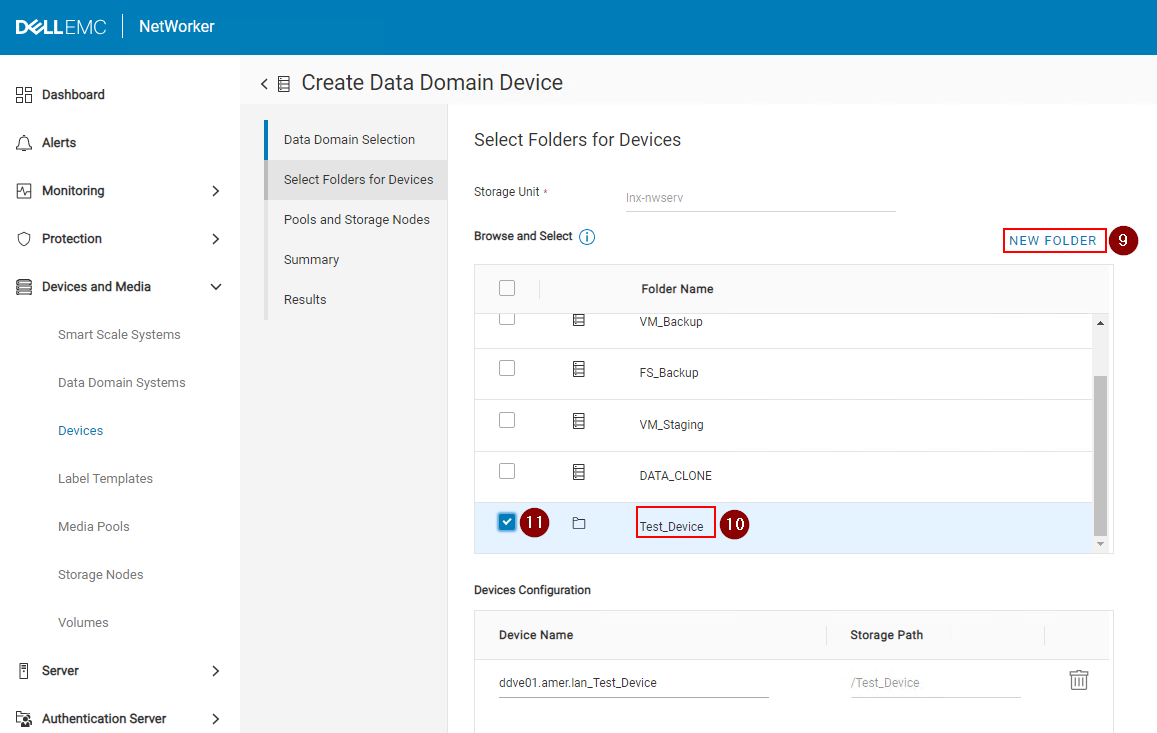
Figure 32. Device folder and storage path configuration
- Click Next.
- Select a Storage Node that the device is configured through.
- Select a Pool Type (Backup or Backup Clone). This should match the Pool type of the Pool selected in the next step. See the Adding a Pool section for more details.
- Select a Pool. See the Adding a Pool section for more details.
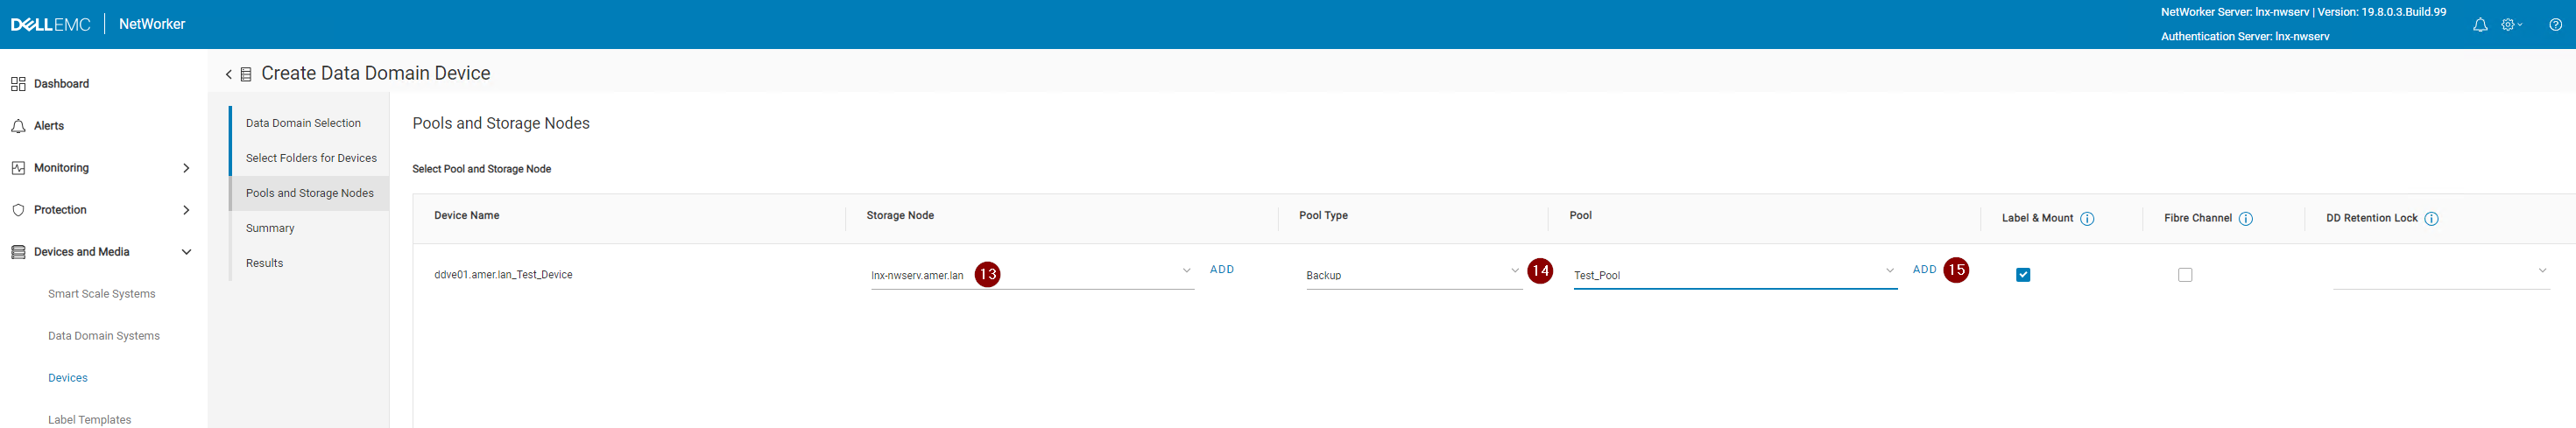
Figure 33. Device storage node and pool selection
- Click Next.
- Review the Summary details and click Create.
- Monitor the Results and click Finish.
- Click Refresh in the Devices pane to see the newly created device.
Creating a Protection Policy, Workflow, Action
The NetWorker protection stack uses the following hierarchy:
- Policy: Top-most container, typically used for managing data sets/types into logical groups for Administrative observability and reporting.
- Workflows: Configured underneath of a Policy. A Policy may contain multiple workflows. A NetWorker group is assigned to a workflow; a Workflow may only have one group assigned to it. The workflow acts as a scheduler for the start time and operations for the Actions to be performed on the Group. See: Adding a NetWorker Group
- Actions: Configured underneath of a Workflow. Typical actions are backup and clone (copy). A Workflow may contain one or more actions. For example, the workflow scheduler initiates a protection job of a group at a set time. The actions define the backup action (levels, overrides, so forth), following the backup an additional clone action may be configured to copy the data from one device to another.
The following Example demonstrates creating a simple backup policy, workflow, and and action for the client and group created earlier in this article. Specific data types may present other options during the action configuration steps. See the NetWorker documentation portfolio for specific instructions:
- Support for NetWorker | Manuals & Documents.
- Support for NetWorker Module for Databases and Applications | Manuals & Documents
- Support for NetWorker Module for MEDITECH | Manuals & Documents
- Support for NetWorker Module for Microsoft | Manuals & Documents
- Support for NetWorker for OpenVMS | Manuals & Documents
- Support for NetWorker Module for SAP | Manuals & Documents
Configuring a Policy.
- Log in to NWUI.
- Go to Protection -> Policies.
- Click +Add.
- In the Basic Configuration tab, specify the following:
- A Name for the Protecton Policy.
- (Optional) A Description describing the intended purpose of the policy.
- (Optional) from the Restricted Datazone drop down, select a RDZ (if configured). Restricted Datazones (RDZ) allows NetWorker administrators to organize a NetWorker environment into a multi-tenancy configuration, providing the ability to add an extra layer of privilege control. For more information, see the NetWorker Administration and NetWorker Security Configuration guides. Support for NetWorker | Manuals & Documents
- (Optional) Select the Protection period box to retain a valid copy of save sets for a specified period. If this option is not selected, the save sets will follow the retention policy settings defined in the action.
- Click Next.
- In the Notification tab you can optionally configure notifications for the Policy:
- From the Notify drop down select one of the following:
- Completion: notification event is triggered regardless if either a successful or failed policy event is observed.
- Failure: notification event is triggered only when a failed policy event is observed.
- (Optional) Modify the Command. By default the
nsrlog -f policy_notifications.logis configured. This means that the notifications are logged to/nsr/logs/policy_notifications.logon the NetWorker server. Alternatively, SMTP or SNMP notifications can be configured:
- From the Notify drop down select one of the following:
- Click Finish. After clicking Finish, you are moved to the Workflow creation window.
Configuring a Workflow.
To create a Workflow under an existing Policy, Log in to NWUI go to Protection -> Policies, click on a Policy then click +Add.
- In the Basic Configuration tab, specify the following:
- A Name for the Workflow.
- (Optional) A Description describing the intended purpose of the workflow.
- By default, the Autostart option is selected. This means that the workflow will start based on the Start time defined.
- Change the Start time to when you want the workflow to start.
- (Optional) Change the Interval. By default, this is set to 24 hours; meaning the workflow will trigger at the same time daily. This can be modified to any interval depending on the job type or intended protection cycle.
- (Optional) Change the Restart Window. By default, this is set to 24 hours; meaning, if a workflow is cancelled or fails, this is the duration in which it is possible to use the Restart function. During a Restart, resources which completed successfully before the cancellation/failure are not restarted. Once this time is elapsed, it is not possible to Restart and the workflow must be started as a new event.
NOTE: Some data types and actions may not support the Restart function, see the NetWorker Guides for clarifcations. Support for NetWorker | Manuals & Documents - Click Next.
- In the Notification field, define if you would like to set Workflow specific notification parameters. The default setting is Set at Policy level. Meaning the Notification event is triggered from the Policy status.
- Click Next.
- In the Associated Group tab, select a Group you previously configured; alternatively, you can create a new group during Workflow creation. See: Adding a NetWorker Group
- Click Finish. After clicking Finish, you are moved to the Action creation window.
Configuring an Action.
To create an Action under an existing Policy, Log in to NWUI go to Protection -> Policies, click on a Policy, then click the Workflow; under the Workflow, clikc +Add.
- Select the +Action option. This guide will demonstrate how to create a traditional backup action.
- Select backup.
- Then select traditional.
- In the Basic Configuration tab, specify the following:
- (Optional) A Name for the action. The default name is backup.
- (Optional) A Description describing the intended purpose of the Action.
- (Optional) Deselect the enabled checkbox if you do not want the action to be started during Workflow Start Time.
- (Optional) Select a Forced Backup level; otherwise, it will follow the schedule defined later.
- Click Next.
- In the Data Movement tab, specify the following:
- Select a Destination Storage Node. The destination storage node must match the device and pool you want to backup to. See: creating data domain device.
- Select a Destination Pool. See: adding a pool.
- Select a Retention Period. This defines how long the backup data should be kept.
- (Optional) Set the Client Override Behavior.
- Client Can Override—The values in the Client resource for Schedule, Pool, Retention policy, and the Storage Node attributes take precedence over the values that are defined in the equivalent Action resource attributes.
- Client Can Not Override—The values in the Action resource for the Schedule, Destination Pool, Destination Storage Node, and the Retention attributes take precedence over the values that are defined in the equivalent Client resource attributes.
- (Optional) Change the Success threshold.
- Warning—Save sets that complete with warnings are reported as success with warnings.
- Success—Save sets that complete with warnings are reported as failed. This is the default value. The number of times NetWorker retries a failed save set is determined by the value defined in the Retries attribute, which you specify in the Specify the Advanced Options screen of the Policy Action Wizard.
- (Optional) Select Apply Lock under DD Retention Lock. For more information, see the Data Domain Boost Integration Guide Support for NetWorker | Manuals & Documents.
- Click Next.
- In the Schedule tab, select one of the default schedules from the Select drop down; optionally you can add a new one or define the schedule directly in the action. Click Next.
NOTE: Some data types only support specific backup levels. See NetWorker documentation on specific components for more information. - (Optional) In the Notifications tab, define if you would like to set Action specific notification parameters. The default setting is Set at Policy level. Meaning the Notification event is triggered from the Policy status. Click Next.
- In the Advanced Configuration tab, leave the default parameters or change to your requirements. See the NetWorker Administration Guide for more information Support for NetWorker | Manuals & Documents. Click Next.
- Review the Summary then click Finish.
NVP-vProxy Recovery Operations
- Click Recover and Savesets in the left menu.
- Select or specify a Time Range.
- Select the VMware client type.
- Select the source vCenter.
- Select the Virtual Machine needed for restore. Click Refresh if the Virtual Machine pane does not populate.
- Click Refresh over the right pane to populate a list of backups and clones within the time range specified.
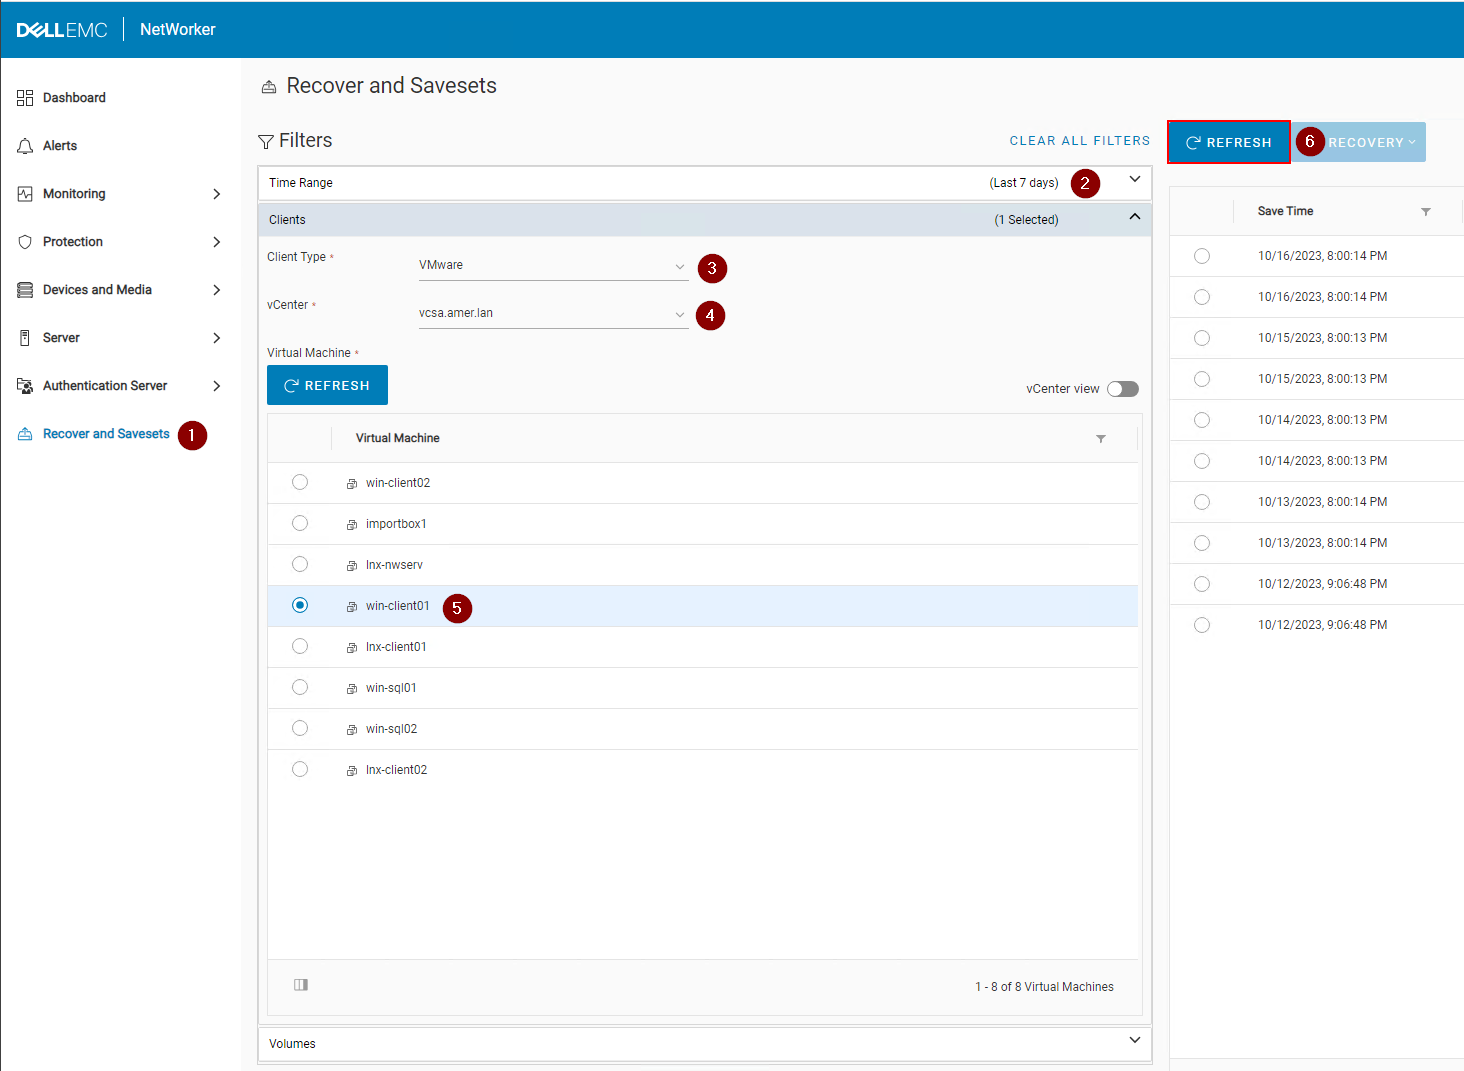
Figure 34. Initiating a VMware Virtual Machine restore from NWUI
- Click the Recovery drop down over the right pane and select the restore method needed:
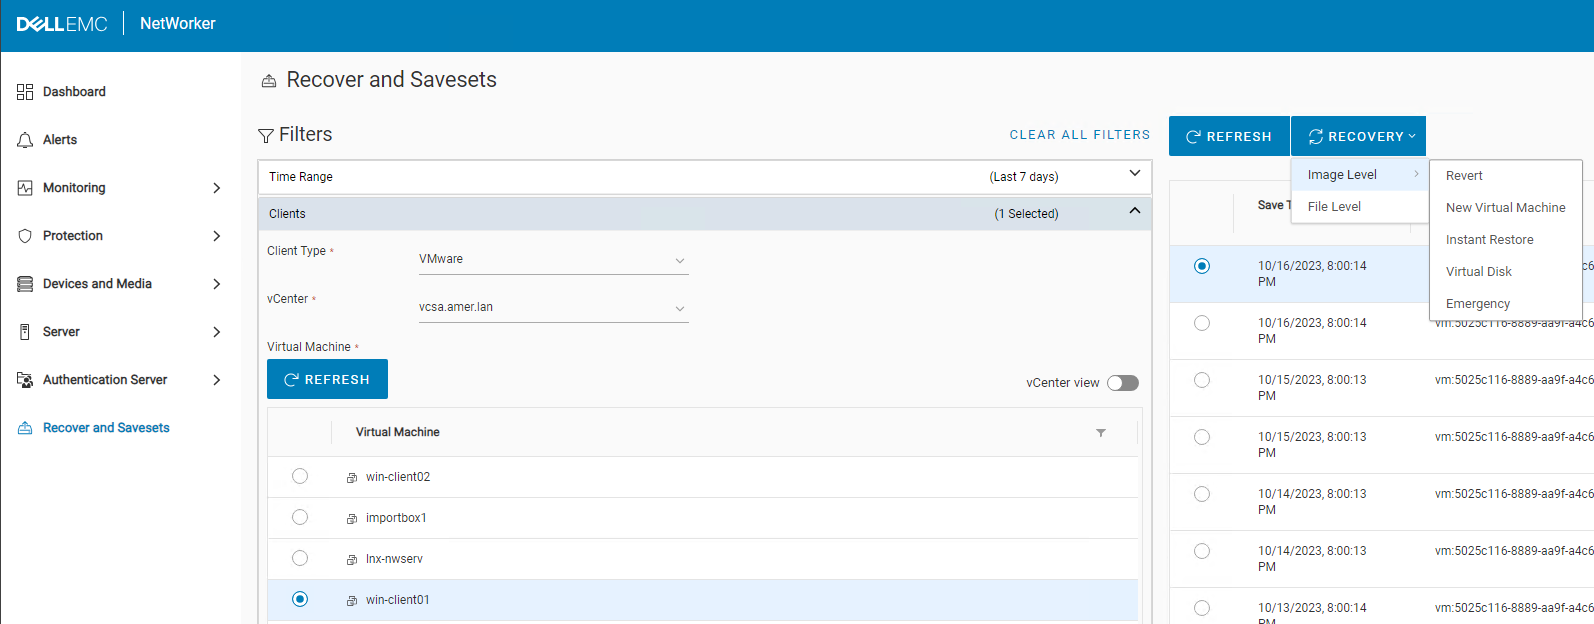
Figure 35. VM restore options available in NWUI
Table 1. Recovery Methods
|
Recovery Method |
Description |
|---|---|
|
Revert (or rollback) |
Roll back one or more VM disks to its state at the time of the backup |
|
Recover to a new Virtual Machine |
Recover a VM to a new VM |
|
Instant Restore |
VM backup is read directly from the Data Domain device |
|
Virtual Disk (VMDK) Recovery |
Recovers a virtual disk and adds it to an existing VM |
|
Emergency Recovery |
Add ESXi server details to recover a VM using that ESXi host (when no vCenter Server is available) |
|
File Level Recovery |
Recover individual files from a backup |
For more information about the different restore options, see the NetWorker VMware Integration Guide, available through: https://www.dell.com/support/home/product-support/product/networker/docs (You must sign-in with your Dell support account)
Additional Information
NetWorker: How to Install NWUI
NetWorker: How to Configure AD/LDAP from the NetWorker Web User Interface
NetWorker: How to configure "AD over SSL" (LDAPS) from The NetWorker Web User Interface (NWUI)
NetWorker: How to Perform a VMware FLR from the NetWorker Web User Interface
NetWorker: NWUI Triage and Troubleshooting Guide
NetWorker: How to Import or Replace Certificate Authority Signed Certificates for "AUTHC" and "NWUI" (Linux)
NetWorker: How to Import or Replace Certificate Authority Signed Certificates for "AUTHC" and "NWUI" (Windows)
Affected Products
NetWorkerProducts
NetWorker, NetWorker SeriesArticle Properties
Article Number: 000010494
Article Type: How To
Last Modified: 23 Oct 2026
Version: 14
Find answers to your questions from other Dell users
Support Services
Check if your device is covered by Support Services.