CAUTION:Many PDF editors and viewers add a line break to the end of each line of text in a PDF. As a result, when you copy commands that wrap across multiple lines in a PDF, the copied command is in the wrong format. It contains erroneous line breaks that might cause the script to fail.
To address this known limitation, do one of the following:
Paste the copied commands into a text editor and remove the line breaks.
Use the HTML version of this document when you are copying commands.
Revision history
The revision history of the document is listed in the following table.
Revision history. This table lists the dates on which this document was published and a description of the changes that are associated with each publishing date.
Date
Document revision
Description of changes
October 2026
12
Added the chapter "External SAN support for Azure Local".
Updated the "Deployment prerequisites for Azure Local deployment using local identity" topic to add DNS suffix as a required management service.
Updated the "Configure Broadcom NICs" topic to document support for Broadcom 57416 NICs.
June 2026
8
Minor updates across the document for 2606
April 2026
7
Added the chapter "Solution Deployment with Local Identity"
Removed "preview" from "Configurator app" in "Register machines with Azure Arc" topic
Removed "which is in preview" from the note in "Register machines with Azure Arc" topic
Added a new section "Drift detection for Azure Local" in "Register machines with Azure Arc" topic
Updated the “Adapter requirements” section in the “Operating system deployment” topic to reflect support for configuring Network ATC intents using the Azure portal or ARM templates, starting with Azure Local Solution version 2603.
April 2026
6
Removed bullet related to Windows Server in “Audience and scope” topic
Removed first sentence and updated SBE version number to 4.1.2505.1501 in “Download Connector” topic
Added note to “SBE package update prerequisites” topic
Added note to steps in Basics section in “Deploy Azure Local Instance using Azure portal” topic
Substantial revisions to "Configuration to prepare node" topic
Removed table and revised information and references in "Antivirus exclusions" topic
Updated procedure of "Restart a cluster node or take a cluster node offline" topic and added a link to current Microsoft procedures and renamed the topic to “Suspend and resume a cluster node"
Removed "Azure portal-based" from the doc title and revised the abstract to include Azure Arc template deployment method
Restructured document into chapters and moved content as to match other deployment guides
Removed any references to Azure Stack HCI 23H2 operating system as it is no longer possible to deploy the 23H2 version
Renamed "About using this guide" to "About copying commands from this guide"
Added "GPU Integration" chapter
Added a note and updated command in the first step in "Configure host networking" topic
Update command in "Change the hostname" topic
Updated text and image in "Install Windows Admin Center" topic
Minor image updates and added reference revised final step and to "Deploy an Azure Local instance using Azure portal" topic
Added a QoS table regarding network priorities to Step 12 of "Deploy Azure Local instance using Azure portal" topic
Updated QoS table regarding network priorities to Step 17 of "Deploy Azure Local instance using Azure ARM template" topic
Updated steps in "Prerequisites before deploying Azure Local Instance using Microsoft ARM template" topic
Added a note to the "Check Azure Arc registration after reboot" topic
Updates to steps in "Update SBE package using Azure portal" topic
Revised note in "Manually deploy operating system using Dell golden-image ISO" topic
Reformatted "View HCI compliance summary" into tables to try to improve the usability and readability of information
Minor updates across document
October 2025
5
Added a topic "Check Azure Arc registration after reboot"
In “Install Windows Admin Center” topic, removed high-availability content. Windows Admin Center no longer supports it from release 2410 onwards
In “Configure host networking” topic, added link and caution about optional automation deployment script
In "Configuration to prepare node" topic, removed duplicate command in code block
Renamed "Cluster deployment prerequisites" to "Azure Local Instance deployment prerequisites"
In "Register machine with Azure Arc" section, added link to the corrected Microsoft page regarding registering deployments with Azure Stack HCI OS version 23H2, update existing links
In "Stage SBE package for installation" deleted duplicate content
Added a note to "Deploy the Azure Local instance" topic regarding optional storage intent for single-node configurations
In "Deploy an Azure Local instance using Azure portal," edited several figures to blur identifiers
In the "Deploy an Azure Local instance using the Microsoft ARM template" procedure, corrected a capitalization error in the JSON snippet example
In "Prerequisites before deploying Azure Local instance using Microsoft ARM template" section, removed all topics because they are no longer needed from Azure Local release 2507 onwards
In the "Deploy an Azure Local instance using the Microsoft ARM template" procedure, corrected steps, and removed steps or details that do not apply to a single-node configuration, and added note to final step regarding deployment duration
In "Restart a cluster node or take a cluster node offline" procedure, corrected steps, and removed steps or details that do not apply to a single-node configuration
Split "Update SBE package using PowerShell" into two separate topics for online and offline solutions
Minor updates across document
August 2025
4
Changed references to the Azure Stack HCI operating system from 23H2 to 24H2 where required
Removed the "Update the page file settings" section
Removed the "Verify and update firmware and software compliance" section
Updated the "Review requirements" section
Updated the "Register servers with Azure Arc" section
Minor updates across the document
May 2025
3
Addition of 'Manual operating system deployment using Dell golden-image ISO' section
Removal of 'Factory-installed operating system deployment' section
May 2025
2
Rebranded product name and terms throughout the document
Updated procedures due to changes to the UI
September 2024
1
Removed the "Create a Storage Account" section.
May 2024
0
Initial publication
Deployment Introduction
Document overview
The Dell AX Solutions for Microsoft product family includes:
Dell AX System for Azure Local (based on Azure Stack HCI operating system)
Dell AX System for Windows Server (not described in this guide)
This deployment and operations guide provides an overview of Dell AX System for Azure Local with a single-node cluster configuration. The guide includes:
Guidance on how to integrate solution components
Instructions for preparing and deploying the solution infrastructure
NOTE:This guide only applies to infrastructure that is built using the validated and certified AX nodes from Dell Technologies and the Azure Stack HCI operating system.
Audience and scope
The audience for this document includes systems engineers, field consultants, partner engineering team members, and customers with knowledge about deploying hyperconverged infrastructures (HCIs) with the Azure Stack HCI operating system, Hyper-V, and Storage Spaces Direct. Customers who do not have Volume License agreements with Microsoft can order AX nodes from Dell Technologies with a factory-installed operating system and OEM license or as a bare-metal installation.
An Azure Local instance can be deployed in the following ways:
Dell Technologies Services-led—Certified deployment engineers ensure accuracy, speed, and reduced risk and downtime.
Customer led—Customers who have the qualified level of technical expertise follow the instructions in this guide.
Assumptions
This guide assumes that deployment personnel understand the following technologies and tasks:
AX nodes from Dell Technologies
Deploying and configuring BIOS and integrated Dell Remote Access Controller (iDRAC) settings
Dell AX System for Azure Local include various configurations of AX nodes from Dell Technologies. These nodes power the primary compute and storage cluster that is deployed as a hyperconverged infrastructure (HCI). The HCI uses a flexible solution architecture rather than a fixed component design.
Microsoft provides a feature to support a single-node cluster on an Azure Stack HCI operating system.
Single-node clusters are similar to standalone Storage Spaces nodes but are delivered as a Microsoft Azure service. Single‑node Azure Local instances support most Azure Local capabilities, except features requiring node‑level fault tolerance.
On a single-node cluster, there is no automatic provision of failover to another node. A hard drive is the fault domain in a single-node cluster, and only a single-tier configuration (All-Flash or All-NVMe) is supported.
NOTE:Node-level high availability cannot be supported on a single-node cluster. However, you can choose application-level or VM-level replication to maintain high availability in your infrastructure.
Single-node configuration
Like a multi-node cluster with Azure Stack HCI OS, a single-node cluster is delivered as a Microsoft Azure service and has all the hybrid-cloud features. Because the disk is the fault domain for a single-node cluster, it does not have to replicate any data over the network.
Dell Technologies recommends that you include an RDMA NIC in the setup. The RDMA NIC can help in future expansions or be used in VM traffic.
You can also use 25 GbE or 100 GbE adapters with Hyper-V Replica for application replication or Shared-Nothing Live Migration to move VMs to other clusters.
Solution Deployment
Solution deployment introduction
You can deploy Dell AX System for Azure Local by manually installing the operating system on AX nodes from Dell Technologies.
Each deployment has its own prerequisites, including configuring network switches, as described in this guide.
NOTE: Instructions in this deployment guide are applicable to the Azure Stack HCI operating system, version 24H2.
Each task in this deployment guide requires running one or more PowerShell commands. Dell Technologies recommends using these commands to complete the deployment tasks.
Deployment prerequisites
Dell Technologies assumes that the management services that are required for the operating system deployment and Azure Local instance configuration are in the existing infrastructure where the instance is being deployed.
The following table describes the management services:
Management services. Management services
Management service
Purpose
Required or optional
Active Directory
User authentication
Required only for AD-based deployments.
Domain Name System
Name resolution
Required
Azure
Deploy and manage
Required
DHCP
Hosts get IPs before and after host configuration using Network ATC
Optional
Registering a Partner Admin Link (PAL) for Azure related solutions
Partner Admin Link (PAL) is a simple telemetry-based capability that is built into Microsoft Azure. PAL enables Microsoft to track partner involvement in Azure related technical engagements.
Adding a Dell Partner ID to the Service Principal does not provide Dell with additional access to the customer system and does not change any Azure Role-Based Account Controls (RBACs).
NOTE:Adding a Dell Partner ID to the Service Principal associates Dell to the customer entity, which is persistent. This means that changes in customer system administrators do not break this association.
Dell Technologies employees can add a PAL using the user ID associated with either the subscription or Service Principal that is used for Arc or for Azure Local registrations. During a deployment, the customer creates the Service Principal for their system.
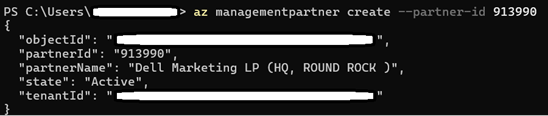
Example: az managementpartner create --partner-id 913990
az managementpartner create --partner-id <Partner ID>
The following figure shows an example of a completed registration in Azure CLI.
Successful addition of Partner ID to customer tenant
Alternatively, you can verify the registration, either using the following CLI command or in the Azure portal. This command displays a similar output to the az managementpartner create command used in the previous step.
az managementpartner show
NOTE:If there is an error when you add the Dell Partner ID, use the following command to correct the registration:
az managementpartner update --partner-id <Partner ID>
Results
The PAL is now registered.
Add a PAL through the Azure portal using the subscription user ID
You can register the Partner Admin Link (PAL) with the subscription user ID through the Azure portal.
NOTE:Portal-based registrations tie the PAL association with the customer user entering the information. If the customer user changes roles, the portal-based PAL association also ends.
The portal-based update is not audit-log tracked, while the CLI-based update is tracked.
If possible, Dell Technologies recommends that you use the user ID associated with the Service Principal for PAL registration.
To add a PAL to a customer user account using the subscription user ID, do the following:
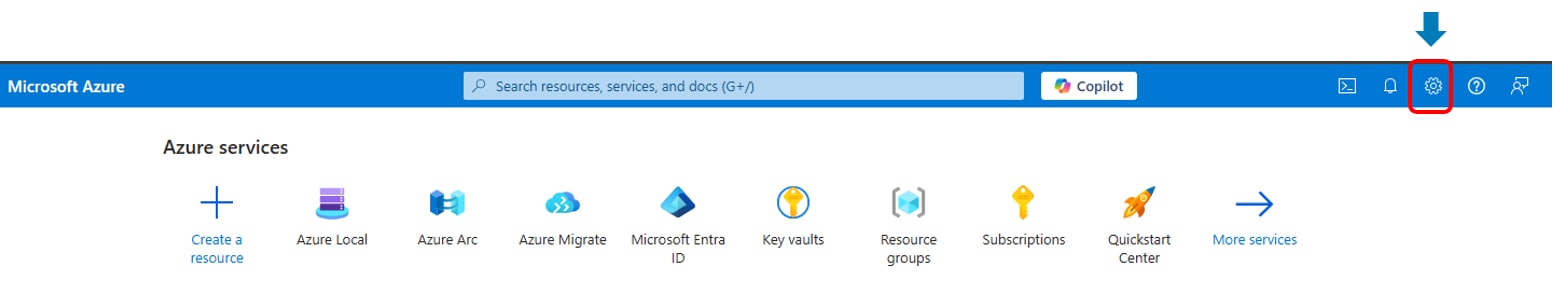
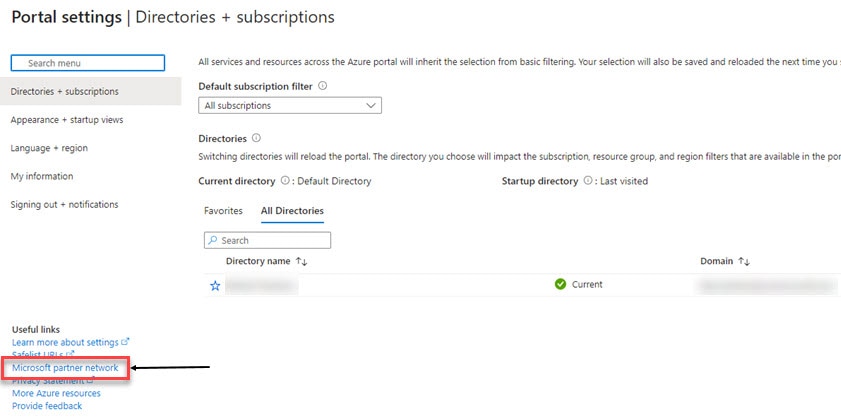
From Portal Settings, under Useful links, select Microsoft partner network.
Microsoft partner network link under Portal Settings
NOTE:If multiple directories are listed, confirm the Azure tenant, and then use the tenant that is associated with Arc registration.
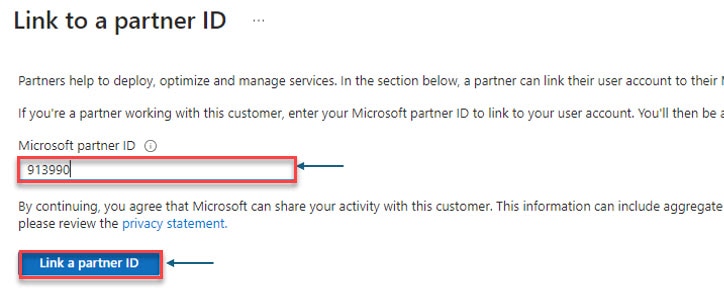
In the Link to a partner ID view, for the Microsoft partner ID, enter the Microsoft Partner Network (MPN) identifier that is associated with the country of the engagement. The available country MPNs are listed in the table in Dell Technologies Partner IDs for Partner Admin Link.
Microsoft partner ID field
To activate it, click Link to a partner ID.
The PAL is now registered.
Dell Technologies Partner IDs for Partner Admin Link
The following table provides a list of Microsoft Partner Network (MPN) partner IDs for Dell Technologies that can be used for Partner Admin Link (PAL) registration with Microsoft.
NOTE:For a country whose MPN partner ID is not listed in the following table, contact the applicable Strategic Partnerships email for help:
Dell Technologies MPN partner IDs for PAL use. Dell Technologies list of MPN Partner IDs for PAL use
Country
MPN ID
Argentina
1973856
Australia
1576776
Austria
1444496
Belgium
1447258
Brazil
1563635
Canada
742767
Chile
2389235
China
2580218
Colombia
1736279
Czech Republic
1980606
Denmark
1449600
Finland
1993462
France
892181
Germany
1449416
Greece
3679221
Hong Kong Sar
2790298
India
2419713
Indonesia
2834572
Ireland
1447272
Italy
1446223
Japan
578508
Korea
2153293
Malaysia
2731874
Mexico
724848
Netherlands
1446198
New Zealand
1872429
Norway
1446238
Panama
1477223
Poland
3697305
Portugal
1552205
Romania
1735552
Russia
4543982
Singapore
2773797
Slovakia
3812320
South Africa
1970176
Spain
1004323
Sweden
1449417
Switzerland
1449592
Taiwan
5097219
Thailand
2345177
Turkey
3396579
United Arab Emirates
3159758
United Kingdom
1447267
United States
913990
Install Windows Admin Center
Microsoft Windows Admin Center is a browser-based management tool that enables you to monitor and manage Windows Servers, failover clusters, and hyperconverged clusters.
You can download the latest version of Windows Admin Center from Microsoft Windows Admin Center and install it on a supported operating system.
You can install Windows Admin Center directly on a managed node to manage itself. You can also install Windows Admin Center on a separate management station to manage the AX nodes remotely.
The Windows Admin Center installer wizard performs the configuration tasks that are required for Windows Admin Center functionality. These tasks include creating a self-signed certificate and configuring trusted hosts for remote node access. Optionally, you can supply the certificate thumbprint that is already present in the target node local certificate store. By default, Windows Admin Center listens on port 443, but you can change the port during the installation process.
NOTE: The automatically generated self-signed certificate expires in 60 days. If you intend to use Windows Admin Center in a production environment, ensure that you use a certificate-authority-provided SSL certificate.
For complete guidance on installing Windows Admin Center on supported operating systems, see the Microsoft article Install Windows Admin Center.
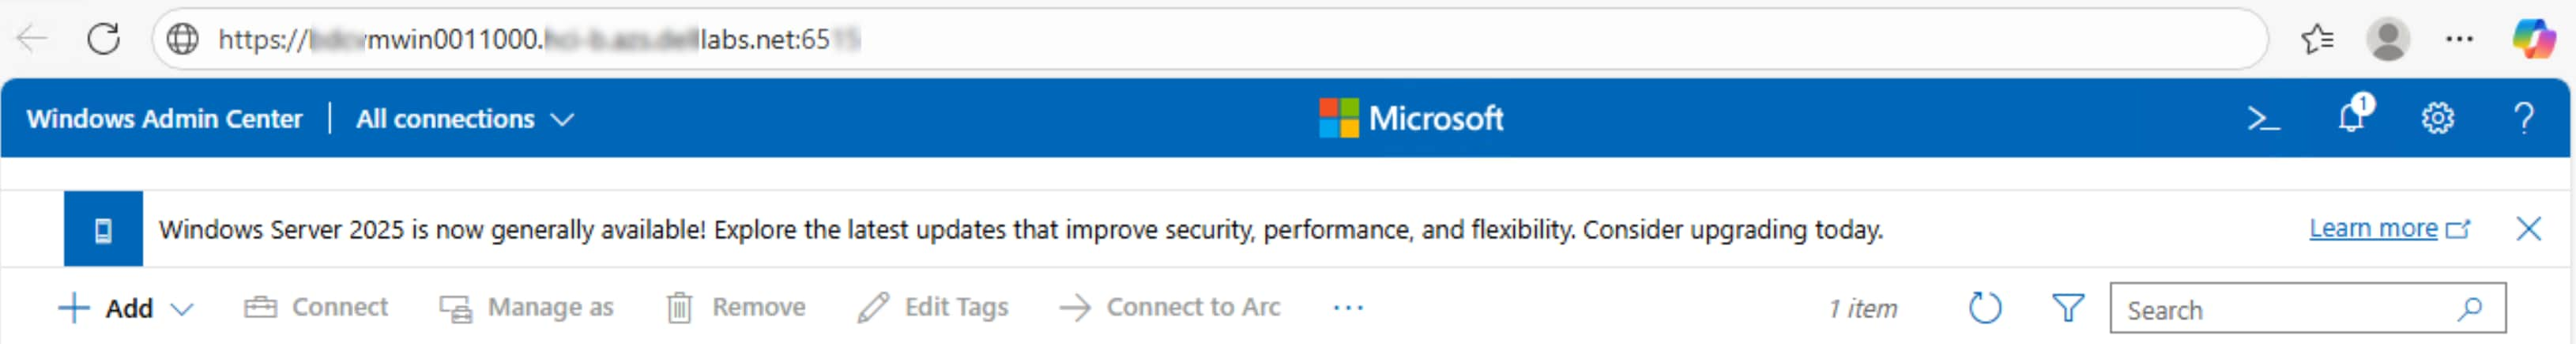
After the installation is complete, you can access Windows Admin Center at either https://ManagementStationName or https://ManagementStationName:<PortNumber>, as shown in the following figure.
Windows Admin Center All Connections window
Install Dell OpenManage Integration with Microsoft Windows Admin Center
You can install Dell OpenManage Integration with Microsoft Windows Admin Center.
Before you begin
Microsoft Windows Admin Center must already be installed.
To install Dell OpenManage Integration with Windows Admin Center, do the following steps:
Procedure
In Windows Admin Center, go to Settings > Extensions.
Under the Available extensions tab, select and install Dell OpenManage Integration.
Results
When Dell OpenManage Integration with Windows Admin Center is installed, you can access it on the left panel on the cluster manager, under Extensions.
Predeployment configuration
Before deploying AX nodes, complete the required predeployment configuration tasks.
Complete the following predeployment configuration before deploying the Dell AX System for Azure Local solution.
Configuring iDRAC and BIOS
AX nodes from Dell Technologies are factory-configured with optimized system BIOS and iDRAC settings.
NOTE:Dell Technologies recommends that you verify that the settings you want to use for iDRAC and BIOS align with the configuration recommendations. You can do this verification either before deployment through the iDRAC and BIOS settings or after deployment through the Compliance window in the Dell OpenManage Integration extension.
CAUTION:Do not enable the Automatic Update feature in iDRAC or manually perform out-of-band component firmware updates through iDRAC. All firmware, BIOS, and drivers must align with the Support Matrix and be applied strictly through supported update workflows.
The iDRAC in AX nodes can be configured to obtain an IP address from a DHCP server or can be assigned a static IP address. When the Out-of-band (OOB) network is not configured to obtain IP addresses from a DHCP server, you must manually set a static IPv4 address on each iDRAC network interface. You can use KVM or other means to access the physical server console and set the addresses.
Verify iDRAC pass-through IP address subnet mask on AX-670 and AX-770 servers
Verify and configure the OS to iDRAC Pass-through USB NIC subnet mask on 17th-generation servers, including Dell AX-670 and Dell AX-770, to ensure proper in-band communication between the host operating system and Integrated Dell Remote Access Controller (iDRAC).
To verify the correct setting of the USB NIC, do the following:
Procedure
Log in to iDRAC
Go to iDRAC Settings > Connectivity > Network > OS to iDRAC Pass-through.
The OS to iDRAC Pass-through window is displayed.
If USB NIC Subnet Mask is not already set to 255.255.255.0, change the field to this value.
Click Apply.
To confirm that the IP is accessible and the link is established between iDRAC and the host operating system, click Test Network Configuration.
Configure BIOS settings including the IPv4 address for iDRAC
Perform these steps to configure the IPv4 address for iDRAC. You can also perform these steps to configure any additional BIOS settings.
Procedure
During the system boot, press F2.
At System Setup Main Menu, press iDRAC Settings.
Under iDRAC Settings, select Network.
Under IPV4 SETTINGS, at Enable IPv4, select Enabled.
Enter the static IPv4 address details.
Click Back, and then click Finish.
Configure Intel E810 or E823 NICs
The Intel E810 or E823 network adapter supports both iWARP and RoCE v2 RDMA protocols.
Before you begin
Ensure that the network card or port is enabled for RDMA traffic.
To configure the Intel E810 or E823 network adapter for each port, do the following:
Procedure
During system startup, to enter system setup, press F2 and then select Device Setting.
From the list of adapters, select Intel network adapter.
Click Device Level Configuration.
(Optional) Set Virtualization Mode to SR-IOV to enable the prerequisite capability that allows tenant virtual machines to use the Azure Accelerated Networking option.
Click Back.
In the Main Configuration window, for NIC + RDMA Mode select Enabled.
To save the settings, select Back > Finish > Yes.
To return to the Device Settings window, click Yes.
Select the next port of the Intel adapter and repeat the previous steps.
To return to the System Setup window, click Finish.
To reboot the system, click Finish.
Configure NVIDIA (Mellanox) ConnectX-6 NICs
To enable support for SR-IOV in the operating system and virtual machines, you must configure the NVIDIA (Mellanox) ConnectX-6 NICs for each port.
Before you begin
Ensure that the network card or port is enabled for RDMA traffic.
To configure the NVIDIA (Mellanox) ConnectX-6 NIC (network adapter), do the following:
Procedure
During system startup, to enter the system setup, press F2, and then select System Setup.
Select Device Settings.
From the list of adapters, select NVIDIA ConnectX-6 adapter.
NIC+RDMA is set to Enabled.
Click Device Level Configuration.
(Optional) Set Virtualization Mode to SR-IOV to enable the prerequisite capability that allows tenant virtual machines to use the Azure Accelerated Networking option.
To return to the main configuration window, click Back. To save your changes, on the main configuration page, click Finish.
Repeat the steps for all NVIDIA adapters.
Configure Broadcom NICs
The Broadcom 57504 and 57416 NICs support only RoCE v2 RDMA protocol and can be configured on both converged and hyperconverged deployments. Both OCP and PCIe cards are available.
Before you begin
Ensure that the network card or port is enabled for RDMA traffic.
To configure the Broadcom NIC for each port, do the following:
Procedure
During system startup, to enter System Setup, press F2, and then select Device Settings.
From the list of adapters, select Broadcom network adapter.
Select Device Level Configuration, and from the menu choose the DCBX Mode option, and then choose Enabled (IEEE Only).
(Optional) Set Virtualization Mode to SR-IOV to enable the prerequisite capability that allows tenant virtual machines to use the Azure Accelerated Networking option.
Click Back.
In the Main Configuration window, set NIC + RDMA Mode to Enabled. To save the settings, click Finish.
To return to the Device Settings window, click Yes.
Select the next port of the Broadcom adapter and repeat the previous steps.
To return to the System Setup window, click Finish.
To reboot the system, click Finish.
Operating system deployment
The following instructions are for manual deployment of the Microsoft Azure Stack HCI OS version 24H2 on AX nodes from Dell Technologies. Unless otherwise specified, perform the steps on the physical machine in the infrastructure that is part of Azure Local.
NOTE:
The command output that is shown in the following sections might show only Mellanox ConnectX-4 LX adapters as physical adapters. The output is shown only as an example.
Before creating a cluster through the Azure Portal, for Azure Stack HCI OS version 24H2 and later, you must use Dell Golden image ISO for all deployments.
Adapter requirements
Azure Local requires using the same adapter card vendor and model for the machines in an instance that support instance operations. The ports that are used by the same Network ATC intent must use the same vendor, model, and speed.
Starting with Azure Local Solution version 2603, Azure Local instances that require NIC-level high availability can use the Azure portal or ARM templates to configure Network ATC intents using NIC ports from adapters that share the same PCIe Vendor ID and PCIe Device ID. This capability enables ports from both an OCP NIC and a PCIe riser NIC to be included within a single Network ATC intent, provided the adapters are of the same NIC model.
CAUTION:If you use optics or cables from one vendor with an adapter card from another vendor, Dell cannot guarantee that your configuration will work as expected. Before you mix vendor equipment in an Azure Local instance, consult the Dell Technologies cable and optics in the Support Matrix.
Manually deploy operating system using Dell golden-image ISO
You must use a Dell provided Azure Local golden-image ISO to install the baseline operating system image for Azure Local instances.
The golden image includes the Azure Stack HCI operating system, Microsoft operating system image customization, Azure Arc extensions, LCM service, registration modules, and Dell customization. Customization includes device drivers that align with the Dell support matrix for Azure Local.
For an Azure Local solution version 2503 and later, you must use a Dell provided Azure Local golden-image ISO. To download the latest Dell provided golden-image ISO, go to Azure Local Support Matrix, and then click Azure Local Support Matrix (Version X) > Azure Local Golden Images (Version X).
NOTE:To access any of the Dell provided Azure Local golden-image ISOs, you must have a Dell Support account.
Before you begin
Before you deploy the Azure Local instance using the Azure Portal or an ARM template, for a single-node cluster configuration, install the golden-image ISO on the machine that is used for Azure Local instance creation. You can use the iDRAC virtual media feature to mount the golden-image ISO.
Procedure
Open the iDRAC interface for the node and re-create the virtual disk on the BOSS-N1 controller where the host operating system is located. If the BOSS virtual disk is in a good state, you can choose to clean the drive, install the operating system on it, and then go to step 2.
Optionally, if the existing BOSS virtual disk is degraded, you can do the following:
Open iDRAC virtual console and mount the golden-image ISO.
Boot the system from the golden-image ISO. Because no other operating system is installed on the host, it should automatically boot from the ISO without requiring you to select a boot device.
NOTE:You must delete any previously created partitions on the boot drive during the deployment procedure.
CAUTION:Do not enable the Automatic Update feature in iDRAC or manually perform out-of-band component firmware updates through iDRAC. All firmware, BIOS, and drivers must align with the Support Matrix and be applied strictly through supported update workflows.
Configure host networking
Identify the network interface cards to be used for the management or compute traffic and assign the IP address to the first port.
Before you begin
NOTE:If you have a DHCP server in your environment, skip the procedure.
Ensure that the host is assigned to an IP address in the correct VLAN.
NOTE:The host IP, DNS, and gateway addresses that are used throughout the guide are examples. You must use the relevant IPs that are based on your environment.
NOTE:You can use the optional 1_AzLocal.ps1 script from Dell ProSupport GSE on GitHub to automate the operating-system configurations for host networking, rename the system name, and register with Azure. You must still do firmware updates before the deployment. Dell Technologies Solutions Engineering has not validated this code. Use at your own risk.
To log in to the host console of each system using the iDRAC virtual console and assign host IPs and respective VLANs, do the following:
Procedure
To disable the DHCP on all management adapters (NICs) except the NDIS NIC, run the following command:
To assign the management IP address to the first port, run the following command:
New-NetIPAddress -InterfaceAlias "Integrated NIC 1 Port 1-1" -IPAddress 192.168.10.11 -DefaultGateway 192.168.10.1 -PrefixLength 24 -AddressFamily IPv4 –Verbose
To set DNS IP addresses, run the following command:
Set-DnsClientServerAddress -InterfaceAlias "Integrated NIC 1 Port 1-1" -ServerAddresses 192.168.11.50, 192.168.11.51
To assign VLAN ID for the management adapters, run the following command:
NOTE:If the management network has any untagged VLANs that are configured in the switch, then this step is not required.
Get-NetAdapter -Name "Integrated NIC 1 Port 1-1" | Set-NetAdapter -VlanID 202 -Confirm: $false
Get-NetAdapter -Name "Integrated NIC 1 Port 2-1" | Set-NetAdapter -VlanID 202 -Confirm: $false
Change the hostname
By default, the operating system deployment assigns a random name as the host system name. For easier identification and uniform configuration, Dell Technologies recommends that you change the hostname to something that is relevant and easily identifiable.
CAUTION:The computer and cluster names cannot be more than 15 characters. If the name exceeds the character limit, the deployment will fail when the system tries to encrypt the volume.
To change the hostname, run the following Rename-Computer command:
Rename-Computer -NewName <NewHostName> -Restart
NOTE: The command induces an automatic restart at the end of the renaming operation.
To allow the issuing of remote commands to nodes that are not in the domain, run the following command on each node:
#Enable Remote Desktop
Set-ItemProperty -Path "HKLM:\System\CurrentControlSet\Control\Terminal Server" -Name "fDenyTSConnections" -Value 0
Enable-NetFirewallRule -DisplayGroup "Remote Desktop"

#Configure time source using NTP server FQDN address
w32tm /config /manualpeerlist:"<NTP Server 1 FQDN> <NTP Server 2 FQDN>" /syncfromflags:manual /update

#Check time source
w32tm /query /status

#Optionally configure the machine to accept remote management and allow pings for troubleshooting purposes.

#Enable ICMP firewall rule
netsh advfirewall firewall add rule name="ICMP Allow incoming V4 echo request" protocol=icmpv4:8,any dir=in action=allow
Configuring firewall settings
For Azure Stack HCI operating system, configure firewall settings for outbound endpoints and internal rules and ports. For more information about configuring the firewall settings, see Firewall requirements for Azure Local | Microsoft Learn.
Deploying an Azure Local instance
Azure Local instance deployment prerequisites
Before deploying Azure Local instance, you must ensure that the deployment prerequisites are met.
NOTE:Ensure that you unmount any virtual media from the iDRAC.
Management services
Dell Technologies assumes that the management services that are required for the operating-system deployment and cluster configuration are in the existing infrastructure where the Azure Local instance is being deployed.
The following table describes the management services:
Management services. The table lists the required and optional management services and their purpose.
Management service
Purpose
Required or optional
Azure
Deploy and manage
Required
Active Directory
User authentication
Required only for AD-based deployments
Domain Name System
Name resolution
Required
DHCP
Hosts get IPs before and after host configuration
Optional
Review requirements
Ensure that the network configuration is in order.
Ensure good Internet connectivity on the nodes.
Ensure that your Azure subscription is registered with the required resource providers. Only the owner or contributor of the subscription can register the resources provider. For the most up-to-date list, see Assign required permissions for Azure Local deployment.
NOTE:Azure Arc gateway is only available in Azure Local version 2506 or later.
NOTE:Manual installation of PowerShell modules is no longer required. The registration procedure changed with the introduction of golden images (10.2503) or Microsoft-provided composed images.
You can use one of the following options to register the Azure Local machines with Azure Arc using PowerShell commands. For details, see:
If you prefer to use a guided UI-based workflow instead of the Arc script, you can select the Via Configurator App tab on the Microsoft pages that are listed above.
NOTE:Dell Technologies has validated the registration of machines using the Configurator app. However, Dell Technologies does not officially support this functionality. If users encounter any issues, they must contact Microsoft directly.
Drift detection for Azure Local
For identifying configuration related deviations or troubleshooting issues in your Azure Local environment, see Drift Detection for Azure Local. You can run drift detection either before or after the cluster is created.
Check Azure Arc registration after reboot
During Azure Arc registration, when the update phase completes, if the system reboots, check the Arc registration status on the system after the reboot completes.
When registering Azure Arc on machines that are imaged with a specific Golden image (operating system customization 12.2506.0.3136), a required update triggers a reboot.
To check the Azure Arc registration, do the following:
NOTE:If you are using the latest Dell Golden-image ISO, you can ignore the following message if the message appears during the ARC registration process: "You are not running the latest Azure Local version. Older versions can only be deployed using the ARM template. Deployment using the Azure Portal cloud wizard is not supported."
Procedure
To monitor the reboot registration status, run the following command:
(Get-ArcBootstrapStatus).Response.Status
If the system completes registration and returns a status of:
Succeeded, no further action is required.
Failed, rerun the Invoke-AzStackHciArcInitialization command.
(Optional) After a successful registration, run azcmagent.exe on the Azure Local machine.
# Expect a status of Connected and a recent Last Heartbeat

azcmagent.exe show 'Agent Status' 'Agent Version' 'Agent Last Heartbeat'
Sample output
Agent Version: 1.58.03228.2572
Agent Status: Connected
Agent Last Heartbeat: 2026-01-27T14:49:58Z
When you use the Dell provided golden image to image a node, the SBE files are automatically placed in the C:\SBE directory. The SBE package is installed as part of the cluster deployment.
Deploy the Azure Local Instance
You can deploy an Azure Local instance in the following ways:
NOTE:The creation of a storage intent is optional for single-machine deployments.
Deploy an Azure Local instance using Azure portal
The deployment wizard guides you through the creation of an Azure Local instance.
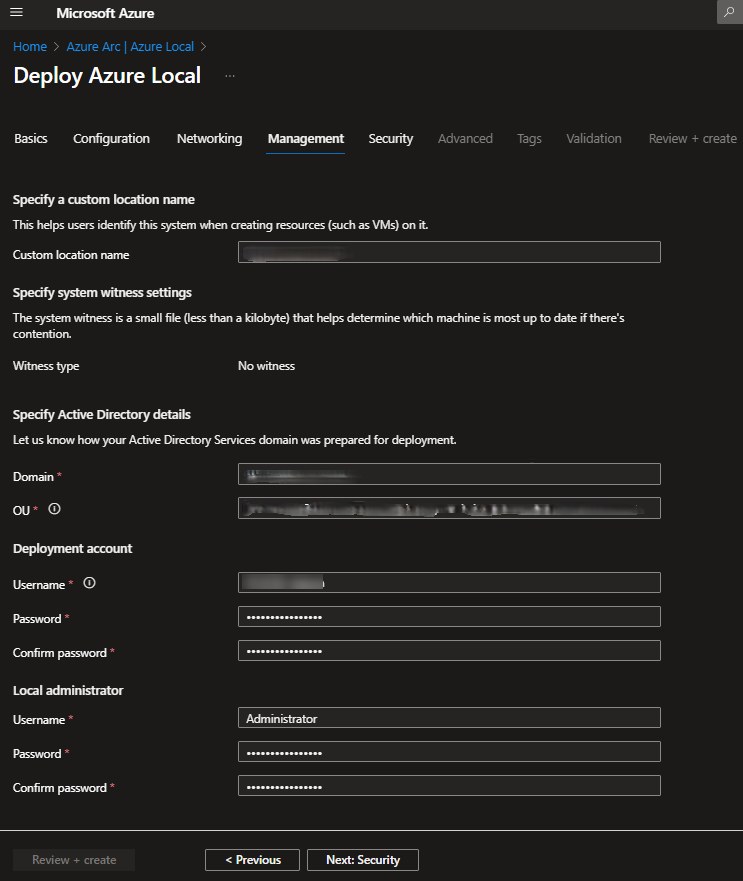
You can use the wizard to define all instance‑level and machine‑level configuration settings. The wizard guides you through the following windows:
Basics
Configuration
Networking
Management
Security
Advanced
Tags (optional)
Validation
Review and create
To create an Azure Local instance:
Procedure
To start the wizard from Home > Azure Local, select Deploy Azure Local.
Under Get Started, in Deploy Azure Local, select Create instance.
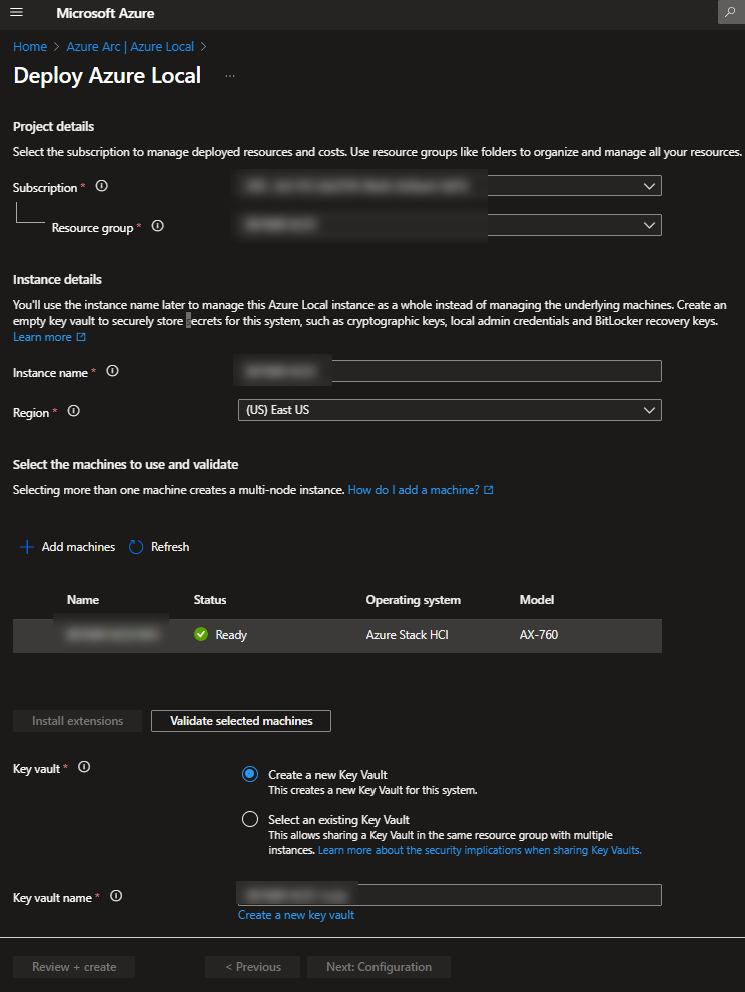
In the Basics window, as shown in the following figure, under Project details, select the Subscription and Resource group from the options lists.
Deployment wizard - Basics window
Under Instance details, enter the Instance Name and Region.
To create a new key vault, enter a Key vault name, and then click Create a new key vault.
NOTE:
If a previously created key vault for a decommissioned instance with the same name exists, you must first delete and purge the old key vault before creating one.
Azure Local does not support deploying a cluster by using an existing Azure key vault that has private endpoints enabled.
If one or more servers show a status of Missing ARC Extensions, select the affected servers, and then click Install Extensions. Wait for the extension installation to complete and for the node status to update to Ready.
To validate the servers for use, select one or more, and then click Validate selected servers.
After you validate the servers, a green checkbox displays next to Validate selected servers.
To go to the next window, click Next: Configuration.
In the Configuration window, enter details about the instance.
To go to the next window, click Next: Networking, shown in the following figure.
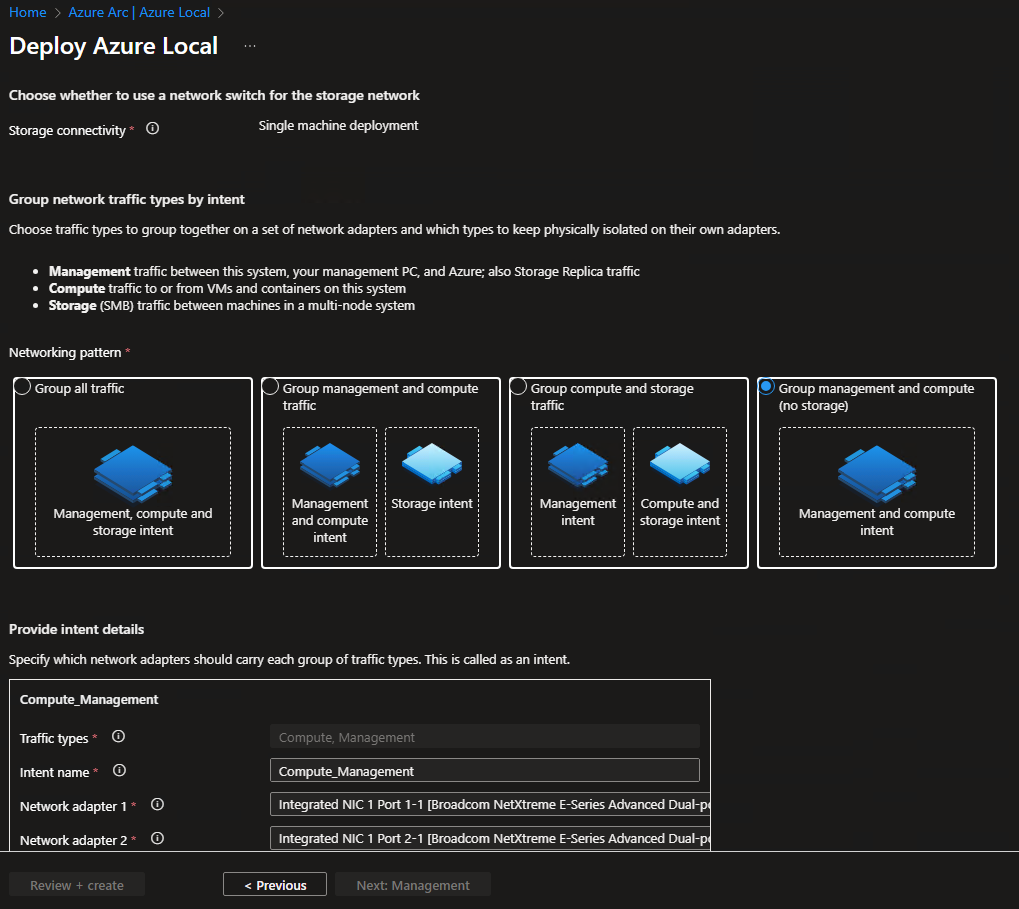
Deployment wizard - Networking window
In the Networking window, for Storage connectivity, choose whether you use a network switch for the storage network.
Under Group network traffic types by intent, based on your network topology, select the Networking pattern. For a single- machineinstance, Dell Technologies recommends that you select Group Management and Compute (no storage).
The following table shows the Quality of Service (QoS) flow priorities for each network type:
QoS priorities for network intents. The table shows the QoS flow priorities that are based on traffic class for each network type.
Traffic class
Purpose
QoS flow
ETS bandwidth allocation
3
RDMA (SMB Direct)
Enabled
50 percent
7
Cluster network
Disabled
10 GbE equals 2 percent
Greater than 25 GbE equals 1 percent
0-2, 4-6
0 - Best-effort traffic
Disabled
Remaining percentage distributed across the traffic classes
Under Provide intent details, for management-network-intent creation, select the network adapters.
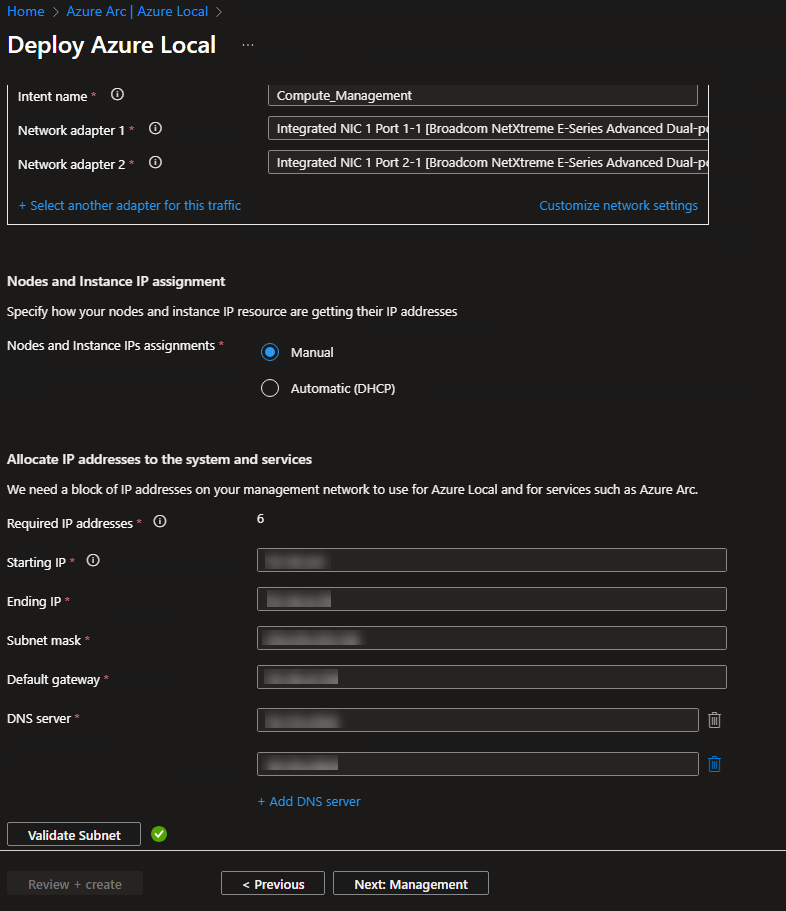
Under Allocate IP addresses to the system and services, provide the required details as shown in the following figure.
Allocate IP addresses section
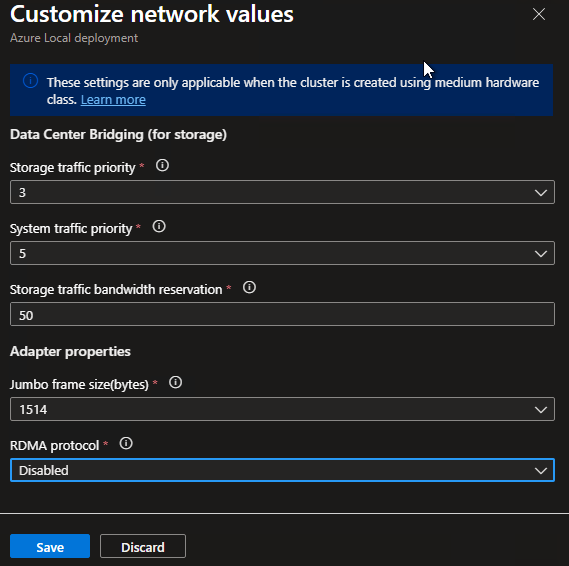
Under Compute_Management, to update information such as network intent, data center bridging, and adapter properties including Jumbo Frame size and RDMA protocol, click Customize network settings.
NOTE: For management network intents, RDMA must be disabled, as shown in the following figure.
Customize network values window with disabled RDMA protocol
NOTE:Microsoft recommends that you set System Traffic Priority to 7 for new cluster deployments. A priority value of 5 is also supported and acceptable. Ensure that the QoS settings on the top‑of‑rack (ToR) switches match the QoS settings that are configured in the host operating system.
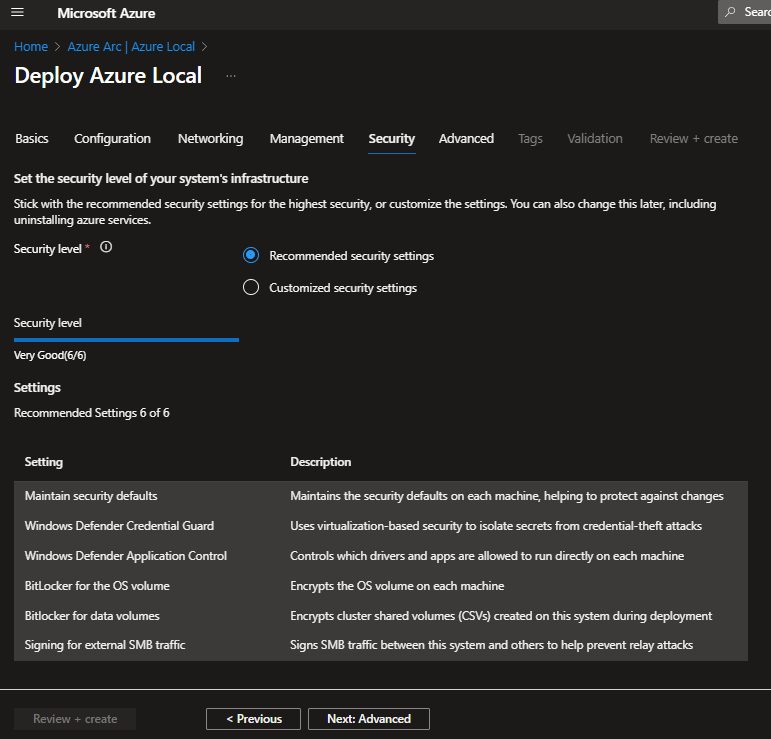
Under Security shown in the following figure, Dell Technologies and Microsoft recommends that you choose Recommended security settings, which offers the highest level of security settings.
Deployment wizard - Security window
Click Next: Advanced.
Under Advanced, choose Create workload volumes and required infrastructure volumes.
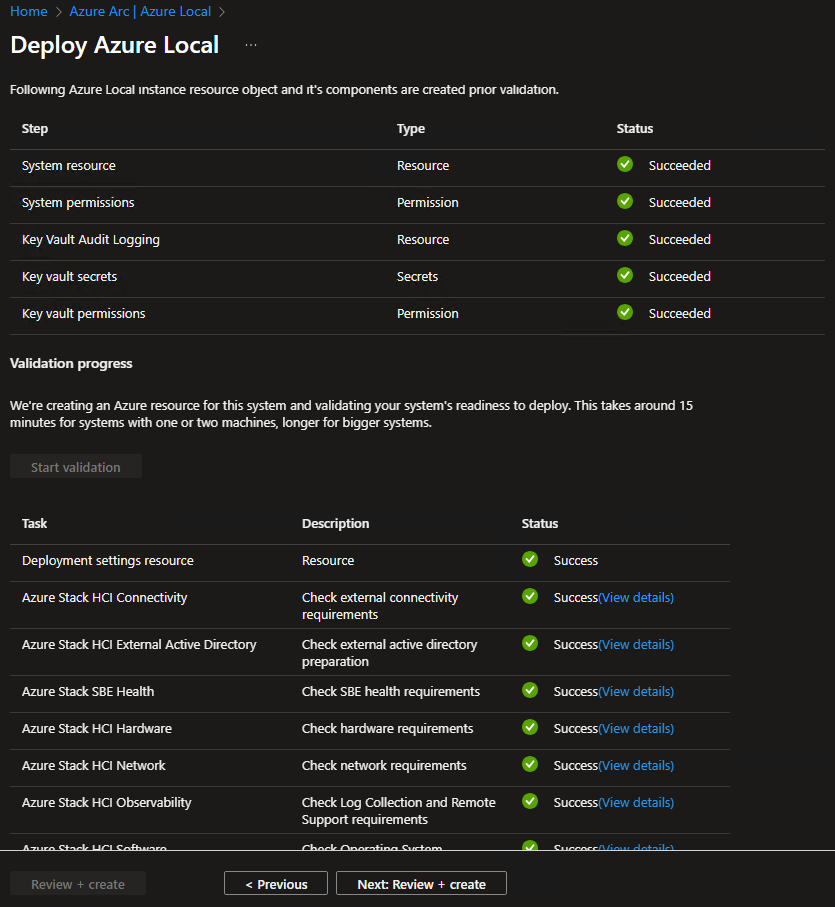
The system creates a resource object and its components for the instance. The validation process typically completes within 15 minutes for a single-server deployment, though it may take longer depending on system conditions or environmental factors. This process assesses the system readiness for cluster deployment.
Click Next: Review + create.
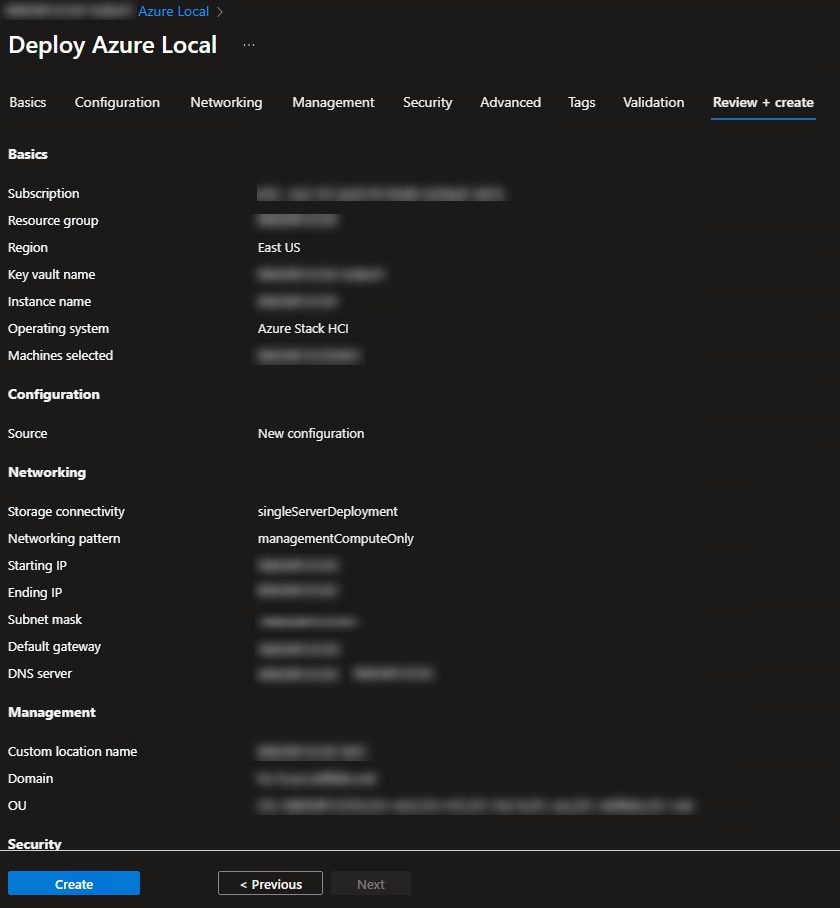
The Review + create window shows the configuration information that you entered or selected in the previous steps for creating the instance. To return to a previous step to change any settings, click Previous.
Deployment wizard - Review and create window
To start the instance creation process, review and confirm your settings, and then click Create .
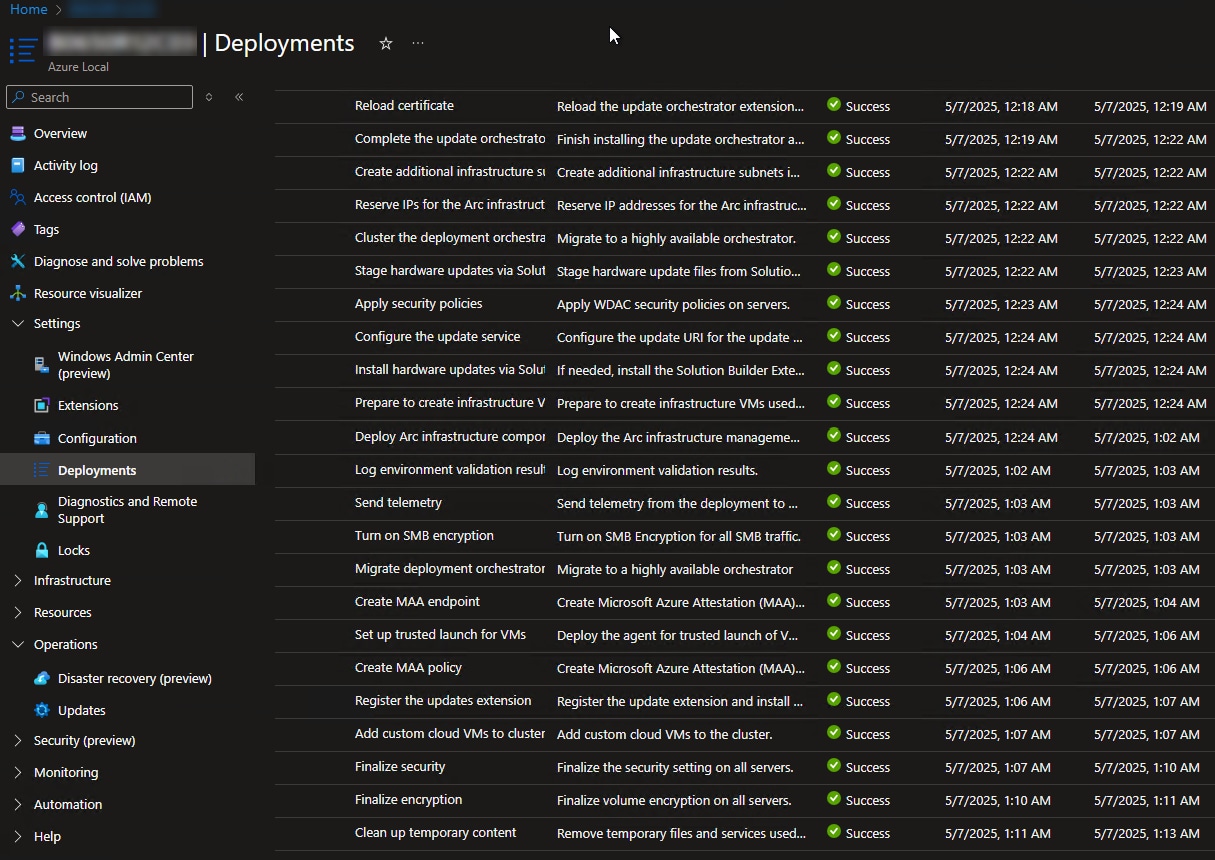
To view the deployment progress in the Azure portal, go to <Instance name > > Deployments. To view the latest update, click Refresh.
When the deployment is complete, all tasks display a status of Success.
Validation of deployment creation success
To access your Azure Local instance remotely, enable Remote Desktop Protocol (RDP).
For more information about enabling RDP, see Enable RDP.
Deploy an Azure Local instance using the Microsoft ARM template
Deploy an Azure Local instance using the Microsoft Azure Resource Manager (ARM) template.
Before you begin
Before using the Microsoft Azure Resource Manager (ARM) template to deploy an Azure Local instance, you must complete the prerequisite procedures. Procedures are correct at publication but are subject to change without notice. For the most current details, see Deploy Azure Local via Azure Resource Manager deployment template > Prerequisites.
Save the parameters file. Leave all remaining parameters set to their default values.
Select Review + create, and then click Create.
This step validates the deployment and creates the prerequisites that are required for the deployment.
When validation is complete, click Redeploy.
Select Edit parameters, load the parameter JSON file, and then click Save.
Select the Resource Group.
Change Deployment Mode from Validate to Deploy.
To begin the deployment, select Review + create, and then click Create.
To check the deployment progress, open a new browser window, go to the resource group, and then click the cluster resource. Go to Settings > Deployment, and then click Refresh.
NOTE:Deployment typically takes 2.5 to 3 hours under normal conditions. However, actual time may vary depending on factors such as environment complexity, network performance, and system load.
External SAN support for Azure Local
Explains how Azure Local integrates with external SAN storage and describes supported deployment architectures, storage protocols, and configuration workflows.
Overview
External SAN support enables hybrid deployments that combine Storage Spaces Direct (S2D) local storage with external SAN storage. This architecture allows organizations to reuse existing SAN investments while running Azure Local workloads.
The hybrid deployment model provides flexibility to place workloads on either local Storage Spaces Direct storage or external SAN storage based on performance, capacity, and operational requirements.
This documentation applies to post-deployment integration of external SAN storage with Azure Local clusters.
External SAN support deployment workflow
To integrate external SAN storage with Azure Local:
Optional CHAP authentication for additional security
SAN array requirements for Azure Local external SAN deployments
Lists the storage array requirements for integrating external SAN storage with Azure Local.
System requirements
To use external SAN storage with Azure Local, the SAN array must meet the following requirements:
LUNs presented to all cluster nodes
NTFS-formatted volumes for Cluster Shared Volumes (CSVs)
Consistent MPIO configuration across all nodes
Dedicated LUNs assigned to individual Cluster Shared Volumes
Planning considerations for Azure Local external SAN deployments
Describes the planning activities that should be completed before integrating external SAN storage with an Azure Local cluster.
Overview
Proper planning helps ensure a successful external SAN integration and reduces deployment issues. Before connecting SAN storage to an Azure Local cluster, review storage, network, and infrastructure requirements.
Planning activities
Before integrating external SAN storage with Azure Local:
Verify cluster deployment: Ensure that the Azure Local cluster is fully deployed and operational.
Plan the storage architecture: Determine which workloads will use Storage Spaces Direct (S2D) storage and which workloads will use external SAN storage.
Assess SAN capacity: Verify that sufficient LUN capacity is available to meet workload requirements.
Review SAN documentation: Consult SAN vendor documentation for LUN creation, zoning, masking, and connectivity requirements.
Prepare network infrastructure: Verify that Fibre Channel or iSCSI networking is configured and operational.
Document WWNs or IQNs: Collect initiator identifiers that will be used for zoning and LUN masking configuration.
Configuration considerations for Azure Local external SAN deployments
Describes deployment and configuration considerations for integrating external SAN storage with Azure Local.
External SAN deployments require consistent configuration across all cluster nodes and supporting infrastructure. Review the following considerations before configuring SAN connectivity:
Delay Fibre Channel zoning until after deployment: Do not zone Fibre Channel host bus adapter (HBA) World Wide Names (WWNs) to the SAN array until Azure Local deployment is complete. This helps prevent deployment and discovery issues.
Use identical HBA configurations: Configure all cluster nodes with the same HBA model, firmware version, and driver version.
Maintain MPIO consistency: Apply identical MPIO settings across all cluster nodes.
Plan for node reboots: Changes to MPIO policies require a rolling reboot of all cluster nodes.
Configure Fibre Channel SAN connectivity for Azure Local
Describes how to connect an Azure Local cluster to external SAN storage using Fibre Channel.
Before you begin
Before configuring Fibre Channel connectivity, ensure that the following requirements are met:
Azure Local cluster is fully deployed and running version 2604 or later.
Fibre Channel host bus adapters (HBAs) are installed on all cluster nodes.
Fibre Channel fabrics are configured with independent VSANs.
SAN array is accessible on the FC fabric with management access configured.
Procedure
Verify and enable Multipath I/O (MPIO).
Verify that Multipath I/O (MPIO) is enabled on all cluster nodes.
To enable the MPIO feature, run the following PowerShell command:
Document the WWPN associated with each HBA port and provide the information to the SAN administrator.
Configure SAN zoning and LUN masking.
Work with the SAN administrator to complete the following tasks:
Create Fibre Channel zones for each cluster node HBA port.
Configure LUN masking to present required LUNs to all cluster nodes.
Verify that zoning is active on all Fibre Channel switches.
Create the required LUNs on the SAN array.
Present the LUNs to all cluster nodes.
Verify LUN visibility.
To verify that all cluster nodes can access the presented LUNs, run the following PowerShell command:
Get-PhysicalDisk
Confirm that all expected LUNs report the following values:
Status: OK or Healthy
HealthStatus: Healthy
BusType: FC
NOTE:Do not initialize the disks after they are presented to the cluster. The disks must remain in RAW format so that Azure Local can use them as Cluster Shared Volumes (CSVs).
Results
All cluster nodes can access the Fibre Channel SAN LUNs, and the storage is ready for CSV configuration.
Configure iSCSI SAN connectivity for Azure Local
Describes how to connect an Azure Local cluster to external SAN storage by using iSCSI.
Before you begin
Before configuring iSCSI connectivity, ensure that the following requirements are met:
Azure Local cluster is fully deployed and running version 2604 or later.
Dedicated physical network adapters are available for iSCSI traffic. Virtual network adapters (vNICs) are not supported.
Network adapter firmware and drivers comply with Azure Local hardware catalog requirements.
The iSCSI target array is accessible on the network with management access.
Procedure
Enable the iSCSI Initiator service.
To enable and start the Microsoft iSCSI Initiator service on each cluster node, run the following PowerShell command:
The MSiSCSI service shows a Status of Running and a StartType of Automatic.
Configure network adapters for iSCSI.
To configure dedicated network adapters for iSCSI connectivity, assign a static IP address and disable DNS registration on each iSCSI adapter. Update the adapter name and IP address values to match the deployment requirements.
Document the IQN for each node and provide the information to the SAN administrator for host registration and LUN masking configuration.
Configure iSCSI target portals.
Configure iSCSI target portals for each available network path on every cluster node. Update the target and local IP address values to match the deployment environment.
To verify that the presented LUNs are visible to the cluster nodes, run the following PowerShell command:
Get-PhysicalDisk
Confirm that all expected LUNs report the following values:
Status: OK or Healthy
HealthStatus: Healthy
BusType: iSCSI
Results
All cluster nodes can access the iSCSI SAN LUNs through the configured network paths, and the storage is ready for multipath validation and Cluster Shared Volume (CSV) configuration.
MPIO for Azure Local external SAN deployments
Explains the role of Multipath I/O (MPIO) in Azure Local external SAN deployments.
Overview
Multipath I/O (MPIO) provides redundancy and load balancing for SAN storage connections. MPIO must be configured consistently across all Azure Local cluster nodes.
To integrate MPIO with Azure Local external SAN deployments, complete the folowing:
Lists the default Multipath I/O (MPIO) settings included with Azure Local version 2604 and later.
Default MPIO settings for Azure Local version 2604 and later. The following table lists the default MPIO settings that Azure Local version 2604 and later applies to all cluster nodes. Review these values before making configuration changes to ensure that any customizations align with your storage array recommendations and operational requirements.
Setting
Default value
PathVerificationState
Enabled
PathVerificationPeriod
30
PDORemovePeriod
20
RetryCount
6
RetryInterval
3
CustomPathRecovery
Disabled
CustomPathRecoveryTime
20
DiskTimeoutValue
60
Load Balance Policy
Round Robin (RR)
NewDiskPolicy
OfflineShared
Register storage vendor with MPIO
Describes how to register your storage vendor with Microsoft Device Specific Module (MSDSM) for MPIO management.
Before MPIO can manage storage array LUNs, your storage vendor must be registered with Microsoft Device Specific Module (MSDSM). Registering your storage vendor allows MPIO to claim and manage the storage devices presented to Azure Local.
Procedure
Verify whether your storage vendor is already registered.
To check whether the vendor and product combination is already registered with MSDSM for Dell PowerStore arrays, run the following PowerShell command:
If the command returns a result, the storage vendor is already registered with MSDSM and you can skip Step 2. If no result is returned, proceed to Step 2 to register the vendor.
Register the storage vendor.
To register the Dell PowerStore storage array with MSDSM if the vendor is not already registered, run the following PowerShell command:
if (!$MSDSMSupportedHW) {
	New-MSDSMSupportedHW -VendorId "DellEMC" -ProductId "PowerStore"
The Dell PowerStore vendor and product identifier are registered with MSDSM on the cluster node. Repeat this step on all cluster nodes to ensure a consistent MPIO configuration.
Results
The Dell PowerStore storage array is registered with MSDSM, allowing MPIO to claim and manage the presented SAN LUNs.
Configure the MPIO load-balancing policy
Describes how to configure the MPIO load-balancing policy for SAN-connected storage.
MPIO uses a load-balancing policy to distribute I/O traffic across available storage paths. Configure the load-balancing policy on all Azure Local cluster nodes to ensure consistent path selection behavior.
Procedure
To set the MPIO load-balancing policy to Round Robin (RR), run the following PowerShell command:
MPIO uses the Round Robin load-balancing policy to distribute storage traffic across available paths on all cluster nodes.
Configure Dell PowerStore MPIO timers
Apply Dell PowerStore MPIO timer settings and perform the required rolling reboot on Azure Local cluster nodes.
After configuring the Dell PowerStore MPIO timer settings and the MPIO load-balancing policy, perform a rolling reboot of each cluster node to ensure that the configuration changes take effect.
Perform this procedure on one node at a time to maintain cluster availability.
Procedure
Pause the node and move workloads to other cluster nodes before performing maintenance.
The Dell PowerStore MPIO timer settings and load-balancing policy are applied consistently across all cluster nodes, and storage is synchronized and healthy before workloads resume.
Verify the MPIO configuration
Describes how to verify MPIO devices, path availability, and load-balancing configuration on Azure Local nodes.
After configuring MPIO, verify that all SAN LUNs are claimed by MPIO, multiple storage paths are available, and the configured load-balancing policy is applied consistently across all cluster nodes.
Procedure
Verify that MPIO devices are detected.
To list all storage devices managed by MPIO, run the following command:
Get-MPIOAvailableHW
Review the output to confirm that the expected storage devices are available for MPIO management.
Verify MPIO paths.
To display path information for each SAN LUN, run the following command
Get-MSDSMPathInfo
Review the output to confirm that each LUN has multiple active paths.
Verify SAN disk health.
To check the health and operational status of all SAN-connected disks, run the following command:
# Verify all LUNs have multiple paths
Get-PhysicalDisk | Format-Table FriendlyName, BusType, OperationalStatus, HealthStatus
Verify that:
The expected SAN disks are visible.
The disk health status is Healthy.
The operational status indicates normal operation.
Verify path status and load-balancing policy.
To verify path state and load-balancing configuration, run the following command:
The configured load-balancing policy is applied to all SAN LUNs.
Results
MPIO devices, storage paths, SAN disks, and load-balancing policies are verified and operating as expected.
Post-deployment verification for Azure Local external SAN deployments
Explains the validation and monitoring activities that should be performed after integrating external SAN storage with Azure Local.
After configuring external SAN connectivity, verify that the SAN LUNs are visible to all cluster nodes, that Multipath I/O (MPIO) is operating correctly, and that storage paths remain healthy during normal cluster operations.
Complete the following activities after configuring Fibre Channel or iSCSI SAN connectivity:
Verify SAN connectivity for Azure Local external SAN deployments
Describes how to verify that all Azure Local cluster nodes can access the SAN LUNs presented by the storage array.
Before using external SAN storage for workloads, verify that all cluster nodes can detect and access the presented SAN LUNs.
Procedure
On each cluster node, run the following command:
Get-PhysicalDisk
Verify the disk status.
Review the output and confirm that all expected SAN LUNs report the following values:
Status: OK or Healthy
HealthStatus: Healthy
BusType: FC (Fibre Channel) or iSCSI
Verify disk consistency across all nodes.
Confirm that the same number of SAN disks is visible on every cluster node.
Results
All cluster nodes can access the expected SAN LUNs, and the presented storage is healthy and available for workload use.
Verify MPIO path availability for SAN storage
Describes how to verify that SAN LUNs are accessible through multiple active MPIO paths on Azure Local cluster nodes.
After configuring Multipath I/O (MPIO), verify that each SAN LUN has multiple active paths and that path failover protection is functioning as expected.
Procedure
To verify the number of paths per LUN, run the following command:
If inactive paths are detected, work with the SAN administrator to identify and resolve zoning, masking, connectivity, or storage path issues.
Results
All SAN LUNs are accessible through multiple active MPIO paths, providing redundancy and load balancing for storage traffic.
Monitor SAN path health for Azure Local external SAN deployments
Describes how to monitor SAN path health, failover events, and cluster health in an Azure Local external SAN environment.
After configuring SAN connectivity and MPIO, regularly monitor storage paths to identify path failures, failover events, and cluster health issues before they affect workload availability.
Procedure
Review MPIO-related events:
To review MPIO-releated events, select Event Viewer > Windows Logs > System.
Look for events generated by the mpio event source.
Monitor storage performance.
Click Performance Monitor to:
Track disk I/O performance metrics.
Monitor path failover events.
Monitor path recovery events.
Verify cluster health.
To verify cluster health, run the following command:
Get-ClusterResource
Get-ClusterNode | Select-Object Name, State
Results
SAN path health, failover activity, storage performance, and cluster health are monitored and operating as expected.
Create and use external SAN storage in Azure Local
Explains how to provision external SAN storage and make it available for Azure Local workloads.
After verifying SAN connectivity and Multipath I/O (MPIO) configuration, you can provision external SAN storage for Azure Local workloads. Using SAN-backed Cluster Shared Volumes allows virtual machines and applications to consume external SAN storage while remaining highly available across the cluster.
To add the volume to Cluster Shared Volumes, run the following command:
Add-ClusterSharedVolume -Name "Cluster Disk X"
Results
The SAN LUN is available as a Cluster Shared Volume and can be used by Azure Local workloads.
Configure workload storage paths on SAN-backed Cluster Shared Volumes
Describes how to configure workload storage locations on SAN-backed Cluster Shared Volumes.
After creating Cluster Shared Volumes, configure workload storage locations so that virtual machines and applications use SAN-backed storage.
Procedure
Log in to the Azure portal and go to your Azure Local cluster resource.
Select Settings > Storage path.
Select + Add storage path.
Enter the Cluster Shared Volume path. For example:
C:\ClusterStorage\Volume1
Confirm and save.
Repeat for each SAN CSV.
Results
Virtual machines and applications store data on SAN-backed Cluster Shared Volumes.
Troubleshoot Azure Local external SAN deployments
Provides troubleshooting guidance for common issues encountered when integrating external SAN storage with Azure Local.
External SAN storage integration issues typically involve storage path visibility, LUN presentation, or multipath failover. When troubleshooting SAN connectivity, verify storage connectivity, MPIO configuration, zoning, masking, and hardware health.
Troubleshoot MPIO paths not visible
Describes how to diagnose and resolve issues where MPIO paths are not visible or are not functioning correctly.
Use the following steps when you observe any of these symptoms:
SAN LUNs are visible, but expected MPIO paths are missing.
Storage devices do not appear to be managed by MPIO.
Storage path redundancy is unavailable.
Procedure
Verify HBA drivers.
To verify that FC or iSCSI drivers are installed and current, run the following command:
Confirm that Fibre Channel zoning is configured correctly and active on all switches.
Verify MPIO device claiming.
To check MPIO automatic claim settings, run the following command:
Get-MSDSMAutomaticClaimSettings
Verify LUN visibility.
To confirm that the SAN LUNs are visible, run the following command:
Get-PhysicalDisk -CanPool $true
Review Windows Event Viewer for MPIO-related errors and warnings.
Results
MPIO paths are visible and operating correctly.
Troubleshoot SAN LUN masking issues
Describes how to diagnose and resolve SAN LUN masking issues that prevent LUN visibility across cluster nodes.
Use the following steps when you observe any of these symptoms:
SAN LUNs are visible on some nodes but not others.
Newly presented LUNs do not appear on cluster nodes.
Inconsistent storage visibility across the cluster.
Procedure
Verify SAN LUN masking.
Confirm that the SAN array masking configuration is correct.
Verify initiator identifiers.
Confirm that all node WWPNs or IQNs are included in the masking configuration.
Verify Fibre Channel zoning.
Verify that Fibre Channel zoning includes all cluster node HBA ports.
Check switch restrictions.
Review Fibre Channel switches for port-level zoning restrictions.
Review vendor documentation.
Consult SAN vendor documentation for array-specific LUN masking requirements and procedures.
Results
All SAN LUNs are visible to all cluster nodes.
Troubleshoot SAN path failover issues
Describes how to diagnose and resolve SAN storage path failover issues.
Use the following steps when you observe any of these symptoms:
Storage traffic does not fail over to alternate paths.
MPIO path recovery does not occur.
Storage connectivity is lost during path failures.
Procedure
Verify MPIO configuration.
Confirm that MPIO is enabled on all cluster nodes.
Verify policy consistency.
Confirm that identical MPIO policies are configured across all cluster nodes.
Verify HBA firmware.
Verify that HBA firmware versions are current and supported.
Verify hardware health.
Inspect Fibre Channel or iSCSI adapters, ports, and cables for hardware issues.
Review SAN logs.
Review SAN array logs for connectivity, path, or controller-related issues.
Review vendor documentation.
Consult vendor-specific MPIO guidance for the storage platform.
Results
Storage paths fail over and recover correctly when path failures occur.
Deploy Azure Local using Local Identity with Azure Key Vault
This chapter describes the additional requirements, configuration differences, and deployment considerations for deploying an Azure Local instance using Local Identity with Azure Key Vault (also known as AD‑less deployment).
This chapter does not replace the standard Azure Local deployment workflow. Unless explicitly stated otherwise, all deployment steps follow the procedures that are described in:
Chapter 3: Solution Deployment
Chapter 4: Deploying Azure Local Instance with Azure Stack HCI OS, version 24H2 or later
About Local Identity with Azure Key Vault
Overview
Azure Local can be deployed without Active Directory by using a local identity model with Azure Key Vault, previously known as AD-less deployment. This deployment option is available starting with Azure Local version 2411 and later.
In a local identity deployment:
A dedicated local administrator account is used on each machine.
Certificate‑based authentication is configured cluster‑wide.
Azure Key Vault is used to securely back up secrets such as BitLocker keys and other critical configuration data that is required for secure cluster operation.
Benefits of local identity with Azure Key Vault (without Active Directory)
Minimal edge infrastructure: Enables secure identity and secret handling in environments that do not use Active Directory.
Secure secret store: Azure Key Vault stores sensitive items such as BitLocker keys and node passwords, reducing the risk of unauthorized access and improving overall security.
Simplified management: Consolidates deployment and local identity secrets in a single vault, making them easier to manage and retrieve.
Simplified deployment: Azure portal workflows store required secrets in Azure Key Vault, reducing reliance on Active Directory and helping simplify Operational Technology network firewall configurations.
Key differences from Active Directory–based deployments
Key differences between Active Directory–based and Local Identity–based Azure Local deployments. The following table summarizes the functional differences between Active Directory–based and Local Identity–based Azure Local deployments
Area
Active Directory deployment
Local Identity deployment
Identity provider
Active Directory
Local administrator account
Authentication
AD objects
Certificate‑based authentication
Secret storage
Cluster and AD
Azure Key Vault
Domain join
Required
Not supported
AD preparation
Required
Not applicable
Deployment prerequisites for Azure Local deployment using local identity
Dell Technologies assumes that the management services that are required for the operating system deployment and Azure Local instance configuration are in the existing infrastructure where the instance is deployed.
Create a local user and add to the local Administrators group
Create a dedicated local administrative user on each Azure Local node for deployment and cluster management operations.
Before you begin
Azure Local deployments that use local identity require a non built-in local administrator account. This account is used for cluster-wide management operations, such as adding or repairing nodes, and must be consistent across all nodes in the Azure Local instance.
NOTE:You are responsible for life cycle management of this account, including expiration, rotation, and security. The default local policy sets a maximum password age of 42 days. This can be modified using PowerShell or by changing the underlying password policy configuration.
Use the same username and password on all machines. The password must meet Azure complexity requirements and include at least 14 characters with a combination of lowercase letters, uppercase letters, numbers, and special characters.
Procedure
On each Azure Local node, create a new local user account, and update the $AdminUser value accordingly.
NOTE:Do not use the built-in Administrator account.
# Create new dedicated user

$AdminUser = '<DedicatedAdminUser>'
# Sample data:
# $AdminUser = 'adless-admin'
$Credentials = Get-Credential -UserName $AdminUser -Message 'Enter password:'
$Description = 'Local AD-less user'
New-LocalUser -Name $AdminUser -Password $Credentials.Password -FullName $AdminUser -Description $Description

# Add user to local admin group
Add-LocalGroupMember -Group 'Administrators' -Member $AdminUser

# Optional: Validate the new user account
Get-LocalGroupMember -Group administrators
# The output should include the user account specified by $AdminUser.
# If it is not listed, the account was not created or added successfully.
Deploy the Azure Local instance using local identity with Azure Key Vault
You can deploy an Azure Local instance in the following ways:
Azure portal deployment with Quickstart Template (template deployment), which uses the UI in the Azure portal to deploy ARM templates. This method is not documented in this guide.
Deploy Azure Local Instance using Azure portal
The Azure portal wizard guides you through steps to create an Azure Local instance.
You can use the wizard to define all instance‑level and machine‑level configuration settings. The wizard guides you through the following windows:
Basics
Configuration
Networking
Management
Security
Advanced
Tags (optional)
Validation
Review and create
To create an Azure Local instance:
To start the wizard from Home > Azure Local, select Deploy Azure Local.
Under Get Started, in Deploy Azure Local, select Create instance.
Specify the Subscription name, Resource group, and Instance name.
Instance name = Cluster Name Object (CNO)
For Cluster options, select either Standard or Rack aware.
For Identity provider, select Local identity with Azure Key Vault.
Select the machines to be added to the Azure local Instance. Click Add machines.
The required extensions are automatically installed during this step.
When the extensions are installed and the status shows as Ready, click Validate selected machines.
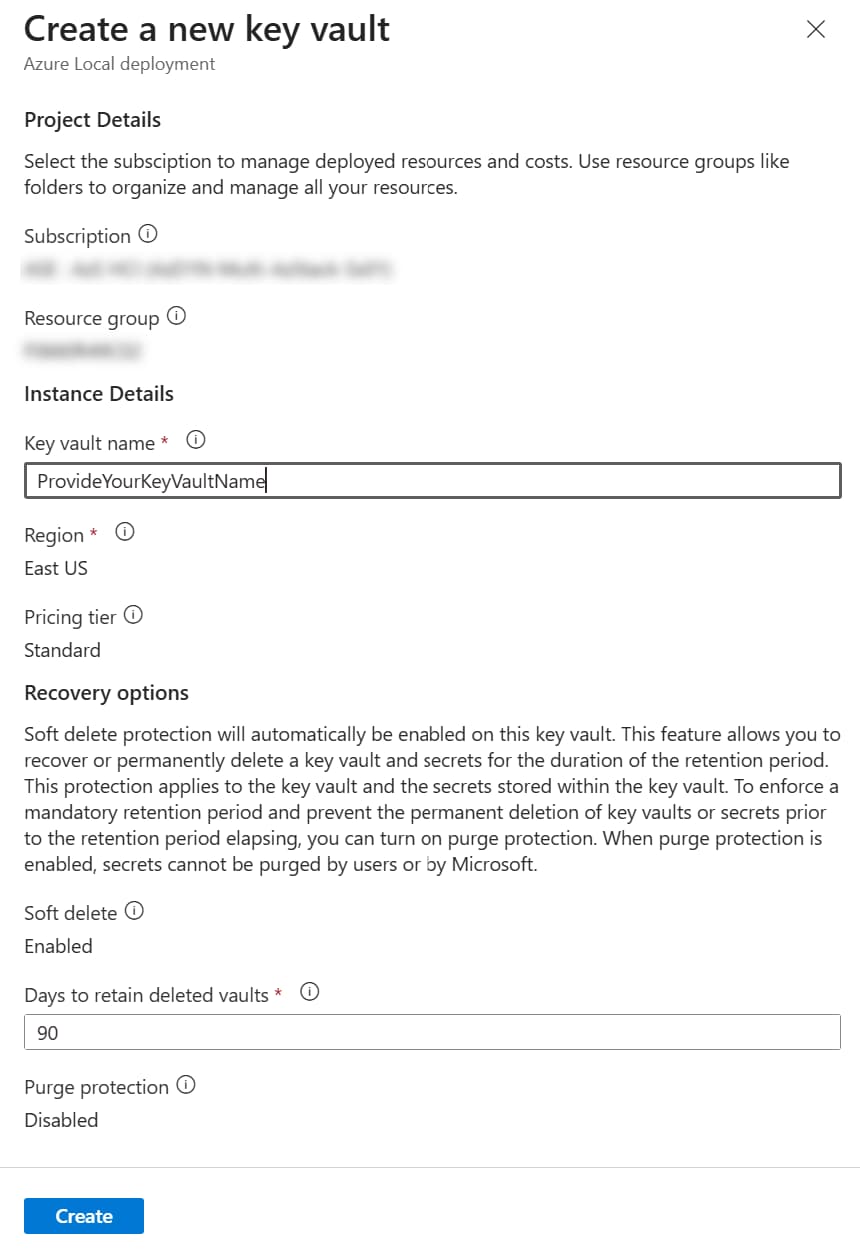
To create a new key vault, enter a Key vault name, and then click Create a new key vault.
NOTE:
If a previously created key vault for a decommissioned instance with the same name exists, you must first delete and purge the old key vault before creating one.
Azure Local does not support deploying a cluster by using an existing Azure key vault that has private endpoints enabled.
Create a new key vault
To go to the next window, click Next: Configuration.
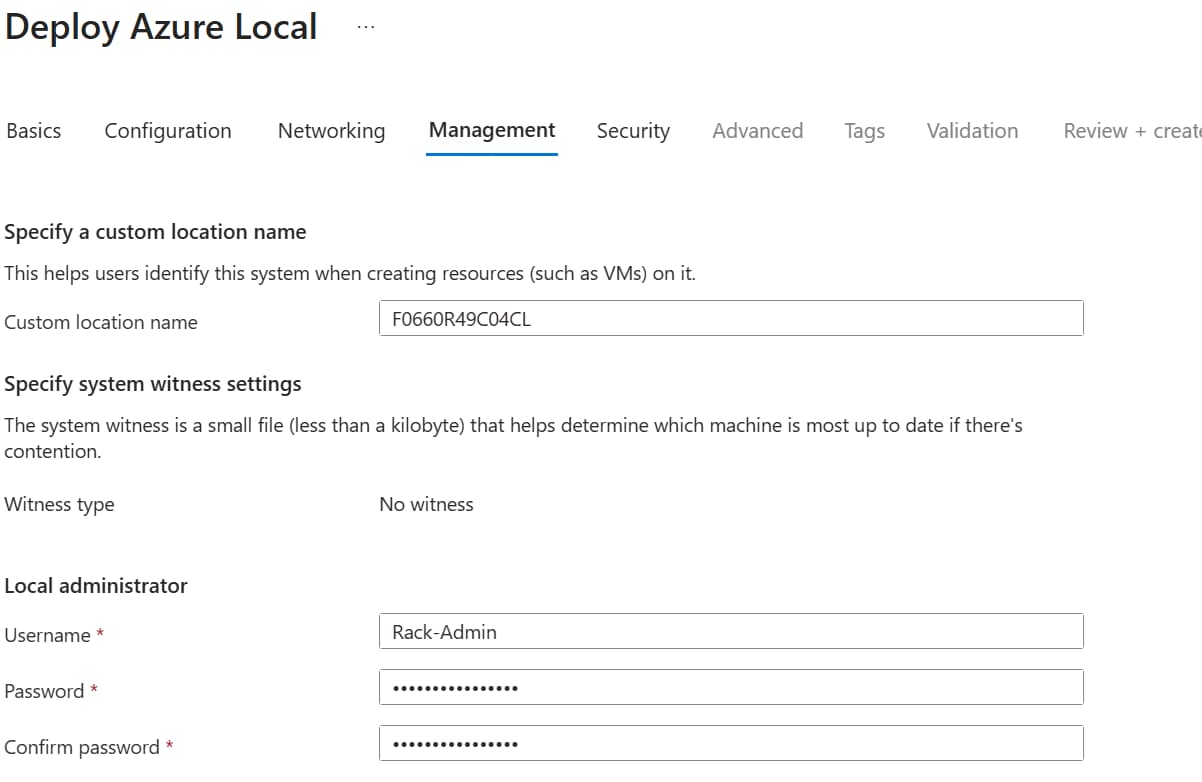
In the Configuration window, enter details about the instance.
To go to the next window, click Next: Networking, shown in the following figure.
Deployment wizard - Networking window
In the Networking window, for Storage connectivity, choose whether you use a network switch for the storage network.
Under Group network traffic types by intent, based on your network topology, select the Networking pattern. For a single- machineinstance, Dell Technologies recommends that you select Group Management and Compute (no storage).
The following table shows the Quality of Service (QoS) flow priorities for each network type:
QoS priorities for network intents. The table shows the QoS flow priorities that are based on traffic class for each network type.
Traffic class
Purpose
QoS flow
ETS bandwidth allocation
3
RDMA (SMB Direct)
Enabled
50 percent
7
Cluster network
Disabled
10 GbE equals 2 percent
Greater than 25 GbE equals 1 percent
0-2, 4-6
0 - Best-effort traffic
Disabled
Remaining percentage distributed across the traffic classes
Under Provide intent details, for management-network-intent creation, select the network adapters.
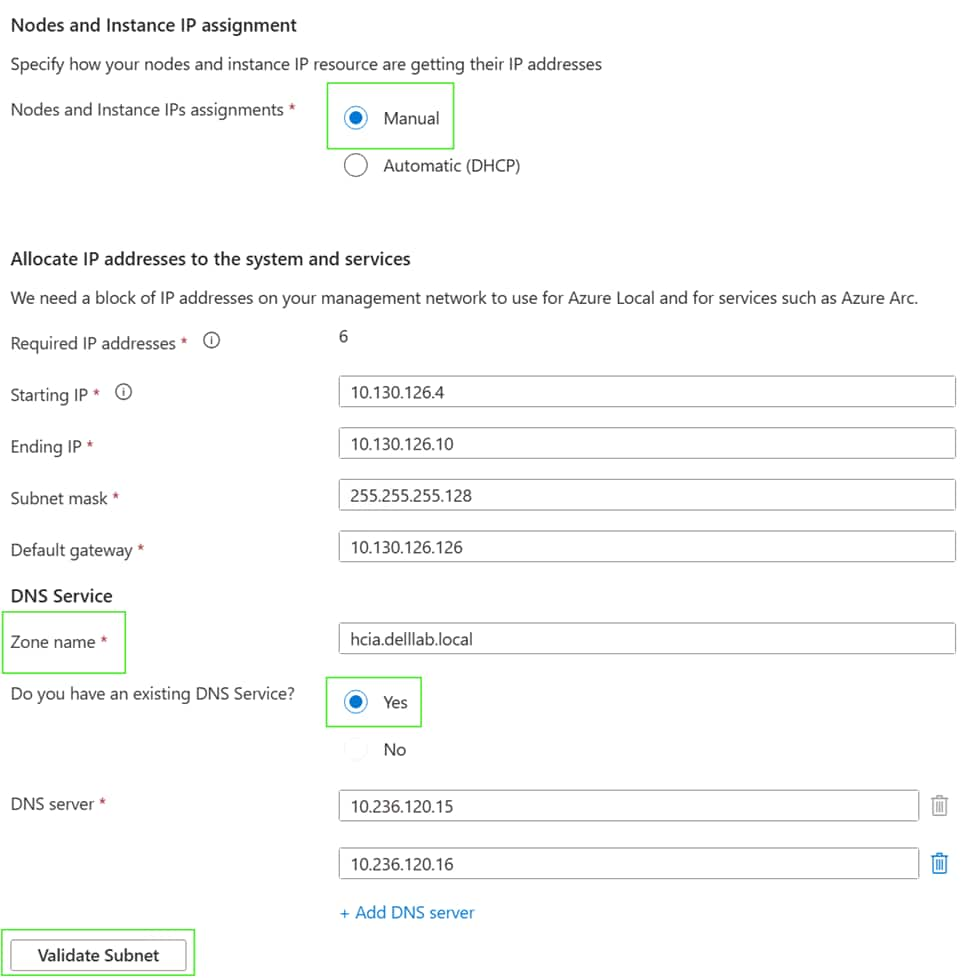
Under Allocate IP addresses to the system and services, provide the required details as shown in the following figure.
Allocate IP addresses
Under Compute_Management, to update information such as network intent, data center bridging, and adapter properties including Jumbo Frame size and RDMA protocol, click Customize network settings.
NOTE: For management network intents, RDMA must be disabled, as shown in the following figure.
Customize network values window with disabled RDMA protocol
NOTE:Microsoft recommends that you set System Traffic Priority to 7 for new cluster deployments. A priority value of 5 is also supported and acceptable. Ensure that the QoS settings on the top‑of‑rack (ToR) switches match the QoS settings that are configured in the host operating system.
Under Security shown in the following figure, Dell Technologies and Microsoft recommends that you choose Recommended security settings, which offers the highest level of security settings.
Deployment wizard - Security window
Click Next: Advanced.
Under Advanced, choose Create workload volumes and required infrastructure volumes.
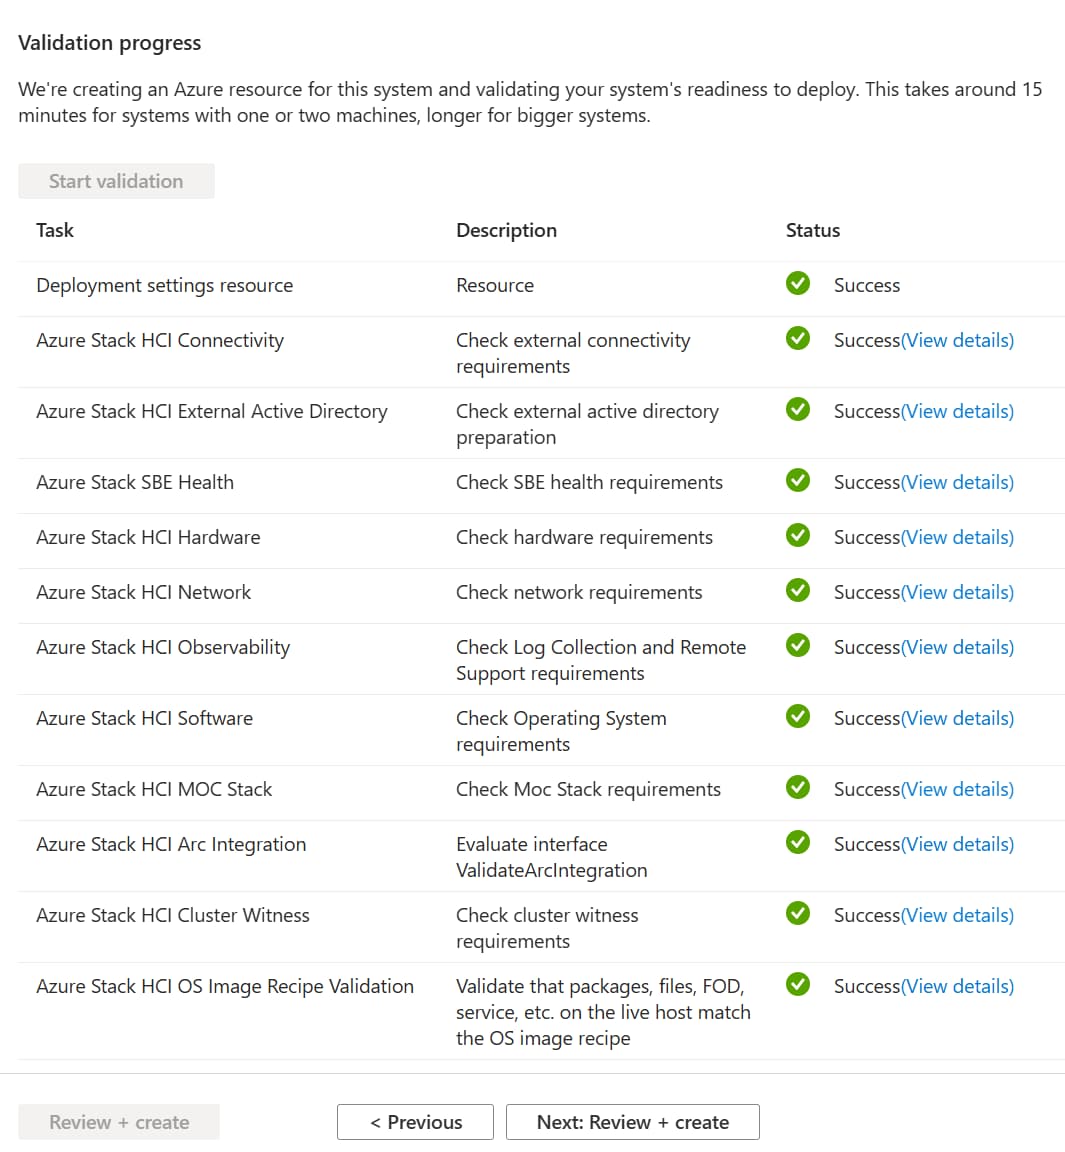
The system creates a resource object and its components for the instance. The validation process typically completes within 15 minutes for a single-server deployment, though it may take longer depending on system conditions or environmental factors. This process assesses the system readiness for cluster deployment.
Click Next: Review + create.
The Review + create window shows the configuration information that you entered or selected in the previous steps for creating the instance. To return to a previous step to change any settings, click Previous.
To start the instance creation process, review and confirm your settings, and then click Create .
When the deployment is complete, all tasks display a status of Success.
Validation of deployment creation success
To access your Azure Local instance remotely, enable Remote Desktop Protocol (RDP).
For more information about enabling RDP, see Enable RDP.
Deploy an Azure Local instance using the Microsoft ARM template
Deploy an Azure Local instance using the Microsoft Azure Resource Manager (ARM) template.
Before you begin
Before using the Microsoft Azure Resource Manager (ARM) template to deploy an Azure Local instance, you must complete the prerequisite procedures. Procedures are correct at publication but are subject to change without notice. For the most current details, see Deploy Azure Local via Azure Resource Manager deployment template > Prerequisites.
In the Azure portal, go to Home, and then click Create a Resource.
Under Template deployment (deploy using custom templates) , click Create.
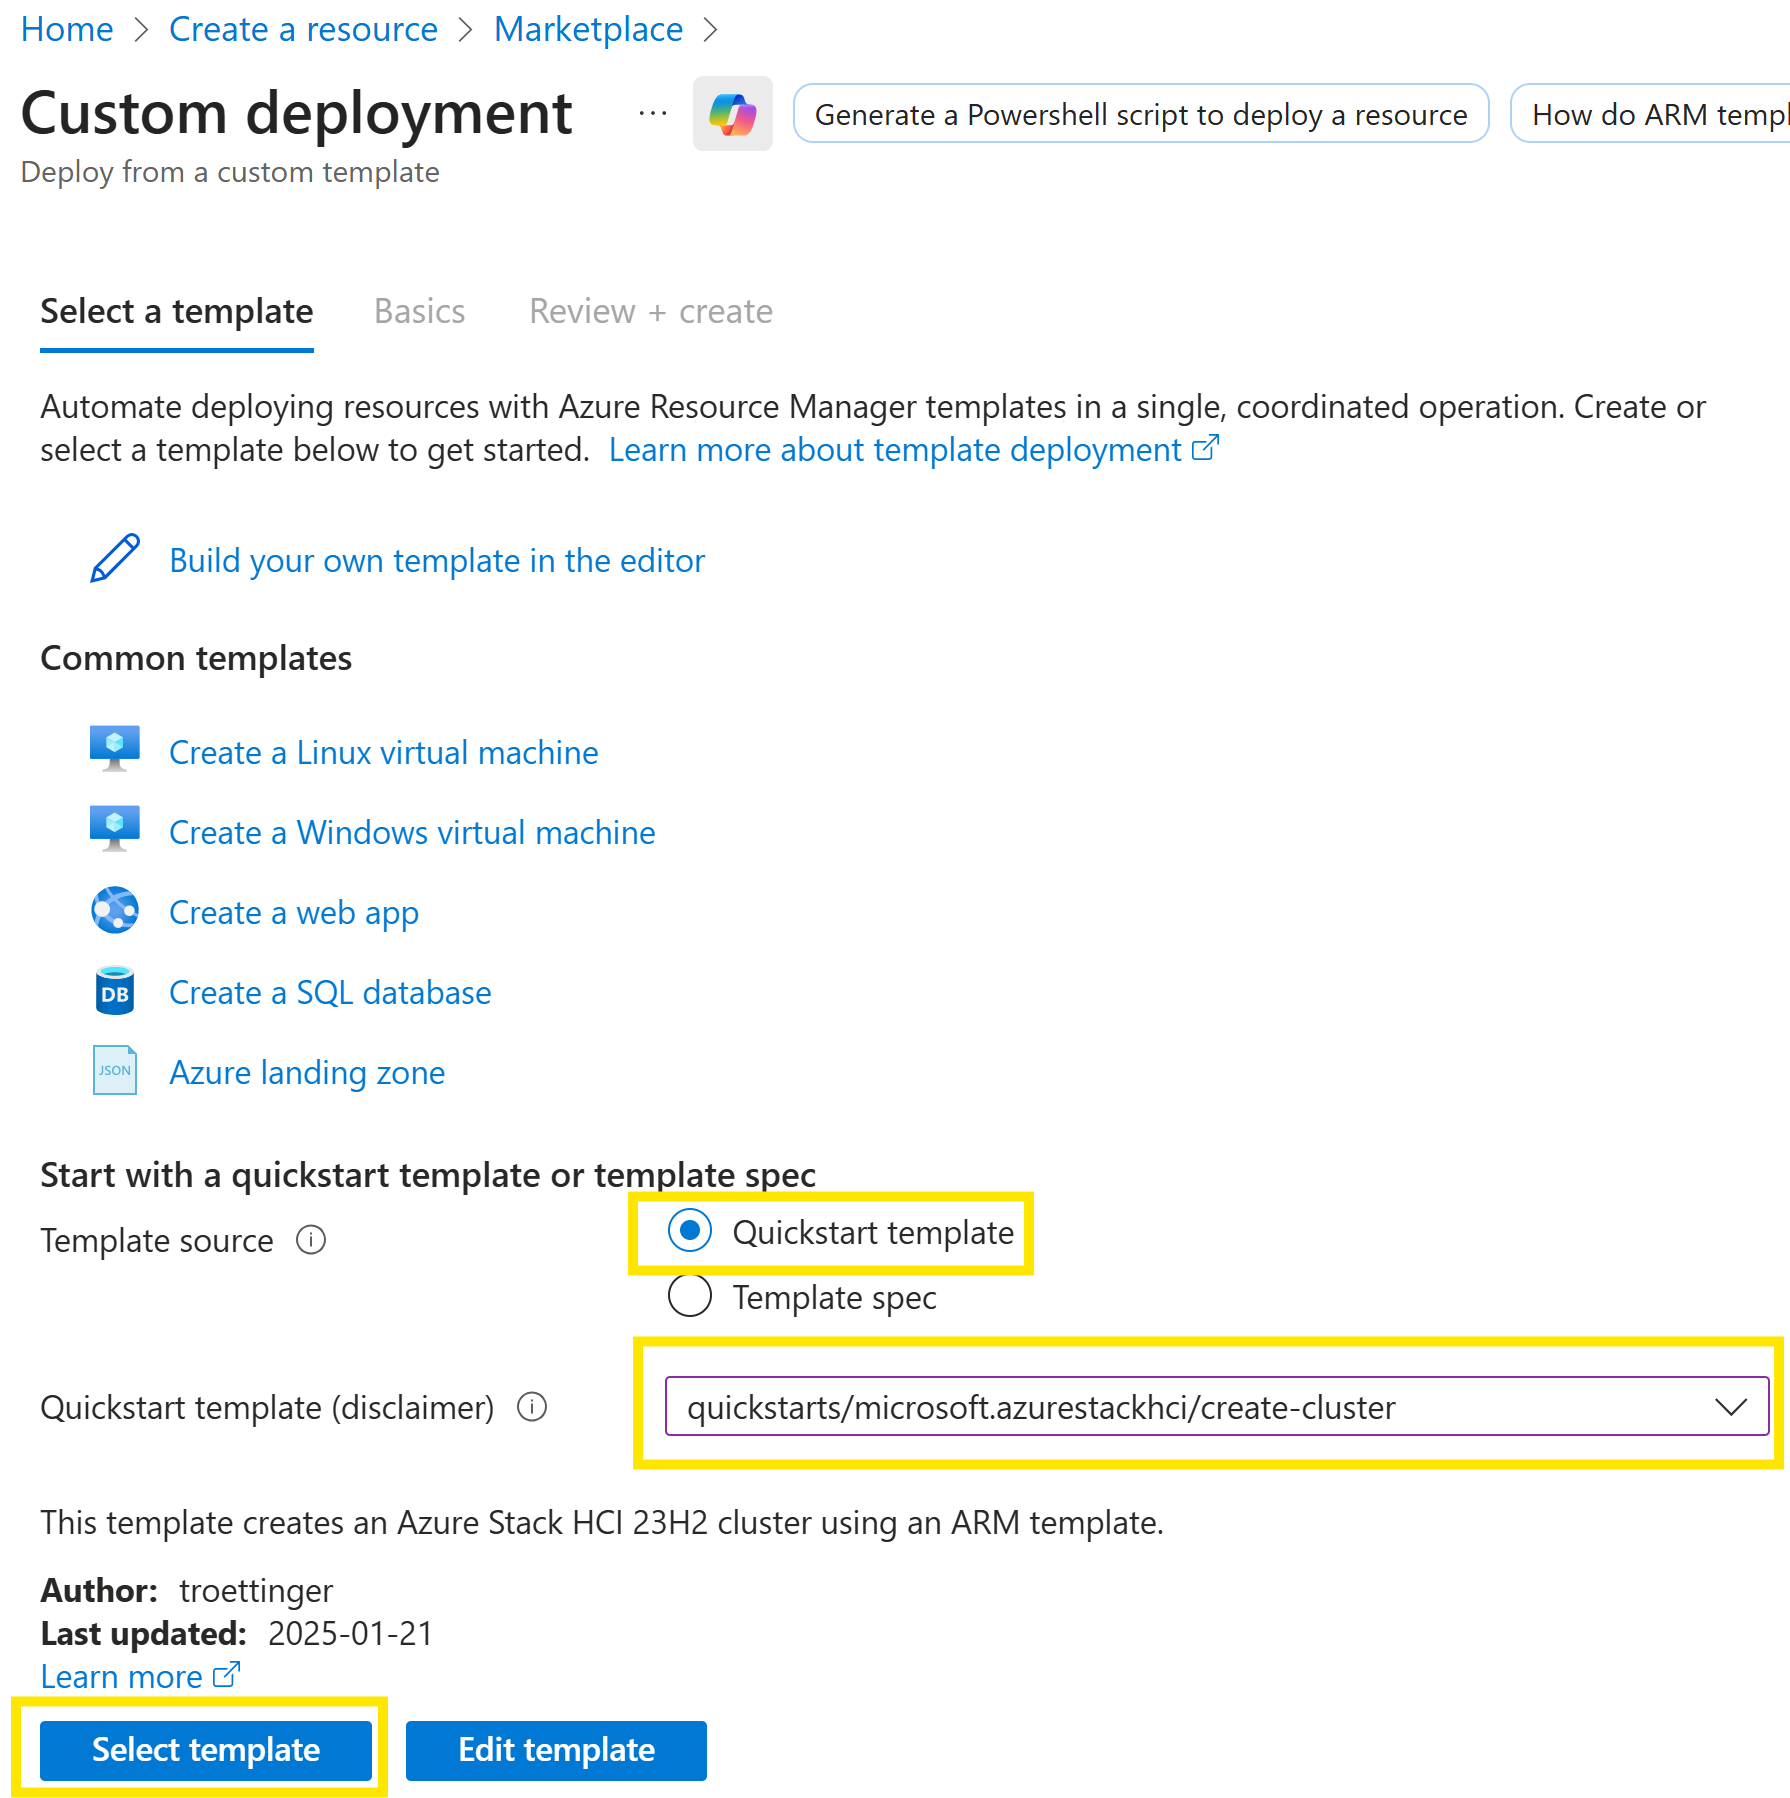
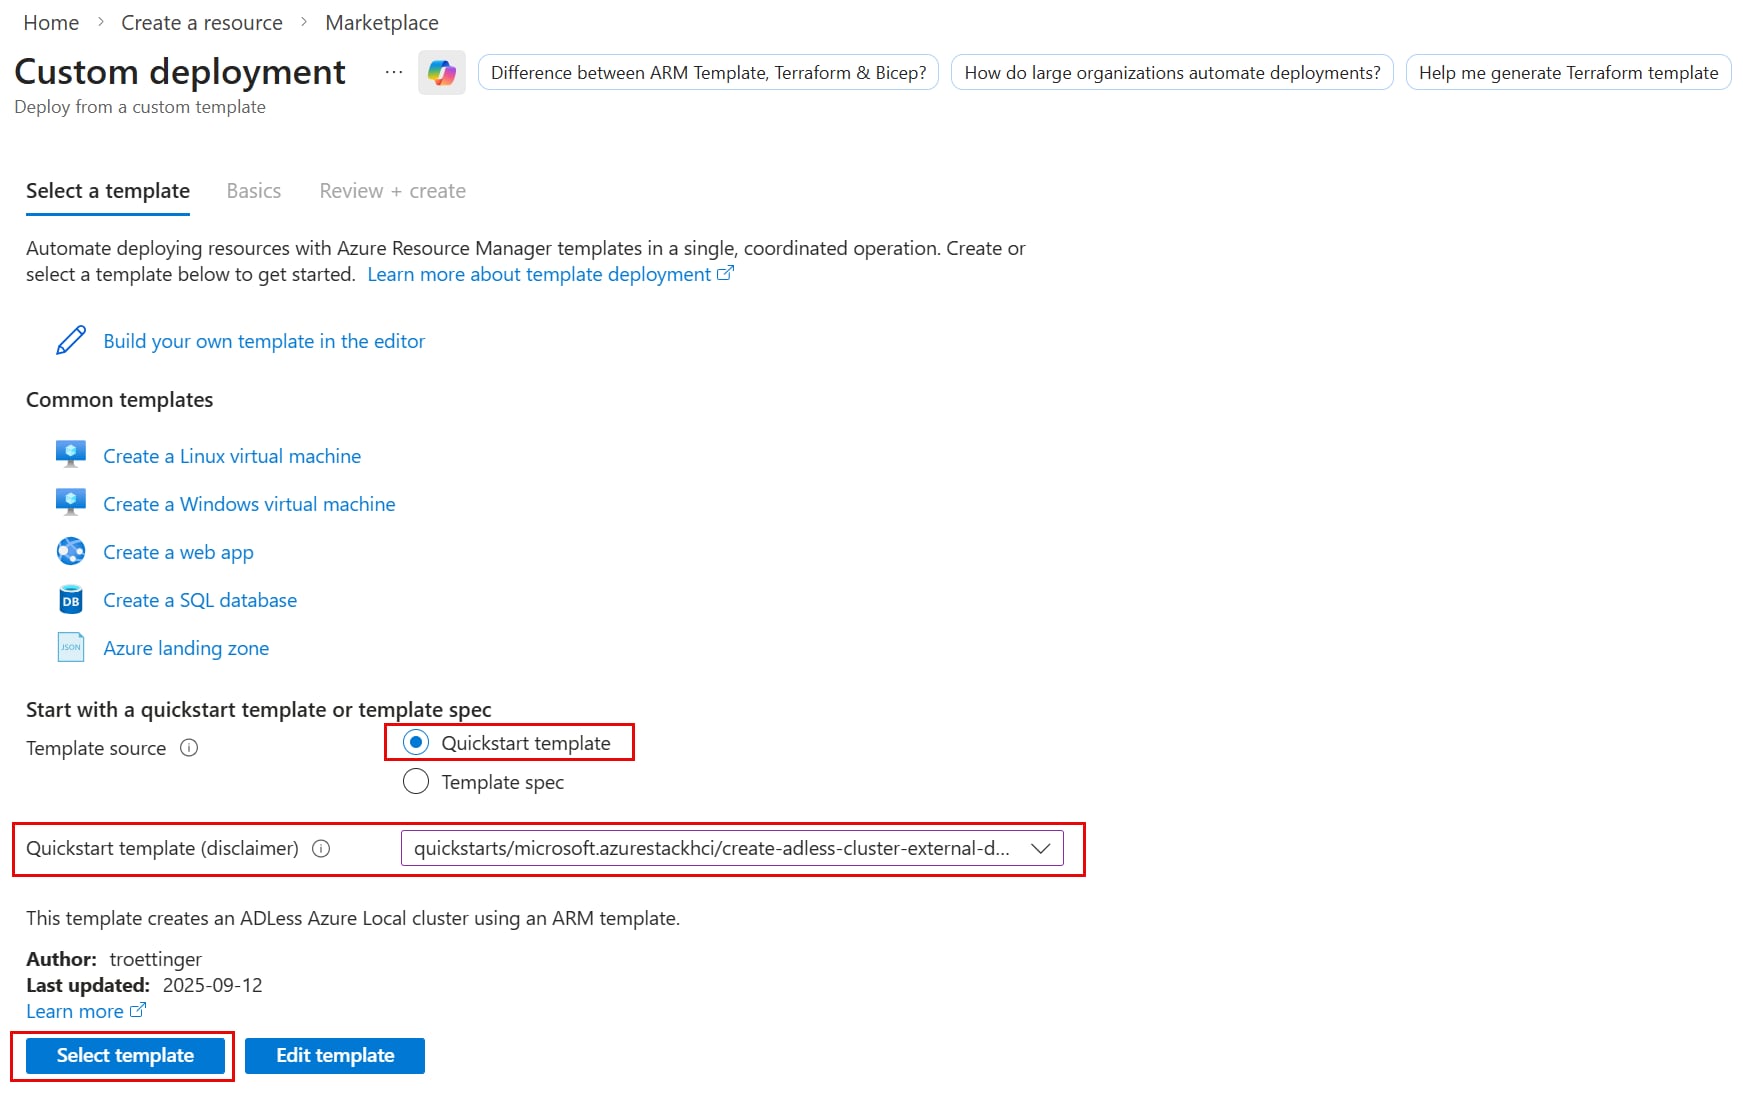
From the Start with a quickstart template or template spec, select Quickstart template as the template source.
Custom deployment window > Select a template
From the Quickstart template (disclaimer) list, select the Azure Local AD‑less cluster template, quickstarts/microsoft.azurestackhci/create-adless-cluster-external-dns-public-preview, and then click Select template.
On the Basics tab, select the resource group where the Arc-enabled servers are registered for the deployment.
Select Region, and then, in Deployment Mode, select Validate.
Enter the Key Vault Name and Cluster Name.
Enter the Local Admin credentials.
Enter the following data from information collected in the previous steps:
Arb Deployment App ID
Arb Deployment App Secret
Arb Deployment SPN Object ID
Azure Stack HCI Resource Provider Object ID
To collect Arc Machine Resource IDs, run (Get-AzConnectedMachine -ResourceGroupName "<your-resource-group>").Id on one of the machines. Enter the details in Arc Machine Resource IDs.
Enter the following:
Subnet Mask
Default gateway
Starting IP address
Ending IP address
DNS Servers IP
NOTE:Azure Local deployment requires six IP addresses for the system and services.
Under Physical Nodes Settings, enter the Hostname and IP addresses for the machines, for example:
Under Networking type, select SingleServerDeployment.
Under Networking Pattern, choose Select ConvergedManagementCompute to Group management and compute traffic.
Set Storage Connectivity Switchless to:
True for switchless networking
False for switched networking
Click Edit Parameters.
NOTE:For an example of a parameter file that shows the format of various inputs, see azuredeploy.parameters.json on GitHub.
Edit Network intent details based on the network topology that you are using for the deployment.
The following table shows the Quality of Service (QoS) flow priorities for each network type:
QoS priorities for network intents. The table shows the QoS flow priorities that are based on traffic class for each network type.
Traffic class
Purpose
QoS flow
ETS bandwidth allocation
3
RDMA (SMB Direct)
Enabled
50 percent
7
Cluster network
Disabled
10 GbE equals 2 percent
Greater than 25 GbE equals 1 percent
0-2, 4-6
0 - Best-effort traffic
Disabled
Remaining percentage distributed across the traffic classes
The following script shows an example from the ARM template and demonstrates how the Local Identity (with Azure Key Vault) deployment differs from the Active Directory deployment. The configuration that is shown corresponds to one of the possible network patterns “convergedManagementCompute.”
For readability, unrelated sections are not shown and are marked with dots (....).
For more information, see Full Azure Local/Azure Stack HCI 'create-cluster' template and parameter examples that are published in the Azure Quickstart Templates GitHub repository.
Management tool compatibility for Azure Local with Azure Key Vault
Management tooling support varies across the Azure Local ecosystem for environments that use Azure Key Vault for identity management.
Management tools
The following table provides the management tools that are supported for Azure Local environments that use Azure Key Vault for identity management:
Management tools. Table lists the management tools compatibility for Azure environments that use Azure Key Vault for identity management.
Category
Tools
Notes
Supported
PowerShell
Azure Monitor
Azure portal
Fully supported for typical management and monitoring workflows.
Unsupported/Limited support
Windows Admin Center
System Center Virtual Machine Manager (SCVMM)
Not supported or only partially supported - avoid relying on these as primary management tools.
Mixed compatibility
Microsoft Management Consoles (MMCs)
Compatibility varies by scenario.
Some MMC tools such as Hyper-V Manager, and Failover Cluster Manager may not work in all the scenarios.
Test critical workflows before using MMCs in production.
Post-deployment Updates and Maintenance
Post-deployment best practices
Dell Technologies recommends that you follow the guidelines that are described in this section.
Antivirus exclusions
As part of best practices, Dell Technologies and Microsoft recommend that you plan appropriate antivirus exclusions.
Azure Local instance machines by default are deployed and configured with security features including Microsoft Defender Antivirus.
If you prefer to use non-Microsoft antivirus and security software, Dell Technologies and Microsoft recommend that your vendor has validated your preferred software for Azure Local.
Download Connector is a component in the Solution Builder Extension (SBE) package that automates the download of new SBE bundles as they become available for your Azure Local instance.
When an SBE that includes the Download Connector is installed on your instance, manual downloading and importing of subsequent versions is no longer required. The update service automatically retrieves the next available SBE, similar to how solution updates are handled.
Download Connector is part of SBE version 4.1.2505.1501 and later. These versions also feature system and update health checks that proactively verify connectivity to the required remote resource before downloading the next SBE. System health checks run daily, while update health checks occur at the beginning of the update process.
Download Connector firewall requirements
The Solution Builder Extension (SBE) Download Connector requires outbound Internet access to retrieve update bundles and catalogs.
The SBE Download Connector that runs on the Azure Local instance must periodically connect to Internet resources to enable Download Connector to download SBE bundles for your instance. The following table lists the outbound connectivity that is required:
Outbound connectivity for SBE Download Connector. Outbound connectivity details for SBE Download Connector
You can apply solution updates to your Azure Local instance using the Dell Solutions Builder Extensions (SBE) package. You can update your instance either by:
Downloading offline solution updates
Discovering online solution updates and then applying the updates
You must ensure that:
You have a functioning Azure Local instance with Azure Stack HCI operating system, version 24H2. The instance is registered to Azure.
You have access to the online solution update package or offline solution update package download.
You can do these updates either by:
Using PowerShell
Using Azure Update Manager service from the Azure portal
NOTE:You must run the Get-SolutionUpdateEnvironment PowerShell command. If the SBE package (latest version is 4.0.0.0) is only partially installed, complete the installation by following the procedures that are outlined in Download Connector – Automated download of future SBE release > Installation in the Azure Local Dell Solution Builder Extensions Release Notes (Dell 2512) on GitHub.
Update SBE package using PowerShell (online)
The process for updating the SBE package using PowerShell in online mode can be used for both multi-machine or single-machineAzure Local instances.
To perform an online solution update, do the following:
Procedure
Depending on your deployment configuration, ensure that your Azure Local instance single-machine has or your multi-machines have good Internet connectivity.
To verify that the update service discovers the solution update, run the following command:
Get-SolutionUpdate | Format-Table DisplayName, State
To install the solution update, run the following command:
Get-SolutionUpdate | Start-SolutionUpdate
Updating SBE package using PowerShell (offline)
The process for updating the SBE package using PowerShell in offline mode can be used for both multi-machine or single-machine Azure Local instances.
CAUTION:Before proceeding, verify that sufficient space is available on the selected Cluster Shared Volume (CSV).
Azure Update Manager allows you to apply, view, and manage updates for your cluster node (also known as Azure Local instancemachine).
Before the updates start, Azure Update Manager checks the cluster readiness and lists available updates. You can also monitor the status of the updates that are being applied.
To identify and install updates, do the following:
Procedure
Go to Azure Update Manager. In the left panel, under Resources, click Azure Local.
Alternatively, you can perform the procedure by going to Azure Arc > Azure Local, and then clicking Azure Local ClusterUpdates.
Select the cluster from the list, and then click One-time update.
The Install Updates window appears and lists available updates.
Updates window
On the Check readiness tab, review the checks and their results. When verified, click Next.
On the Select updates tab, select the available update or updates that you want to install, and then click Next.
On the Review + install tab, verify the previously selected options, and then click Install.
To monitor the update progress, go to Azure Update Manager > Resources > Azure Local. Select your Azure Local Instance. In the left panel, under Operations > Updates, select History.
The cluster with the updated status appears.
To review updated status details for one or more Azure Local instances:
Find and select the update in the list with an Update status of In progress.
Review the results in the Download updates tab, and then click Next.
From the Install tab, review the updates in progress. When the updates are complete, you see results similar to the following figure:
NOTE:You must order AX nodes that are preconfigured for GPU integration, or converted for GPU use, including the required components.
Guidelines for installing GPU hardware
For deployed Azure Local instance, or Windows Server 2025 (or later instance before performing any GPU hardware changes, place the target machine into maintenance mode (pause and drain).
Use Dell Support to follow the platform-specific GPU installation procedure for your server model.
For model-specific GPU slot or riser matrices and riser configuration options, see the applicable Dell installation and service manual sections for your platform, including:
You can use Discrete Device Assignment (DDA) on supported GPUs so that the Azure Stack HCI and Windows Server 2025 and later operating system servers contain GPU-enabled clustered VMs.
The package contains the required driver for the virtual machine to use a GPU that is assigned through Discrete Device Assignment (DDA). With DDA (full device passthrough), you install the NVIDIA driver that enables GPU functionality in the guest virtual machine. In the DDA workflow, the NVIDIA guest driver is not required on the host. If no vendor display driver is installed, the host can show the GPU as a 3D Video Controller.
You can do DDA with either Windows Admin Center (WAC) or PowerShell. Dell Technologies recommends using WAC to reduce user error and to conform to best practices.
NOTE:Before configuring DDA, to make the GPU available for assignment to the virtual machine, you must disable and dismount the GPU from the host-management operating system.
If you are using Windows Admin Center (WAC) to configure GPU assignment, WAC automatically performs the required disable and dismount operations as part of the workflow, so you do not have to complete this step manually. This automation is one of the reasons that Dell Technologies recommends that you use WAC for GPU-related actions. For more information about configuring and performing a DDA, see Use GPUs with Discrete Device Assignment in clustered VMs.
When DDA is complete and the GPU is assigned to the virtual machine, install the NVIDIA guest driver inside the guest virtual machine so that the virtual machine can use the GPU.
NOTE:For Windows guests, the driver is in the Guest_Drivers folder of the archive and has an .exe extension.
When the guest driver is installed, your virtual machine is ready to use the DDA GPU. For NVIDIA software licensing requirements, modes, and license-server configuration guidance, see the NVIDIA Virtual GPU Software Client Licensing User Guide.
GPU partitioning
On the Azure Stack HCI or Windows Server 2025 or later operating-system servers, you can use GPU partitioning (GPU-P) for different workloads, such as artificial intelligence. To avoid mistakes and for a streamlined visual experience, Dell Technologies recommends that you use Windows Admin Center (WAC) for GPU-P.
Dell Technologies servers do not come with a GPU-P driver. The GPU-P driver requires separate licensing from NVIDIA. For more information about licensing options and the benefits of GPU-P, see: NVIDIA Virtual GPUs.
NOTE:For GPU-P to work, you must have both a host driver and a GPU-P enabled guest (VM) driver and the correct activated license.
Download and install host and guest drivers
For GPU partitioning (GPU-P) to work, you must have both a host driver and a GPU-P enabled guest (VM) driver and the correct activated license.
To download and install host and guest drivers, do the following:
Dell OpenManage Integration with Windows Admin Center
Overview of Dell OpenManage Integration with Windows Admin Center
Dell OpenManage Integration with Windows Admin Center (OMIMSWAC) enables IT administrators to manage the HCI that is created by using Dell AX System for Azure Local. OMIMSWAC simplifies the tasks of IT administrators by remotely managing the AX nodes and clusters throughout their life cycle.
In the upper left of Windows Admin Center, from the menu, select Cluster Manager.
In the Cluster Connections window, click the cluster name.
In the left pane of Windows Admin Center, under EXTENSIONS, click Dell OpenManage Integration.
Review the Dell Software License Agreement and Customer Notice, and select the checkbox to accept the terms of the license agreement.
Validate and remediate a cluster
By using the HCI Configuration Profile (HCP) Compliance feature, you can see the cluster compliance by using HCP checks, see the recommendations, and remediate noncompliant components.
Before you begin
Before you begin, the cluster:
Must be Dell AX System for Azure Local, version 24H2.
Nodes must have a valid Dell OpenManage Integration with Microsoft Windows Admin Center (OMIMSWAC) premium license installed.
To run an HCP compliance check in Dell OpenManage Integration extension, perform the following steps by selecting the single-node cluster in the Cluster Manager:
Procedure
Go to View > Compliance. When another menu appears, select HCP .
The Compliance Summary page appears. If the Check Compliance button is enabled, go directly to step 3.
If Check Compliance is disabled, ensure:
All the prerequisites are met.
Required inputs are provided in the Configure Cluster Settings tab.
If not, to save the settings for future use, choose the network topology and the deployment model, and then click Save. To generate compliance for Dell Operating System Configuration policies, the following settings are required:
Network topology
Fully-converged: All storage ports from the server are connected to the same network fabric. Within the host operating system, the NIC ports are used for both storage and management or VM traffic.
Non-converged-Physical: Storage traffic is on the physical storage NIC ports and management, or VM traffic goes through a SET that is created using network ports of the server rNDC.
Non-Converged-Set: Storage traffic uses virtual adapters in the host operating system that is connected to a SET.
Deployment model
Scalable model supports from 2 to 16 nodes in a cluster and uses top-of-rack (ToR) switches for management and storage traffic networking
Switchless model uses full mesh connections between the cluster nodes for storage traffic and supports from 2 to 4 nodes in a cluster
Stretched clusters with Azure Stack HCI operating system consist of nodes residing at two different locations or sites, with each site having two or more nodes, replicating volumes either in synchronous or asynchronous mode.
Place the files in C:\Users\Dell\HCPMetaData folder in the gateway system where Windows Admin Center is installed.
Run the HCP compliance check.
The Dell OpenManage Integration extension fetches the applicable policies, validates the cluster node attributes against the policy attributes, and displays the compliance summary.
To fix noncompliant policies, click Fix Compliance.
WARNING:Fix Compliance is disabled if Dell Hardware Symmetry Policy is noncompliant with a critical error. You are not allowed to remediate other policies.
Before proceeding to the next step, to resolve the error, review the recommendations, view the details, and then contact Dell.com/support if required. The critical error states that this aspect of node configuration is not supported. You must correct the issue before you can deploy a symmetric HCI cluster.
Manual Fixes include policies that require physical interventions and recommendations that can be remediated manually.
NOTE:Ensure that the cluster is compliant with Dell Hardware Symmetry Policy and Dell Operating System Configuration Policies, otherwise the cluster performance is not guaranteed.
Automatic Fixes include policies that can be remediated using the Dell OpenManage Integration extension.
To apply the configurations, if any of the policy fixes require a cluster reboot, choose the reboot option to apply the configurations by restarting your cluster in Cluster-Aware Updating mode.
Choose from:
Apply at Next Reboot: Immediately applies BIOS, NIC, and iDRAC attributes concurrently to all the cluster nodes and restarts the cluster in Cluster-Aware Updating mode.
Apply and Reboot Now: Applies BIOS, NIC, and iDRAC attributes concurrently to all the cluster nodes now and restarts the cluster
NOTE: If you choose to apply the changes at the next reboot, to apply the changes, ensure that you disable the infrastructure lock before the next reboot starts.
Click the Schedule Reboot checkbox to schedule the date and time when BIOS, NIC, and iDRAC attributes are applied concurrently to all the cluster nodes and restart the cluster in Cluster-Aware Updating mode.
If the infrastructure lock is enabled, a window appears to allow you to disable the lock and the proceed. To allow the Dell OpenManage Integration extension to automatically lock the infrastructure after the operation is complete, select Allow OMIMSWAC. This step re-enables the infrastructure lock after the operation is complete.
To trigger the updates, click Apply.
If Kernel Soft Reboot is enabled for the cluster, the Dell OpenManage Integration extension ignores this trigger and performs a full reboot to apply all BIOS-related settings. For more information, see When to use Kernel Soft Reboot.
The operation enables CredSSP. To improve the security, after the operation is complete, disable CredSSP.
To see the update status and progress at node level, click View Details.
After the status finishes, the Dell OpenManage Integration extension rechecks the compliance and displays the updated compliance summary.
To export the HCP Compliance report to a Microsoft Excel spreadsheet, which can be useful when contacting the Dell Technologies support team, click Export compliance summary.
View HCI compliance summary
Dell OpenManage Integration with Microsoft Windows Admin Center (OMIMSWAC) computes the compliance using different types of Dell HCI Configuration Profile policies that are mentioned and displays the report.
The following table provides information about each Dell policy:
Dell HCI Configuration Profile policies. The Dell HCI Configuration Profile policies table names and describes each policy.
Policy name
Description
Dell Infrastructure LockDown
Checks whether the HCI cluster infrastructure is locked.
Dell Hardware Symmetry
Checks whether cluster nodes have validated and supported hardware components and have symmetrical hardware configurations.
Checks whether cluster nodes have Dell Technologies recommended BIOS, NIC, and iDRAC configurations
Dell OS Configuration
Checks whether cluster nodes have Dell Technologies, and Microsoft recommended operating-system configurations
If the compliance summary is already generated, the last report is displayed with the timestamp. In this case, Re-Check Compliance is enabled.
To see the latest compliance report, click Re-Check Compliance.
For a brief description of the compliance summary sections, see the Details of Compliance summary sections table.
Policy Summary
Displays compliance of each cluster node and its components for each policy type. For a description of each policy type, see the Details of Policy Summary sections table.
The compliance summary is divided into several sections as described in the following table:
Details of Compliance summary sections. The compliance summary sections table lists and describes the sections.
Compliance summary section
Description
Overall Compliance
Displays the overall compliance of the cluster such as compliance percentage, number of policies compliant, and total number of policies from the displayed policy types
Overall Compliance State
Displays overall compliance of the cluster using a doughnut chart and color codes. The color codes indicate different compliance types. You can select different color codes, if any, to filter the respective policy details and its cluster nodes.
For example, when you select the red color code, policies that are not compliant and their respective cluster nodes are displayed.
For a description of each color code, see the Icons shapes and color codes for Overall Compliance State options table.
The table lists the Overall Compliance State options and provides a description of the relevant icon shape and color code for the compliant state options:
Icons shapes and color codes for Overall Compliance State options. The table lists the compliance state options and provides a description of the relevant icon shape and color code for the compliant state options:
Compliance state
Description and color code
Compliant
Displays that all cluster nodes are compliant with all Dell policies.
Icon is a checkmark in a green circle.
Errors
Displays if any clustermachine is not compliant with Dell Hardware Symmetry policy.
Icon is an exclamation mark in a red hexagon.
Warnings
Displays if any clustermachine is not compliant with any optional policies.
Icon is an exclamation mark in an orange triangle.
Unknown
Displays if any clustermachine inventory could not be retrieved when the machine is down or not reachable.
Icon is a question mark inside a gray circle.
The following table describes each section of the Policy Summary and what it contains:
Details of Policy Summary sections. The following table describes each section of the Policy Summary and what it contains.
Policy component
Description
Policy Name
Name of Dell Technologies policies
Description
Description of Dell Technologies policies
Overall Status
Displays overall status of compliance of the cluster for each policy type
Overall State
Displays how many policies are compliant out of the total number of policies and its percentage
Errors
Displays several policies that are noncompliant and must be fixed
Warnings
Displays several policies that are noncompliant and must be fixed
Unknown
Displays several unknown issues, or unable to run or fetch the data
Details
Displays additional information about each node and its components and their compliance status
Onboard Dell policies to Azure Arc from Windows Admin Center to monitor HCI clusters
In the Dell OpenManage Integration extension, you can deploy the Dell HCI Configuration Profile (HCP) policies onto Azure Arc, and then use these policies in Azure Arc to monitor your Azure Stack HCI clusters. This feature is supported for single-node HCI clusters.
Before you begin
The single-node HCI cluster must be Dell AX System for Azure Local, version 24H2.
Dell OpenManage Integration with Microsoft Windows Admin Center (OMIMSWAC) premium license must be installed on each cluster node.
To monitor the policies from Azure, the Internet must be available on Windows Admin Center and target nodes.
Ensure that you have the necessary permission to create, write, or read policies into Azure. Also, you must be a member of the Gateway users role.
Azure Stack HCI Cluster and WAC gateway must be registered on Azure and use the same account to sign in. For more information about Azure registration, see Register Windows Admin Center with Azure.
Cluster nodes must be Arc-enabled and onboarded to Azure Arc. See Azure Arc-enabled servers. Ensure that all nodes are registered to the same resource group.
In the cluster node, ensure that all RDMA enabled network adapters are connected to the same NIC ports as recommended by Dell Technologies. For more information, see the relevant deployment and operations guide at Technical Guides for Dell AX Solutions for Microsoft .
To deploy Dell HCP policies to Azure Arc, do the following steps:
Procedure
Sign in to Windows Admin Center.
From the All connections window, to connect to the cluster, select it.
From the left pane, under Extensions, click Dell OpenManage Integration, and then click View > Azure Integration.
OpenManage Integration checks the prerequisites. If all prerequisites are successful, a Sign In button appears.
If any prerequisites fail, a list of prerequisites with status and recommendations for failed prerequisites appears. Follow the recommendations to ensure that all prerequisites are successful before moving to the next step.
Click Sign In. A sign-in window opens to let you sign in to your Azure account. Specify your Azure subscription account details.
When signed-in, the button shows as Signed-in.
In the Onboarding Checklist section, the OpenManage Integration extension verifies and displays the list of checks and shows the recommendations if checklist items are not met.
Click Show Details to see the list of checklists, status, and recommendations if the checklists do not match. You cannot move to the next step until all the checklists are successful.
Click Refresh Checklist to see the checklist with the updated status.
For more information about the checklist, see Azure built-in roles in the Microsoft document.
In the Onboard Policies section, do the following:
To view the Azure account subscription details, click View Subscription Details.
To edit network topology, deployment model, and RDMA protocol for network direct technology, click Configure Cluster Settings, specify the details, and click Save to save the settings for future use. The policies are displayed based on your cluster settings. Once you save the settings, they are applied to all relevant features in OMIMSWAC. For more information about the settings, see the relevant deployment and operations guide at Technical guides for Microsoft HCI Solutions from Dell Technologies
NOTE:
For single node HCI cluster, Configure Cluster Settings option is not available.
Dell Technologies recommends that the resource group has no other Arc-enabled nodes that are not part of the current cluster.
Network Topology
Fully Converged: All storage ports from the server are connected to the same network fabric. Within the host operating system, the NIC ports are used for both storage and management/VM traffic.
Non-Converged-Physical: Storage traffic is on the physical storage network adapter ports, and management/VM traffic through a SET created using network ports of the server rNDC.
Non-Converged-Set: Storage traffic uses virtual adapters in the host operating system that is connected to a SET.
Deployment Model
Scalable model supports from 2 to 16 nodes in a cluster and uses top-of-rack switches for management and storage traffic networking.
Switchless model uses full mesh connections between the cluster nodes for storage traffic and supports from 2 to 4 nodes in a cluster.
Stretch cluster with Azure Stack HCI consists of servers residing at two different locations or sites, with each site having two or more servers, replicating volumes either in synchronous or asynchronous mode.
Network Direct Technology: This property is available only for Azure Stack HCI clusters using Intel E810 and E823 Network adapters. Choose the appropriate RDMA protocol, either iWARP or RoCEV2 that was used during the deployment. Based on this setting, appropriate network adapter policies are displayed for compliance.
If policies are not onboarded to Azure Arc, click Onboard Policies to see the details of the applicable Dell HCP policies for onboard and go to the next step.
The Onboard Dell HCI Configuration Profile policies for Azure window appears on the right side showing the available policies for onboarding or update. The window also shows the version of the previously onboarded policy, if any, and shows with a green dot the number of policies that are already onboarded. All mandatory policies are selected by default and cannot be changed. You can clear any optional policies. To onboard or update the onboarded policies, click Onboard.
After the policies are onboarded, the policy onboarding status appears next to the Onboard Policies button. Click View Details to see the Policy Onboarding Status page that displays the status of each policy that was onboarded to the Azure Arc.
To export the onboarded policies in a CSV format, click Export Details.
After the policies are successfully onboarded, log in to the Azure portal (Azure Arc) using the same subscription account to monitor your cluster using Dell HCP policies. In the Azure portal, click the Resource Groups to find the resources you want to monitor (Go to step 6 to find the resource group name in the view subscription details.)
Cluster node details are displayed.
To check the cluster compliance, click Policies under Settings.
The Policy page displays the cluster compliance and lists all the applicable policies including the default policies.
NOTE: Ignore the policy details of the "Dell Exempted Policy" as it only helps in tracking policy versions of onboarded Dell HCP policies and does not impact cluster performance or compliance.
To find the policies that are onboarded from the Dell OpenManage Integration extension, on the Search box, enter Dell. Select a policy to have a deeper look at the compliance for that particular policy. For more information about viewing compliance data in the Azure portal, see Microsoft Azure Policy documentation.
Secure connect gateway (SCG) is an enterprise monitoring technology that is delivered as an appliance and a stand-alone application. It monitors your devices and proactively detects hardware issues that may occur. Depending on your service contract, it also automates support request creation for issues that are detected on the monitored devices. When a hardware issue is detected, SCG automatically collects the telemetry that is required for troubleshooting the issue. The collected telemetry helps technical support to provide a proactive and personalized support experience.